Risk-Based Mindset: The Core of Modern Risk Management
Updated:
September 27, 2026
According to IBM, the average cost of a data breach in 2024 reached $4.88 million. With stakes this high, can any organization afford to take a reactive approach to risk?
At Bright Defense we strongly believe the key to staying ahead lies in adopting a risk-based mindset. This approach shifts the focus from just simply checking boxes to identifying, evaluating, and prioritizing real threats.
In this blog, we’ll break down what a risk-based mindset looks like and why it’s at the heart of effective, modern risk management.
Let’s jump right in!
What is a Risk-Based Mindset?
A risk-based mindset means using the likelihood and potential impact of harm to guide security decisions. Organizations identify threats and vulnerabilities affecting their systems, data, and operations, then assess which risks need attention first.
This approach helps teams choose safeguards, set remediation deadlines, and direct resources where they will have the greatest effect. A system that handles sensitive data, for example, may require stronger controls and faster action than a system with limited exposure.
In compliance work, risk guides priorities while every applicable legal, regulatory, and contractual requirement still applies. Teams document their assessments, decisions, and remaining risks to show how they manage them. That documentation can support a compliance review, but does not establish compliance on its own.
What is Modern Risk Management? And Why It Is Important?
Modern risk management is a proactive, data-driven approach that identifies, evaluates, and responds to risks in real time. It integrates technology, continuous monitoring, and cross-functional collaboration to address threats across cybersecurity, compliance, operations, and business strategy.
Unlike outdated models that rely on periodic reviews and rigid checklists, modern risk management adapts quickly to change, focusing on business impact and resilience.
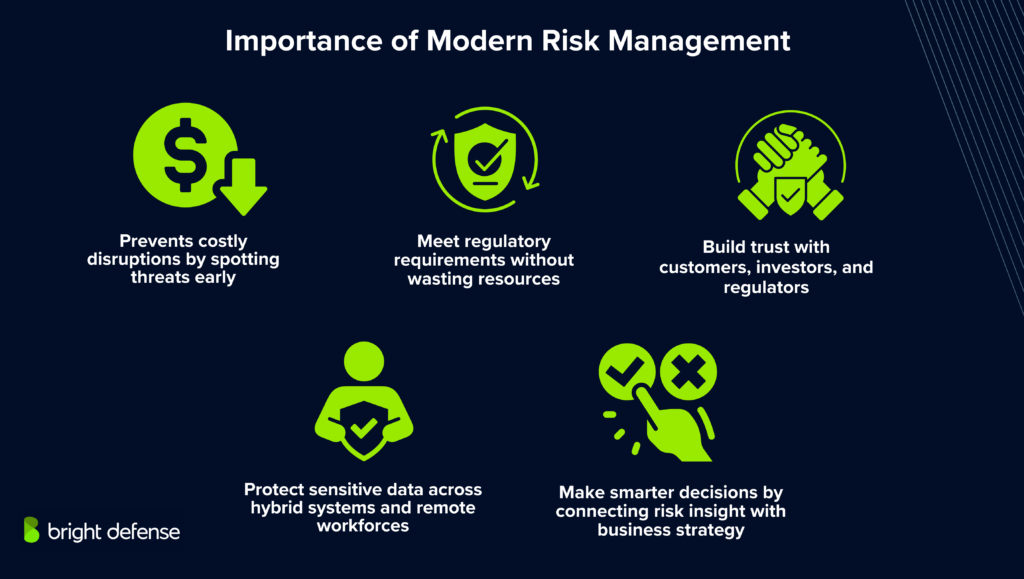
Modern risk management is critical because traditional methods can’t keep up with today’s fast-moving threats. Cyberattacks, regulatory shifts, supply chain disruptions, and reputational risks evolve constantly. A modern approach helps organizations:
- Prevent costly disruptions by spotting threats early
- Meet regulatory requirements without wasting resources
- Protect sensitive data across hybrid systems and remote workforces
- Build trust with customers, investors, and regulators
- Make smarter decisions by aligning risk insight with business strategy
Without modern risk management, organizations leave themselves exposed and reactive. With it, they stay ahead.
Why Adopt a Risk-Based Approach?
Benefits of a Risk-Based Approach
A risk-based approach helps organizations direct security work toward exposures that could cause the greatest harm to operations, people, or sensitive data. It gives decision-makers a consistent basis for setting priorities while they meet applicable compliance requirements.
The approach supports three practical decisions:
- Allocate Resources Where Risk Is Greatest: Direct staff time, budget, and remediation toward consequential exposures. In vendor risk management, for example, a provider with access to sensitive data may warrant more extensive review than one with no such access.
- Choose and Explain Risk Responses: Compare likelihood, impact, existing safeguards, and acceptable risk before deciding whether to reduce, avoid, transfer, or accept an exposure. Record the rationale and assign an owner for action.
- Reassess Priorities as Conditions Change: Review risks when systems, vendors, threats, or business operations change. Update safeguards and work plans as needed, while continuing to meet required controls and deadlines.
Update notes: Kept the three-part structure and repaired the existing internal link’s anchor. Replaced the implied promise of continued compliance with a specific requirement to keep meeting applicable controls and deadlines. The prioritization, risk response, and reassessment points follow NIST guidance.
Changing the Attitude Towards Risk-First
Most teams have been trained to chase feature delivery, speed, and innovation without first considering the consequences. Risk becomes an afterthought, addressed only when deadlines loom or incidents force a response. Shifting to a risk-first mindset demands that risk considerations come before everything else.
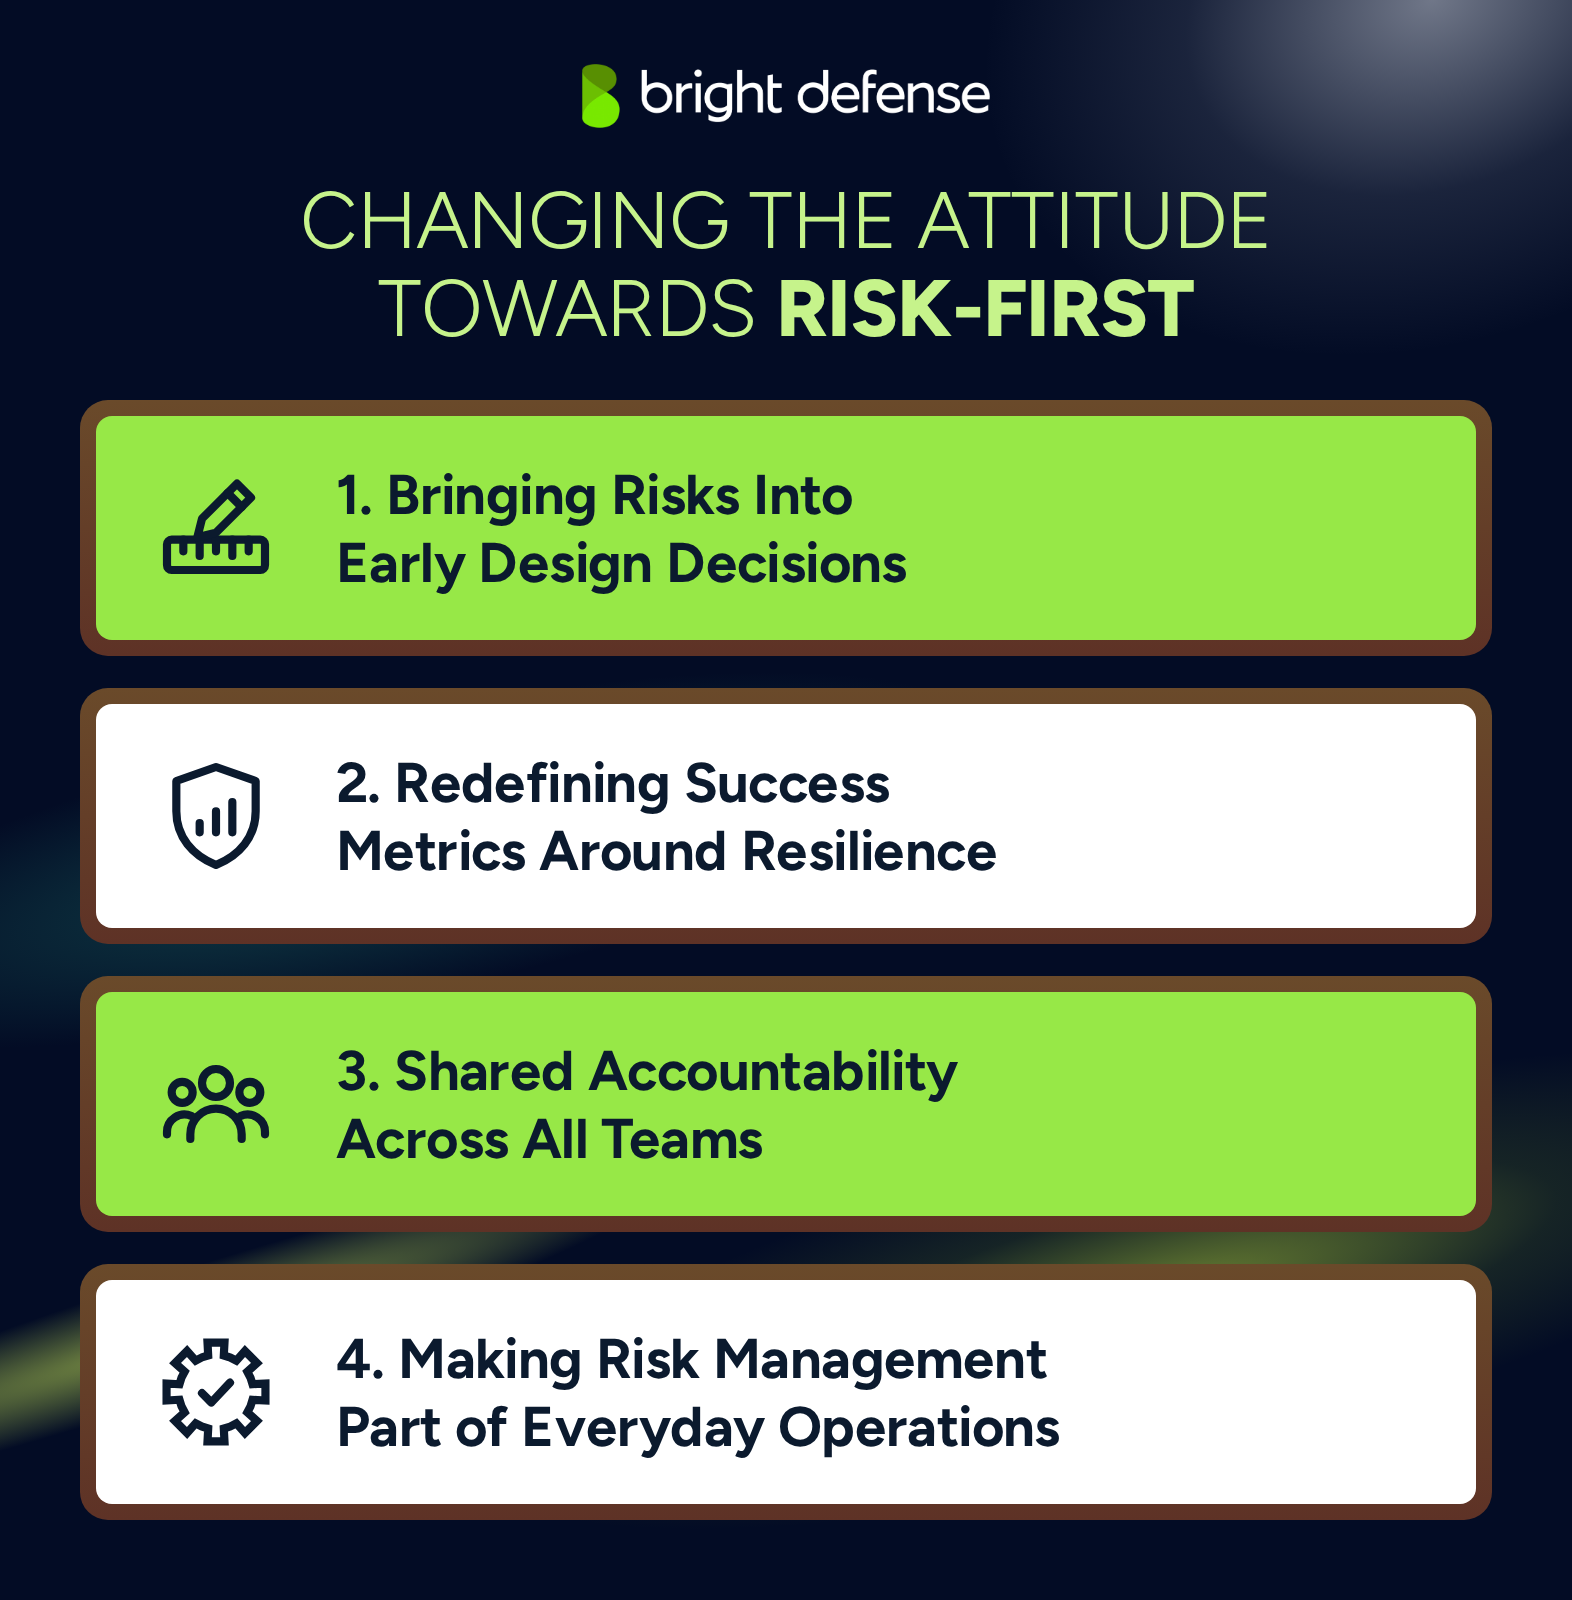
1. Bringing Risks Into Early Design Decisions
Rather than tacking on controls late, teams must treat potential security vulnerabilities, system failures, and insecure output as first-class concerns during initial planning.
Especially when building large language model applications, overlooking risks like direct prompt injection or insecure output handling can create gaps that attackers exploit. Stronger security postures form when risk shapes design choices from the beginning.
2. Redefining Success Metrics Around Resilience
A risk-first approach also reframes success. Teams do not measure progress solely by features shipped or deadlines met. Instead, they evaluate how well the work withstands critical security risks such as model denial of service or training data poisoning.
Teams that understand the importance of protecting training datasets, access logs, and backend systems build resilience into every layer of their work.
3. Shared Accountability Across All Teams
Responsibility cannot rest with security teams alone. Engineers, product managers, and data scientists all contribute to preventing data breaches and managing emerging threats. In doing so, they reduce the chances of service model denial attacks and improve overall llm security, without waiting for security flaws to surface during late-stage reviews.
4. Making Risk Management Part of Everyday Operations
Embedding risk-first thinking into everyday decisions creates organizations better prepared to handle the unique security challenges tied to llms and generative AI.
It shifts risk management away from isolated checkpoints and into the DNA of daily operations, preserving trust, protecting personally identifiable information, and supporting more durable innovation.
Implementing a Risk-Based Approach to Compliance
A risk-based approach to compliance identifies where an organization is most likely to fall short of its obligations and where the consequences would be greatest. It helps teams prioritize assessments and improvements while meeting every applicable requirement.
Organizations can apply this approach in six steps:
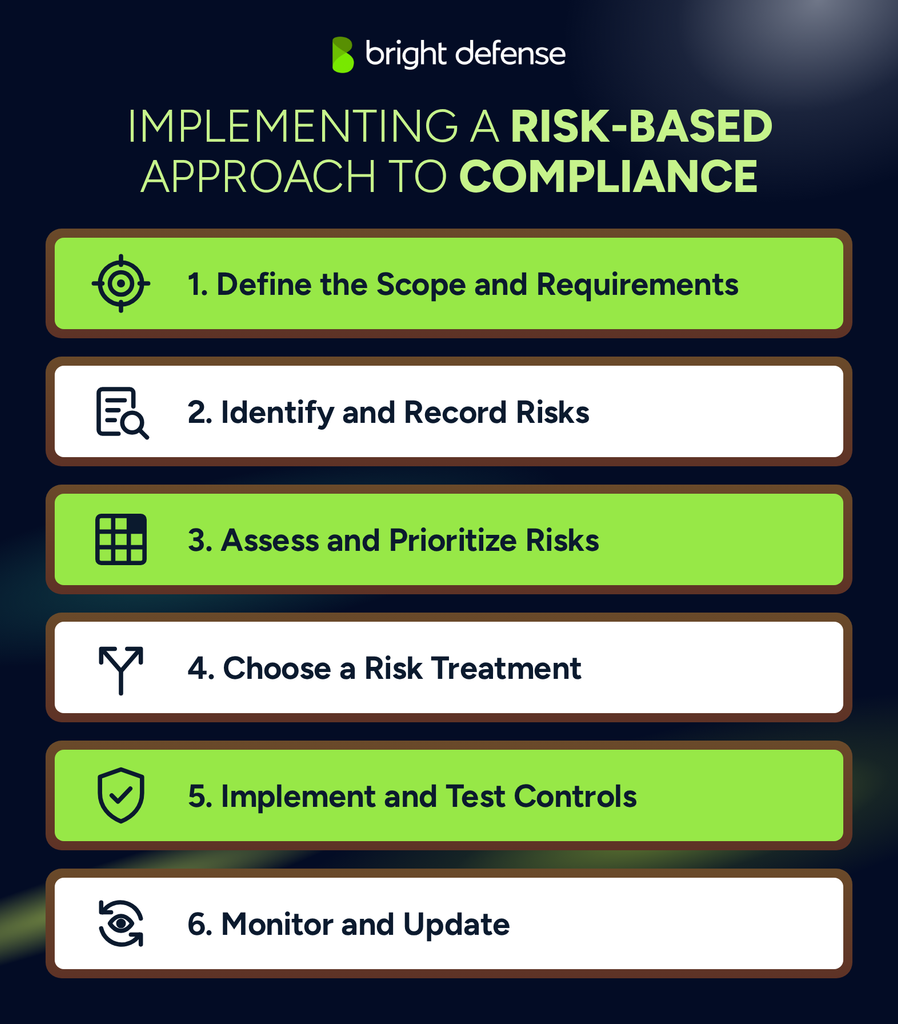
1. Define the Scope and Requirements
Identify the applicable laws, contracts, and frameworks, such as HIPAA, SOC 2, or ISO 27001. Document the systems, data, processes, and third parties within scope. Assign owners and establish how the organization will evaluate and approve risk decisions.
2. Identify and Record Risks
Review where processes or safeguards could fail to meet those requirements. Use audit findings, incidents, system reviews, and third-party assessments to identify gaps. Third-party exposure deserves attention: Verizon’s 2026 Data Breach Investigations Report found that third parties were involved in 48% of breaches in its dataset. About Verizon
Record each risk, its cause, affected requirement or asset, existing controls, and owner in a risk register.
3. Assess and Prioritize Risks
Rate each risk using a consistent method for likelihood and impact. Consider how well existing controls reduce the exposure, then document the reasoning behind the rating. A scoring matrix can help, but its size matters less than applying it consistently.
External figures can provide context without replacing an organization’s own assessment. IBM’s 2026 study of 602organizations that experienced breaches found a global average breach cost of $4.99 million. The potential impact for a particular organization depends on its systems, data, and circumstances. newsroom.ibm.com
4. Choose a Risk Treatment
Decide whether to reduce the risk, avoid the activity creating it, share some of its financial impact, or accept the remaining risk. Document the decision, its owner, and any planned actions or deadlines. Sharing or accepting a risk does not remove the responsibility to meet an applicable requirement.
5. Implement and Test Controls
Carry out the treatment plan and check whether the controls operate as intended. Depending on the risk, measures may include access reviews, vendor oversight, staff training, technical safeguards, or revised procedures. Retain policies, review records, test results, and other evidence showing how the relevant requirements are met.
6. Monitor and Update
Review risks and controls at a frequency appropriate to their importance. Reassess them when systems, vendors, business activities, or requirements change. Track control failures and overdue actions, then update the risk register and treatment plan when the organization’s exposure changes.
Challenges of a Risk-Based Approach to Compliance
A risk assessment can help an organization decide where to focus its effort. Problems arise when ratings are inconsistent, decisions lack evidence, or teams treat a low score as permission to ignore a requirement.
The main challenges are:
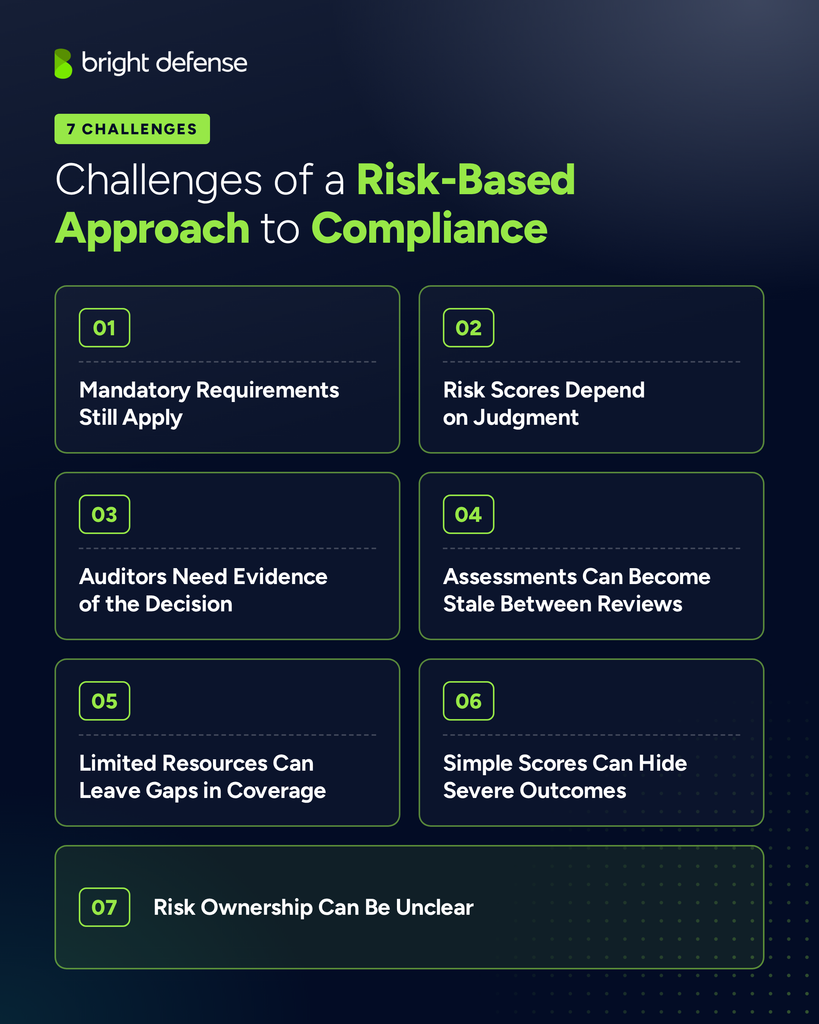
1. Mandatory Requirements Still Apply
A low risk rating does not remove a legal, regulatory, or contractual obligation. Teams should identify applicable requirements before deciding which additional safeguards deserve the most attention.
Frameworks differ in what can be tailored. ISO 27001 permits an organization to justify why an Annex A control is unnecessary in its Statement of Applicability, but its management system requirements cannot be excluded. A decision to omit a control needs to follow the framework’s rules, not just an internal score. committee.iso.org
2. Risk Scores Depend on Judgment
Two teams can assess the same risk differently, even when both use likelihood and impact. A simple score can create false confidence when the team has limited data or uses broad rating categories. It can also distort priorities: some teams rate risks low to avoid costly work, while others rate nearly everything high because no one wants to defend a lower rating.
Define what each rating means, record the assumptions behind it, and review unusual or disputed scores. NIST SP 800-30 provides a structured approach to conducting and maintaining risk assessments; it does not remove the need for judgment.
3. Auditors Need Evidence of the Decision
A risk register entry that says “low risk” rarely explains why a control was omitted or a treatment was delayed. For a SOC 2 examination or ISO 27001 audit, teams need to show what they assessed, which requirements applied, who approved the decision, and what controls address the remaining risk.
Keep the assessment, scope, control mapping, approval, and supporting evidence together. ISO 27001’s Statement of Applicability, for example, records necessary controls and justifications for excluding Annex A controls.
4. Assessments Can Become Stale Between Reviews
A new vendor, system, data flow, or customer requirement can change the risk picture before the next scheduled assessment. In Verizon’s 2026 Data Breach Investigations Report, third parties were involved in 48% of the breaches in its dataset, up from 30% in the prior report. That finding makes vendor changes a practical trigger for reviewing assumptions and controls.
Set a review schedule and require an earlier review when a material change occurs. The trigger should be part of the change or vendor approval process so it does not depend on someone remembering to update the risk register.
5. Limited Resources Can Leave Gaps in Coverage
Risk-based work still takes people to identify risks, assign owners, test controls, and maintain evidence. A small team may struggle to do all four consistently.
Prioritize deeper testing and remediation in higher-risk areas, while keeping a clear inventory of required controls and their owners. This directs limited effort without losing track of obligations that still need to be met.
6. Simple Scores Can Hide Severe Outcomes
Likelihood multiplied by impact can understate a rare event if the impact scale is capped or reviewers underestimate the consequences. A major data exposure or prolonged service loss may deserve leadership attention even when its calculated score is moderate.
Define separate escalation criteria for outcomes the organization cannot readily absorb. Record those thresholds in the risk appetite statement and require senior review before accepting a risk that crosses them.
7. Risk Ownership Can Be Unclear
Security, compliance, legal, and business leaders may disagree about treatment cost or acceptable exposure. When no one has authority to accept a risk, decisions stall; when anyone can accept it, accountability becomes weak.
Assign each risk a business owner, identify who advises on compliance obligations, and specify who can approve acceptance at each severity level. Record the decision and a date for reviewing it.
Final Thoughts
A risk-based approach helps organizations focus on the most important risks first. It allows teams to allocate resources based on actual threat levels and maintain compliance with regulatory requirements.
Regular risk evaluation keeps compliance strategies current and aligned with business goals. A deliberate and organized risk management process strengthens operational stability, protects critical assets, and improves overall resilience.
Add Bright Defense as a Preferred Source on Google