CMMC 2.0 Final Rule: Key Updates for Defense Contractors
Updated:
September 28, 2026
The CMMC 2.0 final rule establishes three assessment levels for protecting sensitive defense information. Published on October 15, 2024, and effective December 16, 2024, the program rule defines security requirements, assessment procedures, and continuing compliance obligations for Federal Contract Information (FCI) and Controlled Unclassified Information (CUI).
A separate acquisition rule took effect on November 10, 2025, beginning the phased introduction of CMMC requirements into applicable DoD contracts.
The transition to Phase 2 was suspended on July 13, 2026. Phase 1 self-assessment requirements remain in effect, along with underlying cybersecurity obligations. Contractors should confirm current requirements in their solicitations and contracts rather than rely on the original 2028 rollout target.
This guide explains the final rule’s assessment levels, contractor responsibilities, and implementation updates to help businesses plan their compliance work.
CMMC 2.0 Definition and Requirements
CMMC 2.0 is the Department of Defense’s cybersecurity assessment program for verifying how contractors and subcontractors protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). It replaces the original five-level model with three levels: Foundational, Advanced, and Expert.
The three levels use different security requirements and assessment methods under the program rule.
| CMMC Level | Security Requirements | Assessment Method |
|---|---|---|
| Level 1: Foundational | Protects FCI through 15 safeguarding requirements in FAR clause 52.204-21. | Requires an annual self-assessment. |
| Level 2: Advanced | Protects CUI through 110 requirements from NIST SP 800-171 Revision 2. | Provides self-assessment and C3PAO certification assessment routes, generally on a three-year cycle. |
| Level 3: Expert | Adds 24 selected NIST SP 800-172 requirements to the Level 2 foundation. | Requires a government-led DIBCAC assessment every three years and a prerequisite Final Level 2 C3PAO status. |
Each level requires annual affirmation of continuing compliance. Contractors should confirm their required level and CMMC assessment obligations from applicable solicitations and contracts.
Contract implementation began on November 10, 2025. The transition to Phase 2 was suspended on July 13, 2026, leaving Phase 1 self-assessment requirements in effect. The suspension does not remove underlying obligations to protect FCI and CUI.
Key Changes Under CMMC 2.0
CMMC 2.0 replaces the original five-level model with three levels, expands self-assessment options, and introduces conditional compliance under defined restrictions. The following seven updates explain the framework changes and current implementation status.
1. Three Compliance Levels
CMMC 2.0 removes the original transitional levels and establishes three levels based on the information and security requirements specified for the contract.
| Level | Security Requirements |
|---|---|
| Level 1: Foundational | Protects Federal Contract Information (FCI) through 15 FAR 52.204-21 safeguarding requirements, organized into 17 CMMC practices. |
| Level 2: Advanced | Protects Controlled Unclassified Information (CUI) through 110 NIST SP 800-171 Revision 2 requirements. |
| Level 3: Expert | Adds 24 selected NIST SP 800-172 requirements to the Level 2 foundation to address advanced persistent threats. |
Level 3 protects CUI associated with designated defense programs. It does not establish requirements for handling classified information.
2. Removal of CMMC-Specific Requirements and Maturity Ratings
CMMC 2.0 removes the additional requirements and separate process maturity ratings introduced under CMMC 1.0. Level 2 uses NIST SP 800-171 Revision 2 directly, while Level 3 adds selected NIST SP 800-172 requirements.
Policies, procedures, training, and documentation remain necessary where applicable. Assessors evaluate whether requirements are implemented and supported by evidence.
3. Different Assessment Routes
The program rule establishes different assessment methods and renewal periods for each level.
| Level | Assessment Route Under the Program Rule |
|---|---|
| Level 1 | Requires an annual self-assessment, with results submitted through the Supplier Performance Risk System (SPRS). |
| Level 2 | Provides self-assessment and authorized C3PAO certification assessment routes, generally every three years. |
| Level 3 | Requires a government-led DIBCAC assessment every three years, following Final Level 2 C3PAO status for the applicable scope. |
All levels require an affirmation of continuing compliance after applicable assessments and annually thereafter. Contractors cannot select a less demanding assessment route based solely on their budget or company size.
4. Final Rules and a Paused Phase 2 Rollout
The CMMC program rule was published on October 15, 2024, and took effect on December 16, 2024. The separate acquisition rule took effect on November 10, 2025, beginning contractual implementation.
The transition to Phase 2 was suspended on July 13, 2026. The program remains in Phase 1, with Level 1 and Level 2 self-assessment requirements continuing. Contractors should verify current solicitation and contract requirements instead of relying on the original 2028 implementation target.
5. Conditional Status With Restricted POA&Ms
Plans of Action and Milestones (POA&Ms) can support conditional status at Levels 2 and 3 only when specified scoring and requirement restrictions are satisfied. Level 1 does not permit outstanding requirements on a POA&M.
Conditional Level 2 requires a score of at least 88 out of 110, with only eligible deficiencies remaining. Qualifying gaps must pass a closeout assessment within 180 days of the conditional status date. A remediation promise alone does not establish eligibility.
6. Limited Government Waiver Authority
Authorized DoD acquisition officials can waive inclusion of CMMC requirements in a solicitation or contract under limited circumstances. Contractors cannot treat a waiver as a routine alternative to preparation or obtain one simply because compliance is expensive.
A CMMC waiver leaves applicable cybersecurity and information protection obligations in place, including relevant FAR and DFARS requirements.
7. Self-Assessments Reduce Some Assessment Expenses
Self-assessment options remove the need to purchase a C3PAO assessment where that route applies. Businesses still need to fund staff time, security improvements, documentation, evidence collection, and ongoing maintenance.
Actual costs depend on assessment scope, existing safeguards, and remediation needs. The revised model does not guarantee low-cost compliance or remove responsibility for protecting FCI and CUI.
Estimated Percentage of Defense Contractors at Each CMMC Level
The DoD’s 2024 final rule projected that roughly 63% of covered entities would require CMMC Level 1, 36% Level 2, and 1% Level 3. These figures describe the rule’s planning estimates, rather than measured participation or current certification rates.
The following percentages are calculated from the rule’s estimated population of 221,286 entities.
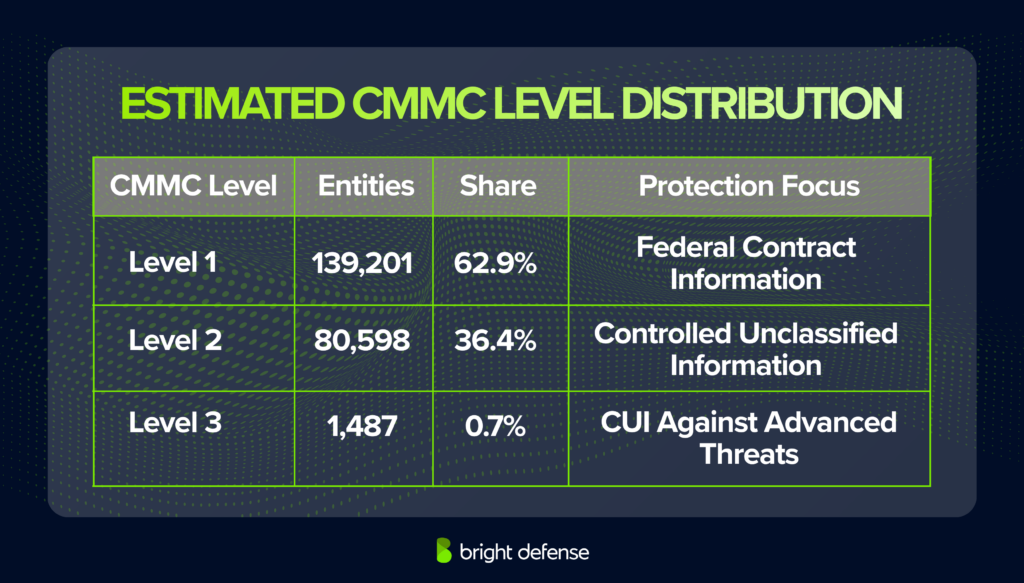
The Level 2 estimate combines 4,000 entities projected for self-assessments and 76,598 projected for C3PAO assessments. Level 3 assessments are government-led and conducted by the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC).
These projections predate the July 2026 suspension of the Phase 2 transition. Contractors should determine their obligations from current solicitation and contract requirements.
CMMC 2.0 Rollout Timeline and Current Status
CMMC implementation began on November 10, 2025, and remains paused in Phase 1 following the July 13, 2026 suspension of the Phase 2 transition. The original plan introduced four phases over three years, but its later milestones should no longer be presented as confirmed implementation dates.
| Phase | Original Start Date | Planned Requirements and Current Status |
|---|---|---|
| Phase 1 | November 10, 2025 | Introduces Level 1 and Level 2 self-assessment requirements for applicable contract awards. These requirements remain in effect. |
| Phase 2 | November 10, 2026 | Expands Level 2 C3PAO assessment requirements for applicable awards. The transition is suspended. |
| Phase 3 | November 10, 2027 | Expands Level 2 certification requirements to applicable contract options and introduces Level 3 requirements more broadly. The original date is subject to changes following the suspension. |
| Phase 4 | November 10, 2028 | Extends CMMC requirements to all applicable solicitations and contracts, including option periods. The original date is subject to changes following the suspension. |
Contractors must continue meeting applicable safeguarding, self-assessment, reporting, and annual affirmation requirements. The pause does not remove existing obligations to protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). Preparation should follow current solicitation and contract requirements.
The Importance of Third-Party Assessments
Third-party CMMC assessments provide independent verification that contractors have implemented required safeguards for Controlled Unclassified Information (CUI).
Assessors examine evidence, interview personnel, and test controls against defined assessment objectives. Written policies alone do not demonstrate that safeguards operate effectively.
Under the CMMC program rule, authorized CMMC Third-Party Assessment Organizations (C3PAOs) conduct Level 2 certification assessments against 110 NIST SP 800-171 Revision 2 requirements.
Level 2 self-assessments evaluate the same requirements, with the contractor responsible for evaluating and reporting its implementation.
The transition to Phase 2 was suspended on July 13, 2026. Current guidance keeps the program in Phase 1 and permits Level 1 and Level 2 self-assessment requirements. Contractors must continue meeting applicable security obligations and verify their assessment requirements before commissioning certification work.
Level 3 follows a separate government-led assessment process through the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC). Under the program rule, this assessment evaluates 24 additional requirements and requires prior Final Level 2 C3PAO status covering the applicable scope.
Independent assessment provides greater assurance about implemented safeguards. Maintaining those safeguards, correcting deficiencies, and keeping evidence current remain continuing contractor responsibilities.
CMMC 2.0 Rollout and Timeline
CMMC contractual implementation began on November 10, 2025, and remains in Phase 1 following the July 13, 2026 suspension of the Phase 2 transition. The program rule took effect earlier, on December 16, 2024.
Phase 1 self-assessment requirements and underlying cybersecurity obligations remain in force. Contractors should follow their applicable solicitation and contract requirements; there is no blanket requirement for every new defense contract to require CMMC certification in 2026.
Preparing for CMMC 2.0 Compliance
Preparing for CMMC 2.0 starts with confirming contractual requirements, defining the assessment scope, and evaluating existing safeguards.
Contractors should document where Federal Contract Information (FCI) or Controlled Unclassified Information (CUI) is handled, correct security gaps, and gather evidence that applicable requirements are met. Official CMMC scoping and assessment guides support this work, while eligible businesses can access government cybersecurity assistance.
Phase 1 self-assessment requirements remain in effect during the Phase 2 suspension, making accurate assessments and continuing compliance immediate priorities.
Conclusion: The Path Forward for Defense Contractors
CMMC 2.0 requires contractors to demonstrate that applicable safeguards protect sensitive defense information. The Phase 2 suspension leaves Phase 1 self-assessment requirements and underlying security obligations in place. Contractors should confirm their required level, correct security gaps, and maintain evidence that supports their compliance claims.
Contact Bright Defense for help with CMMC readiness assessments, remediation planning, and ongoing compliance support.
How Bright Defense Can Help with CMMC 2.0 Compliance
Bright Defense helps defense contractors prepare for and maintain CMMC Level 1 and Level 2 compliance through gap assessments, remediation support, compliance automation, and ongoing security guidance. Its services help organizations document their safeguards and prepare evidence for the applicable assessment.
Bright Defense provides support in four areas:
- Continuous Compliance Plans: Sentry, Guardian, and Defender provide different service packages combining compliance automation and security guidance. Organizations should confirm which monitoring, assessment, and remediation activities their selected engagement includes.
- Gap Analysis and Remediation: Bright Defense reviews existing safeguards against applicable requirements, documents deficiencies, and helps prioritize corrective work. Findings support a practical plan for implementing controls and gathering evidence.
- Assessment Preparation: The team helps organizations prepare for CMMC Level 1 and Level 2 requirements, including documentation, self-assessment support, and certification assessment readiness where applicable.
- PreVeil CUI Enclave Support: Bright Defense helps deploy PreVeil for encrypted email and file collaboration within a CUI enclave. An enclave can limit CUI exposure and reduce assessment scope when properly designed. Compliance still depends on the surrounding systems, operating procedures, and required safeguards.
Contact Bright Defense to discuss your required CMMC level, existing environment, and preparation priorities.
FAQs
1. What Is the Purpose of CMMC 2.0?
CMMC 2.0 verifies that defense contractors and subcontractors implement required safeguards for Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). The program connects cybersecurity assessment results and continuing compliance obligations to applicable DoD contracts.
2. How Many Compliance Levels Does CMMC 2.0 Have?
CMMC 2.0 replaces the original five-level model with three levels.
| Level | Protection Requirements |
|---|---|
| Level 1: Foundational | Protects FCI through basic safeguards and requires annual self-assessments. |
| Level 2: Advanced | Protects CUI through 110 NIST SP 800-171 Revision 2 requirements. The program rule provides self-assessment and C3PAO assessment routes. |
| Level 3: Expert | Adds 24 selected NIST SP 800-172 requirements and requires government-led DIBCAC assessments following Final Level 2 C3PAO status. |
3. When Did CMMC 2.0 Take Effect?
The program rule took effect on December 16, 2024. Contractual implementation began on November 10, 2025. The Phase 2 transition was suspended on July 13, 2026, leaving Phase 1 self-assessment requirements in effect. Contractors should confirm their obligations in current solicitations and contracts.
4. What Are POA&Ms, and How Do They Affect CMMC Status?
A Plan of Action and Milestones (POA&M) documents security deficiencies and corrective work. Levels 2 and 3 permit conditional status only under specific scoring and requirement restrictions. Eligible deficiencies must pass a closeout assessment within 180 days of the conditional status date. Level 1 does not permit POA&Ms.
5. Do All Contractors Need Third-Party CMMC Assessments?
Third-party assessments are not required for every contractor. Level 1 uses self-assessments. The program rule includes Level 2 C3PAO assessments and government-led Level 3 DIBCAC assessments. During the current Phase 1 pause, official guidance permits only Level 1 and Level 2 self-assessment requirements.
6. How Can Contractors Prepare for CMMC Compliance?
Preparation involves confirming the required level, defining the assessment scope, evaluating safeguards, correcting deficiencies, and gathering evidence. Use the requirements applicable to your level. Bright Defense can assess your CMMC readiness and help plan remediation and assessment preparation.
7. Have the CMMC Rules Been Finalized?
Both the program rule and the associated acquisition rule have been finalized. The CMMC program final rule was published on October 15, 2024. The acquisition rule was published on September 10, 2025. The subsequent Phase 2 suspension changes implementation without removing underlying safeguarding obligations.
8. What Is the Current Version of CMMC?
CMMC 2.0 remains the current three-level model. Level 2 assessments use NIST SP 800-171 Revision 2. Publication of a newer NIST revision does not automatically change the requirements incorporated into the CMMC program.
9. Is Microsoft GCC Required for CMMC Compliance?
CMMC does not mandate Microsoft GCC, GCC High, or any particular cloud vendor. External cloud services handling covered defense information under DFARS 252.204-7012 must meet FedRAMP Moderate-equivalent security requirements and applicable incident-response obligations. The specific service, configuration, data restrictions, and contract requirements determine suitability.