ISO 27001 vs SOC 2 – Whats the Difference
Updated:
October 12, 2026
ISO 27001 and SOC 2 help organizations demonstrate their security practices, but they provide different forms of assurance.
ISO 27001 sets requirements for an information security management system (ISMS), against which an organization can achieve certification. SOC 2 produces an independent attestation report on a service organization’s controls.
Choosing between ISO 27001 and SOC 2 starts with the assurance your customers require, the systems you need to cover, and the resources available to maintain compliance. Some organizations need ISO 27001 certification, others need a SOC 2 report, and some need both.
This guide compares ISO 27001 versus SOC 2 across requirements, audit processes, costs, timelines, and ongoing obligations to help you decide which to pursue first and when combining them makes sense.
What Is ISO 27001?
ISO 27001 is an international standard for establishing, maintaining, and improving an information security management system (ISMS). Developed jointly by ISO and IEC, it helps organizations manage risks to the confidentiality, integrity, and availability of information.
An independent certification body audits the ISMS against the standard’s requirements. Certification applies to a defined scope, which buyers should check to confirm it covers the services they use.
96,709 Valid ISO 27001 Certificates Covered 179,877 Sites Worldwide in the ISO Survey 2024, Demonstrating Its Adoption Across Organizations and Locations
What Is SOC 2?
SOC 2 is an AICPA examination and reporting framework for evaluating a service organization’s controls. An independent CPA firm issues an attestation report covering security and any additional Trust Services Criteria included in the engagement: availability, processing integrity, confidentiality, or privacy.
A Type 1 report evaluates control design at a specified date. A Type 2 report evaluates design and operating effectiveness over a specified period. ISO 27001 provides ISMS certification, while SOC 2 provides a detailed report on controls within the examined system.
About 70% of Drata Customers Hold a SOC 2 Attestation, According to the Company’s SOC 2 By the Numbers Analysis of Thousands of Active Accounts.
What Are The Differences Between ISO 27001 And SOC 2?
ISO 27001 evaluates an organization’s information security management system, while SOC 2 evaluates controls within a defined service organization system. The main differences concern audit requirements, scope, deliverables, and ongoing assessment.
The following are the key differences:
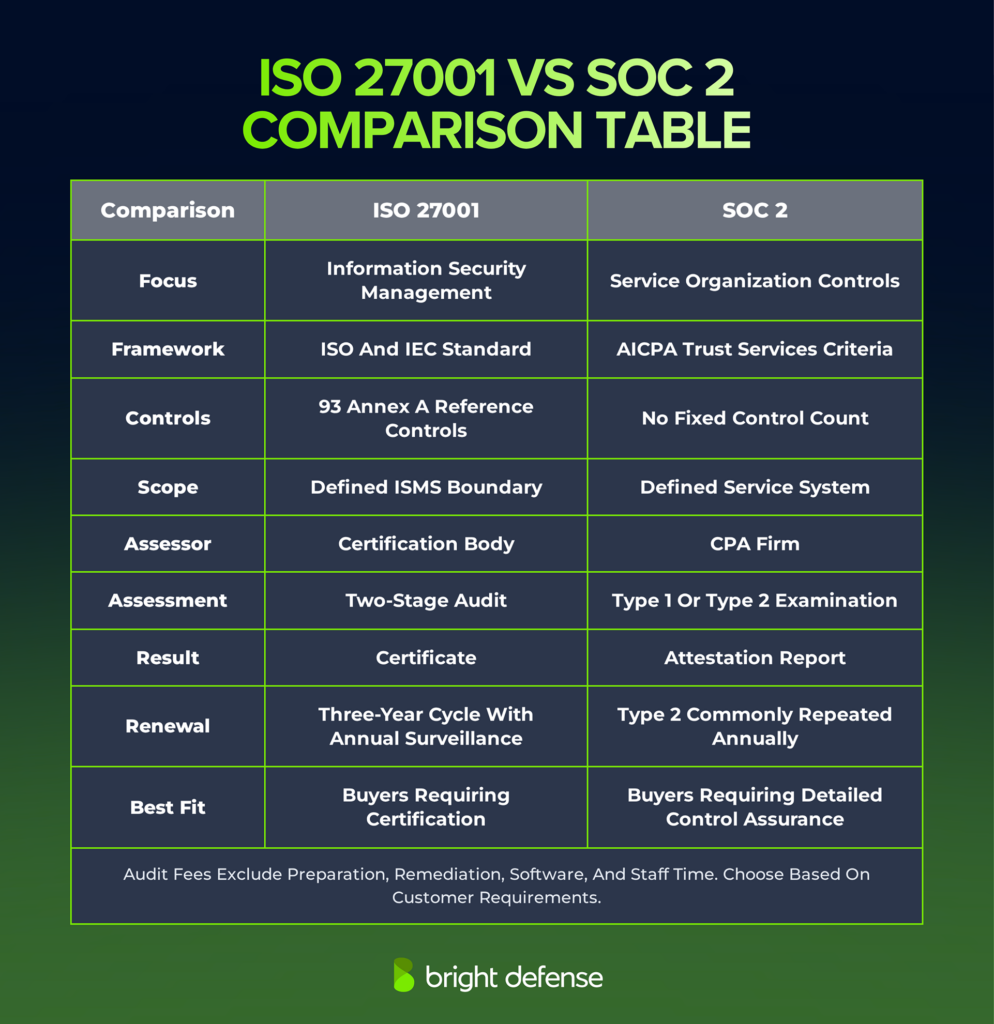
Audit fees exclude preparation, remediation, software, and internal staff time. Customer requirements determine which assurance to pursue.
Compliance Requirements And Control Selection
ISO 27001 requires organizations to meet the management system requirements in Clauses 4–10. These cover leadership, risk management, internal audits, management reviews, and continual improvement.
Its Annex A contains 93 reference controls. Organizations determine necessary controls through risk assessment and treatment, then justify their selections and exclusions in a Statement of Applicability. They can include additional controls where needed.
SOC 2 uses the AICPA’s Trust Services Criteria. Security is required; availability, processing integrity, confidentiality, and privacy are included according to the engagement’s scope.
Organizations design controls to meet the applicable criteria, with no universal requirement to implement 70–150 controls.
23% of SOC 2 reports reviewed in CBIZ’s 2024 benchmark study contained more than 150 security controls. This illustrates how control counts vary between engagements and reinforces the need to select controls around actual risks and requirements.
Audit Scope
ISO 27001 certification covers a defined ISMS scope, which can encompass an entire organization or particular services, locations, and business units. SOC 2 covers a described system used to deliver services, including its supporting people, processes, technology, and data.
Either scope can be narrow or extensive. Buyers should confirm that the certificate or report covers the service they intend to purchase.
75.3% of the 73 SOC 2 reports reviewed in CBIZ’s 2024 benchmark study included availability, while 64.4% included confidentiality. These findings show how organizations extend their examination scope to address additional service commitments.
Customer And Market Requirements
ISO 27001 has international recognition across industries. SOC 2 is frequently requested during vendor reviews involving North American technology and service providers.
Customer requirements provide the stronger decision rule. Confirm whether buyers accept ISO 27001, require a SOC 2 Type 2 report, or expect both before committing to an audit.
51% of respondents in the Association of Corporate Counsel’s 2025 cybersecurity survey say their organizations ask vendors for proof of certification or assurance, with SOC 2 and ISO 27001 listed as examples. This supports confirming buyers’ requirements before choosing an engagement.
Audit Process And Assessor
ISO 27001 certification involves a certification body conducting a two-stage audit. Stage 1 reviews the ISMS documentation and readiness; Stage 2 evaluates implementation and effectiveness.
SOC 2 examinations are performed by independent CPA firms. Type 1 evaluates control design at a specified date. Type 2 evaluates design and operating effectiveness throughout a specified period.
Certificate Versus Attestation Report
ISO 27001 produces a certificate identifying the certified organization, ISMS scope, and validity dates. Detailed findings appear in audit records rather than on the certificate.
SOC 2 produces a report containing the auditor’s opinion, management’s assertion, and system description. Type 2 includes control tests and their results, including exceptions. Our SOC 2 report example shows how these sections fit together.
Preparation And Audit Timeline
Both timelines depend on existing controls, scope, evidence quality, and assessor availability. ISO 27001 preparation includes establishing the ISMS, completing an internal audit and management review, and addressing gaps before certification.
SOC 2 Type 2 adds an examination period commonly lasting 3–12 months, followed by any remaining testing and report preparation. This period is separate from initial readiness work. Our SOC 2 timeline guide explains the stages.
Costs And Ongoing Assessments
Neither approach is consistently cheaper. Compare audit fees alongside remediation, software, consulting, and internal staff time. Scope, organizational complexity, locations, and report type influence the total cost.
ISO 27001 generally follows a 3-year certification cycle with annual surveillance audits and recertification before expiry. Organizations conduct ISO 27001 internal audits at planned intervals.
SOC 2 reports cover a specified date or period. Customers commonly request a new Type 2 report annually to maintain current assurance.
What Do ISO 27001 And SOC 2 Have In Common?
ISO 27001 and SOC 2 help organizations manage information security risks and provide independent assurance to customers. Their requirements overlap in several areas, allowing organizations pursuing both to reuse relevant controls and evidence.
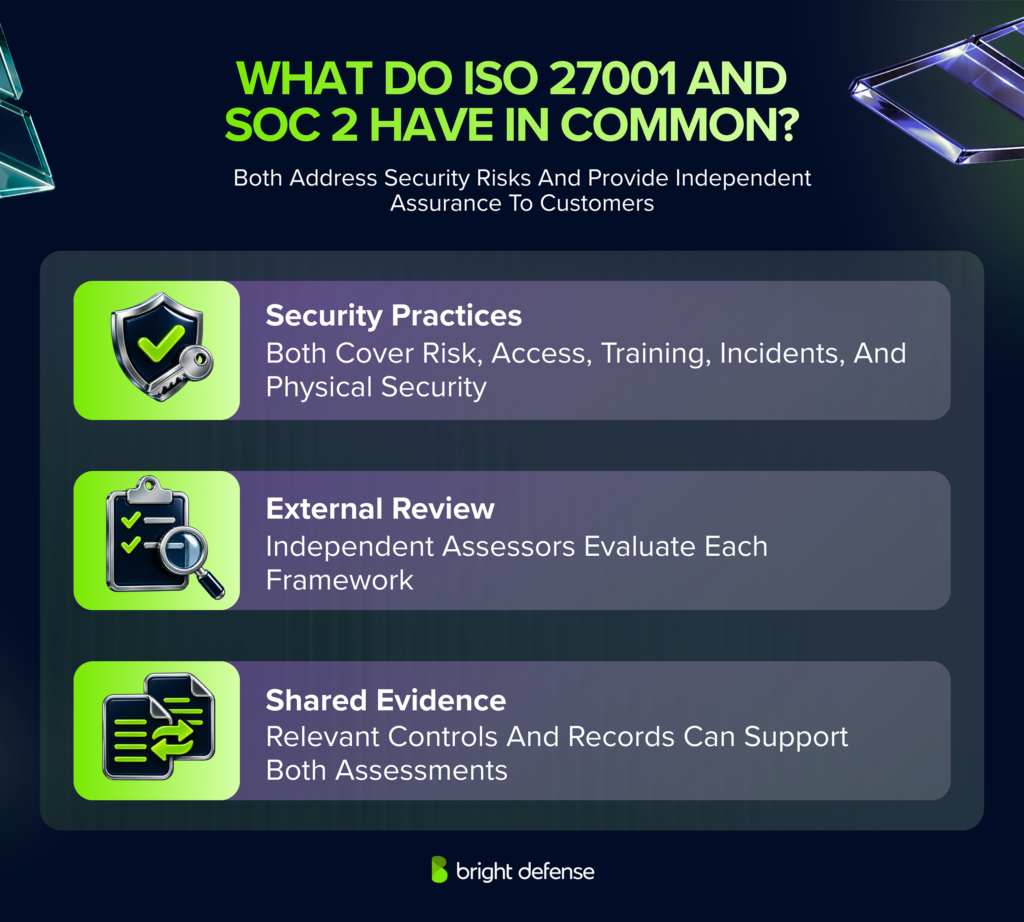
The following are their main similarities:
Shared Security Practices
Both address risk assessment, access control, employee security training, incident response, and physical security. The controls an organization implements depend on its risks, systems, and audit scope.
Independent External Assessment
Both involve an independent external assessment. A certification body audits the ISMS for ISO 27001, while a CPA firm examines controls for SOC 2. Customers use the resulting certificate or report during vendor reviews.
Reusable Controls And Evidence
Access reviews, training records, risk assessments, and incident response procedures can support both engagements when their scope and evidence requirements align. Compliance automation can help organize shared evidence and track control responsibilities.
Shared controls reduce duplicate work, but each engagement retains its own requirements. ISO 27001 certification and a SOC 2 report remain separate outcomes.
ISO 27001 Versus SOC 2: Which Is Right For Your Company?
The right choice depends on the assurance your customers require and the security program your organization needs to maintain. Review contract requirements, vendor questionnaires, and upcoming sales opportunities before selecting an audit.
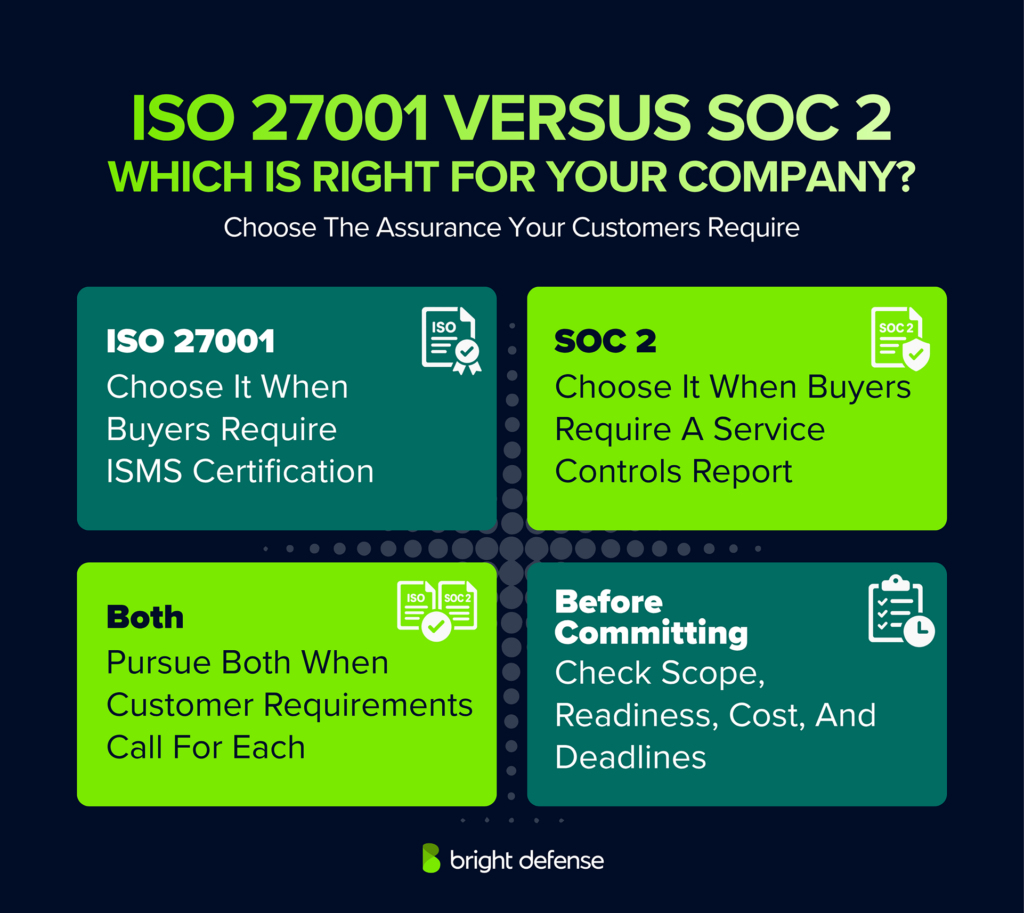
The following factors help determine which to pursue first:
Choose ISO 27001 When Customers Require ISMS Certification
Prioritize ISO 27001 when contracts or procurement requirements specify certification. It suits organizations seeking a formal management system for assigning security responsibilities, managing risks, and continually improving their security program.
Confirm that the proposed certification scope covers the services, locations, and operations customers expect.
Choose SOC 2 When Customers Require A Service Controls Report
Prioritize SOC 2 when buyers request detailed assurance about the controls supporting your services. Confirm the report type, Trust Services Criteria, and examination period they require.
A Type 1 report can satisfy a requirement for assurance at a specified date. Customers seeking evidence of operating effectiveness over time need Type 2.
Pursue Both When Business Requirements Support Both
Consider both when different customers require different forms of assurance or planned expansion creates a clear need. Shared controls and evidence can reduce duplicate preparation, while each engagement retains separate requirements.
Sequence the work around the earliest customer deadline and your team’s capacity.
Check Readiness Before Committing To A Deadline
Assess existing policies, control operation, evidence, staffing, and remediation needs. Include preparation and ongoing maintenance in the budget alongside audit fees.
Geography helps indicate buyer preferences, but written requirements determine acceptance. Confirm what customers will accept before paying for an engagement.
Bright Defense helps organizations assess gaps, define scope, and prepare for ISO 27001 certification and SOC 2 examinations through ongoing compliance support.
How Can Bright Defense Help With ISO 27001 And SOC 2?
Bright Defense provides readiness and ongoing compliance support for both ISO 27001 and SOC 2. We help organizations define scope, assess gaps, implement controls, and maintain evidence aligned with customer requirements.
For ISO 27001, our services include risk assessments, policy development, remediation guidance, and internal audits. Certified ISO 27001 Lead Auditors help evaluate your ISMS and identify issues to address before the certification audit.
For SOC 2, we help organizations establish relevant controls, organize evidence, and prepare for an independent CPA examination. Our team supports policy implementation, remediation tracking, and evidence management throughout preparation and the examination period.
Our continuous compliance services combine expert guidance, managed automation, and ongoing control monitoring. Organizations pursuing both can reuse relevant controls and evidence while addressing each engagement’s specific requirements.
FAQ
1. Can You Pursue ISO 27001 And SOC 2 At The Same Time?
Yes. Organizations can coordinate preparation, map shared controls, and reuse evidence where scope and audit requirements align. Each engagement produces a separate outcome, and completion dates can differ because SOC 2 Type 2 requires evidence over a specified period.
2. What Is The Overlap Between ISO 27001 And SOC 2?
Common areas include risk assessment, access control, incident response, employee training, and physical security. The amount of reusable work depends on scope, selected SOC 2 categories, and implemented controls. The AICPA provides a mapping, but its public resource does not establish a universal 80% overlap.
3. Is ISO 27001 Equivalent To SOC 2?
No. ISO 27001 certification evaluates an ISMS, while a SOC 2 report evaluates controls within a defined service system. A customer may accept either, but substitution requires their agreement when a contract specifies one.
4. Is SOC 2 Mandatory?
SOC 2 is generally voluntary. Customers can make a SOC 2 report a contractual or procurement requirement, including specifying Type 2 and the categories it must cover.
5. Is ISO 27001 A Legal Requirement?
ISO 27001 is generally a voluntary standard. Certification can become necessary through contracts, procurement rules, or applicable regulatory requirements. Organizations should check the requirements governing their industry and jurisdiction.
SOC 2 is an AICPA reporting framework used by organizations and customers internationally. ISO 27001 is an international standard jointly developed by ISO and IEC. Customer acceptance determines whether a SOC 2 report meets a particular requirement.
SOC 2 produces an attestation report issued by an independent CPA firm. ISO 27001 produces a certificate issued by an independent certification body.
No. You can proceed directly to Type 2 if your controls are operating and you can provide evidence for the examination period. Type 1 can be useful when a customer accepts a report covering a specified date while you prepare for Type 2.
An ISO 27001 certificate can generally be shared publicly. A SOC 2 report has restricted use and contains detailed system and control information, so distribution should follow the report’s restrictions. If you need a publicly shareable assurance report, ask your CPA firm about SOC 3.
No. Both provide assurance within a defined scope, but neither guarantees that a breach cannot occur. Your organization must continue managing risks, maintaining controls, and responding to new threats after the assessment.