What is Physical Penetration Testing?
Updated:
October 12, 2026
Physical penetration testing is an authorized attempt to access a facility, restricted area, or physical asset to find weaknesses in its security controls.
Trained testers examine measures such as doors, badge readers, visitor procedures, and staff responses. The test’s rules of engagement define where, when, and how they may act.
A test may simulate tailgating, impersonation, badge misuse, or bypassing a lock when the organization has explicitly authorized those methods.
The resulting report documents what happened, which controls failed, and what the organization should fix. This gives security teams a way to validate protections that a digital assessment alone cannot examine.
Physical testing can help organizations evaluate controls relevant to PCI DSS and ISO/IEC 27001. Neither standard creates a universal requirement to conduct physical penetration tests on a fixed schedule.
Organizations should set the scope and testing frequency based on facility risks, changes, and applicable obligations.
This guide explains what testers assess, when testing is useful, and how to act on the findings.
Key Takeaways
- Physical penetration testing checks whether facility access controls and staff procedures prevent or detect unauthorized entry.
- Testers may simulate tailgating, impersonation, or other entry methods within an agreed scope and rules of engagement.
- Findings should document the attempted entry, the control weakness, and a practical corrective action.
- Testing frequency should reflect facility risk and significant changes; there is no universal schedule for every organization.
- A physical test can support a broader security and compliance program, but it does not guarantee compliance or prevent every breach.
What is Physical Penetration Testing?
Physical penetration testing is an authorized attempt to enter a facility or restricted area to assess its security controls. It is one of several types of penetration testing.
Testers examine whether locks, badge systems, visitor procedures, surveillance, and staff responses prevent or detect unauthorized access. The agreed rules of engagement define the locations and methods they may test.
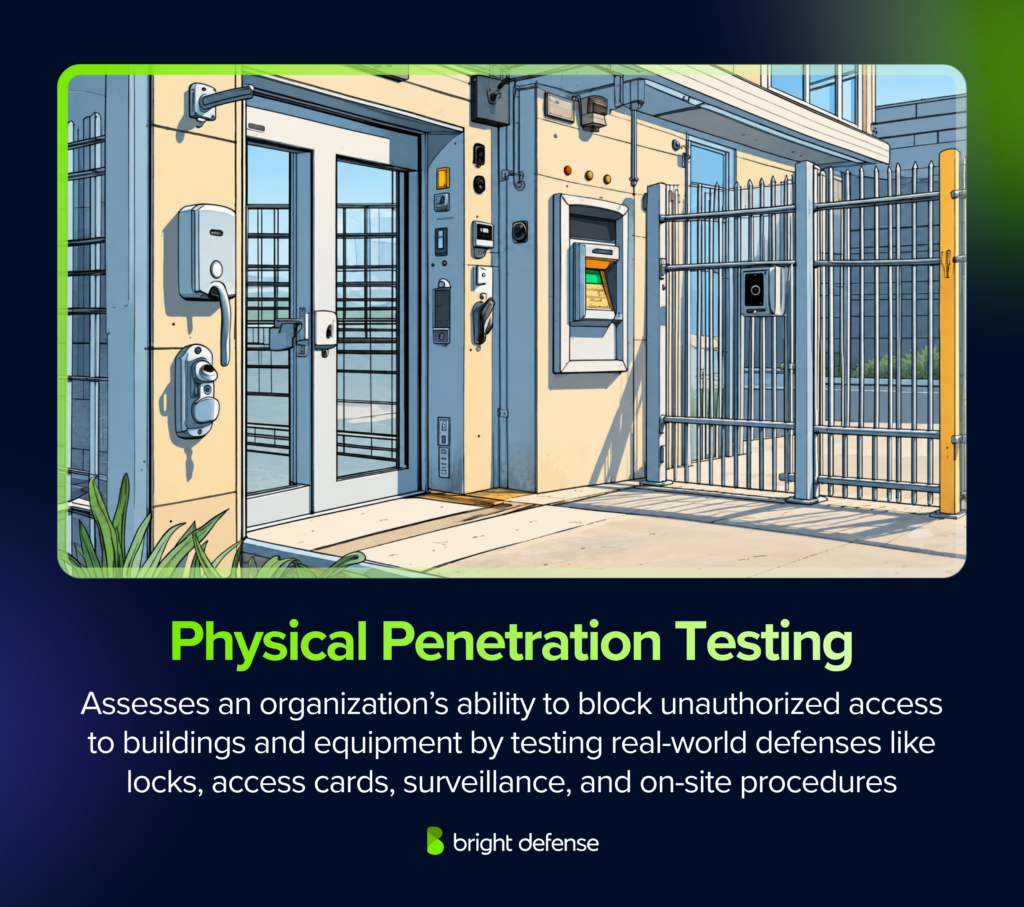
Testers may attempt to enter a restricted area through an approved scenario, such as following an employee through a door or posing as a visitor.
An assessment may include social engineering penetration testing to examine how staff verify identities and respond to access requests. The findings document successful and unsuccessful attempts, identify control weaknesses, and guide corrective action.
Why is Physical Penetration Testing Important?
Physical penetration testing identifies weaknesses that could allow unauthorized access to facilities, sensitive information, and equipment. It evaluates how entry controls, monitoring systems, and staff procedures perform during authorized intrusion attempts.
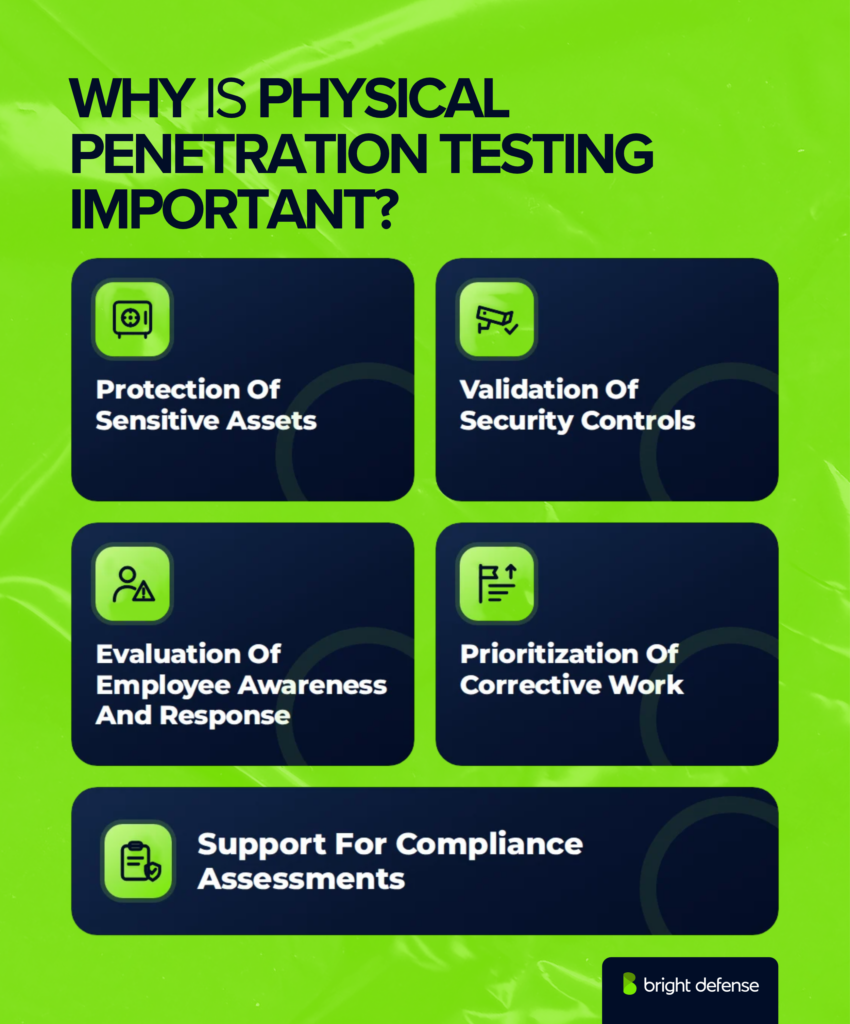
The following five benefits explain its role in a security program.
1. Protection of Sensitive Assets
Physical penetration testing examines whether an unauthorized person could reach assets such as servers, confidential documents, employee devices, or intellectual property.
Findings identify access paths that could enable theft, tampering, or operational disruption. Correcting these weaknesses helps organizations protect the assets within the tested environment.
2. Validation of Security Controls
Physical penetration testing checks whether locks, badge readers, alarms, surveillance, and guard procedures work together effectively. Across penetration testing programs, 28% of organizations test to validate security controls.
A test can reveal situations where a door restricts entry but another access route remains exposed, or where an intrusion generates an alert without an effective response.
NIST recognizes facility penetration testing as a method for evaluating controls at physical access points.
3. Evaluation of Employee Awareness and Response
Authorized social engineering scenarios assess how employees apply visitor and identity-verification procedures. Testers can evaluate whether staff verify access requests, follow escort requirements, and report suspicious activity through established channels.
Results help identify training needs and unclear responsibilities. A single exercise does not establish the overall likelihood of an insider threat.
4. Prioritization of Corrective Work
Physical penetration testing gives security teams evidence for prioritizing repairs, configuration changes, and procedural improvements. Findings should explain the access achieved, the assets exposed, and the potential business impact.
Across penetration testing programs, 32% of organizations use test results to prioritize security investments.
Assigning owners, setting completion dates, and retesting corrected weaknesses turns the assessment into measurable risk reduction.
5. Support for Compliance Assessments
Physical penetration testing can provide evidence relevant to physical-security obligations. PCI DSS Requirement 9 addresses physical access to cardholder data, while ISO/IEC 27001 supports risk-based selection of controls, including physical safeguards.
Test reports and remediation records can support audit preparation, but completing a physical penetration test does not independently establish compliance or certification.
Get Trusted Penetration Testing By Bright Defense Run a Pen TestHow Much Does Physical Penetration Testing Cost?
Published physical penetration testing prices start at US$6,800 for a single office, while broader assessments have published estimates of US$10,000 to US$50,000. These are provider examples, not an industry-wide average.
Penetration testing pricing depends on the locations, testing objectives, team size, and time required. Travel, reporting, and retesting arrangements vary by provider.
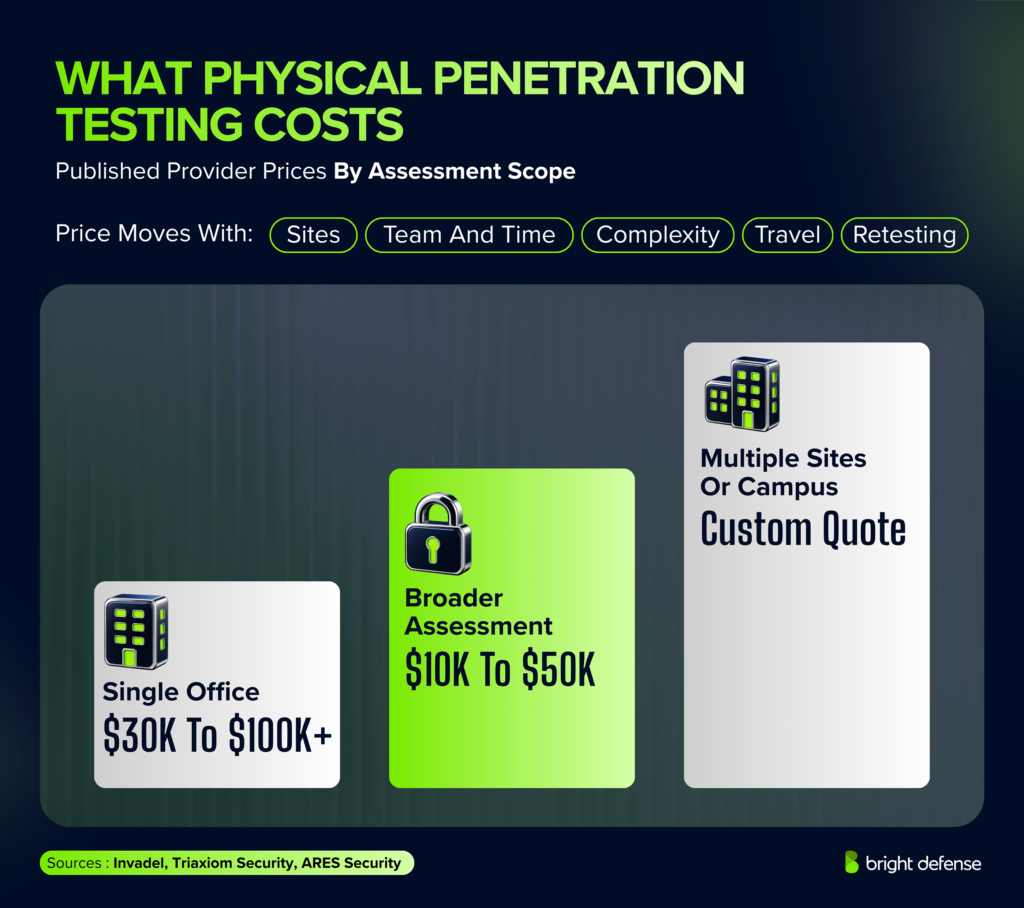
Published Physical Penetration Testing Prices
The following examples show how scope and included services affect the quoted price.
| Assessment Scope | Published Price | Scope and Inclusions |
|---|---|---|
| Single Office With Invadel | Starts at US$6,800. | The package covers one New York metropolitan office, two operators, and up to three days onsite. Reporting and a retest are included. |
| Single Office With Triaxiom Security | Typically US$10,800. | The assessment takes approximately three days. Travel is billed separately, except for the Charlotte, North Carolina area. |
| Broader Physical Assessment | ARES Security estimates US$10,000 to US$50,000. | Its November 2024 article provides a general estimate based on scope, complexity, and required services. |
| Multiple Sites or a Campus | A custom quote is required. | Providers price the engagement around locations, objectives, staffing, and scheduling. |
These published examples should be confirmed through a written proposal for the specific engagement.
Factors Influencing Cost
- Number of Sites: Additional locations require more reconnaissance, entry attempts, and evidence collection.
- Team Size and Duration: More testers, longer observation periods, and restricted testing windows increase the work involved.
- Security Complexity and Objectives: Guarded entrances, multiple restricted areas, and specialized access systems can require additional preparation and testing.
- Travel and Accommodation: Providers may include local travel or charge separately for transportation, lodging, and related expenses.
- Reporting and Retesting: Written findings are included in the providers reviewed here. Confirm whether the quote includes a debrief, remediation verification, and any return visit.
Request a proposal that specifies the authorized locations, testing hours, objectives, deliverables, travel charges, and retest terms. Comparing these details makes differences between quotes easier to assess.
How Criminals Can Cause Harm Inside a Building
Unauthorized physical access can expose an organization to information theft, system compromise, operational disruption, and threats to employee safety. The impact depends on the areas an intruder can reach and the safeguards protecting equipment and information.
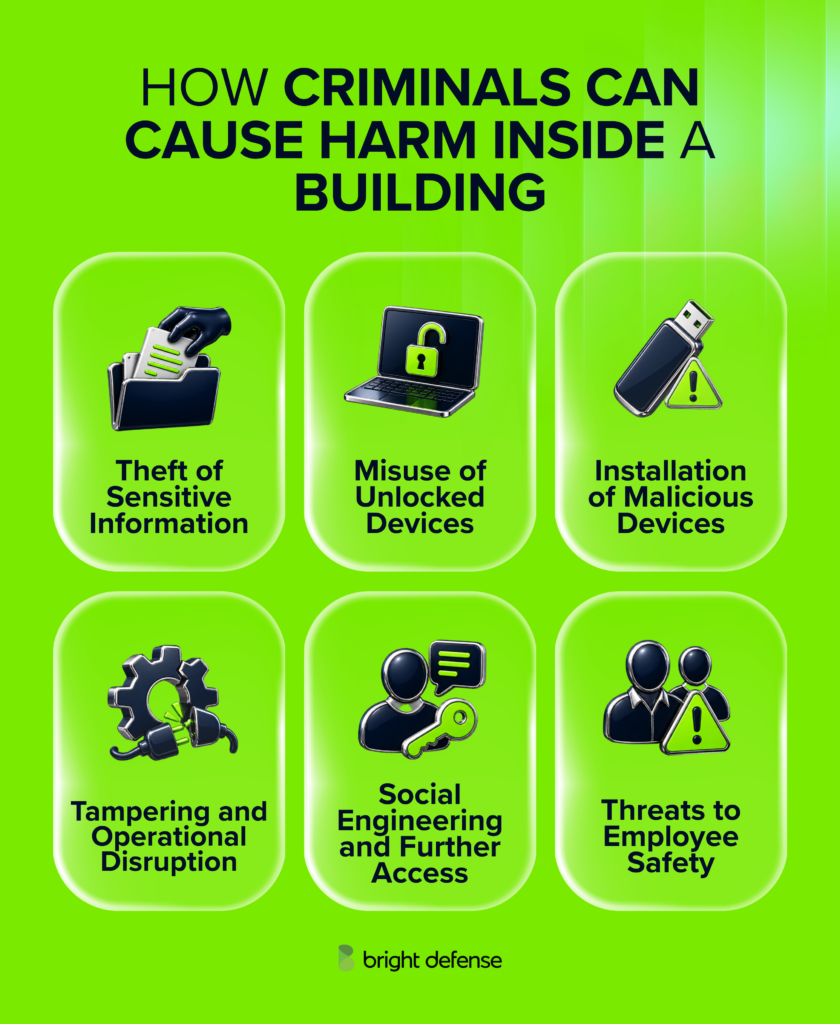
Potential harms include:
- Theft of Sensitive Information: Intruders can steal documents, laptops, or storage devices containing confidential information. Access to stolen digital data depends on protections such as encryption and device authentication.
- Misuse of Unlocked Devices: An unattended, unlocked device can expose active sessions, business applications, and sensitive files. An intruder could use that access to collect information or make unauthorized changes.
- Installation of Malicious Devices: Unauthorized hardware or removable media can introduce malware, capture information, or provide an unapproved connection to systems. Physical access creates opportunities for these attacks where device and network controls are insufficient.
- Tampering and Operational Disruption: Interference with servers, network cabling, power supplies, or operational equipment can interrupt services and damage systems. The consequences depend on the equipment affected and available recovery measures.
- Social Engineering and Further Access: An intruder posing as an employee, contractor, or service technician can deceive staff into sharing sensitive information or granting access to additional restricted areas.
- Threats to Employee Safety: Unauthorized individuals can intimidate, threaten, or assault employees and visitors. Physical security planning must account for workplace violence alongside risks to information and equipment.
How to Perform a Physical Penetration Test
A physical penetration test follows an agreed process covering authorization, reconnaissance, controlled testing, evidence collection, cleanup, reporting, and remediation.
The following seven steps provide a practical sequence for assessing facility security and verifying corrective work.
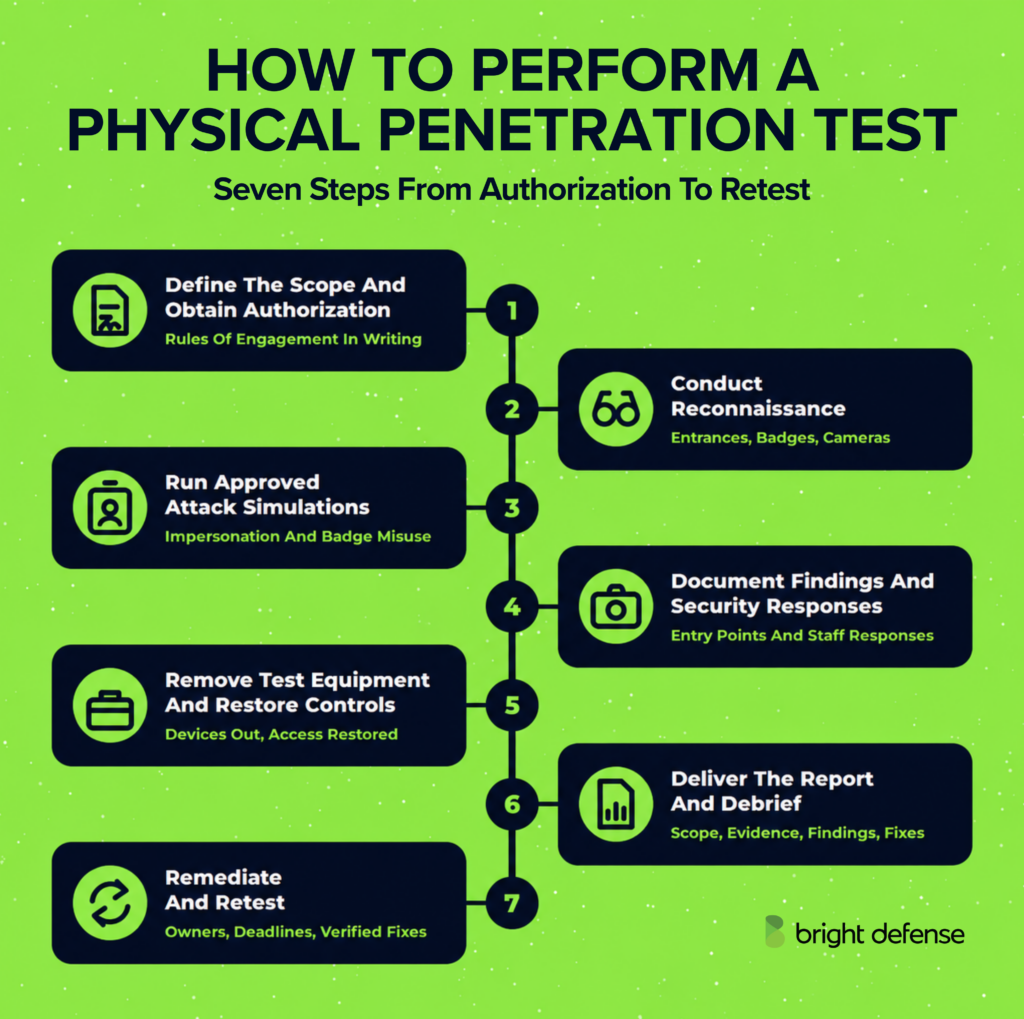
Step 1: Define the Scope and Obtain Authorization
Obtain written authorization before testing begins. Define the facilities, restricted areas, objectives, permitted techniques, testing hours, and exclusions.
Establish emergency contacts, stop conditions, and evidence-handling requirements. Confirm any permissions needed from building owners or third parties. Record these arrangements in the rules of engagement.
Step 2: Conduct Reconnaissance
Review available facility information and observe security controls within the authorized scope. Examine entrances, visitor procedures, access systems, surveillance coverage, and protections around sensitive areas such as server rooms.
Use these observations to identify scenarios that test the agreed objectives.
Step 3: Run Approved Attack Simulations
Conduct authorized scenarios involving visitor verification, employee impersonation, badge misuse, or attempts to enter restricted areas. Select credential tests according to the badge technology and authentication method.
Lock manipulation and placement of test equipment should follow the specific permissions and limits established before the engagement.
Step 4: Document Findings and Security Responses
Record evidence throughout the assessment, including timestamps, attempted entry points, successful access, blocked attempts, and relevant staff responses.
Use approved photographs or recordings and protect sensitive information collected during testing. Where included in scope, document whether alarms triggered and security personnel responded.
Step 5: Remove Test Equipment and Restore Affected Controls
Account for and remove all test devices, temporary credentials, and other materials introduced during the engagement.
Confirm that affected doors, access permissions, and security systems are in their agreed operational state. Record cleanup actions and notify the designated contact of any unresolved issues.
Step 6: Deliver the Report and Debrief
Provide a structured penetration testing report covering the scope, methods, limitations, evidence, findings, and business impact. Recommend corrective actions based on the weaknesses observed.
Review the results with leadership, facilities, IT, and security personnel responsible for implementing changes.
Step 7: Remediate and Retest
Assign each finding an owner, priority, and completion date. Correct weaknesses through appropriate repairs, access changes, procedural updates, or training.
Retest significant findings to verify that the corrective actions work, and document any remaining exposure.
Common Physical Penetration Testing Techniques
Physical penetration testing uses authorized entry attempts, credential tests, and social engineering scenarios to evaluate facility security. Testers select methods according to the site’s controls, assessment objectives, and agreed rules of engagement.
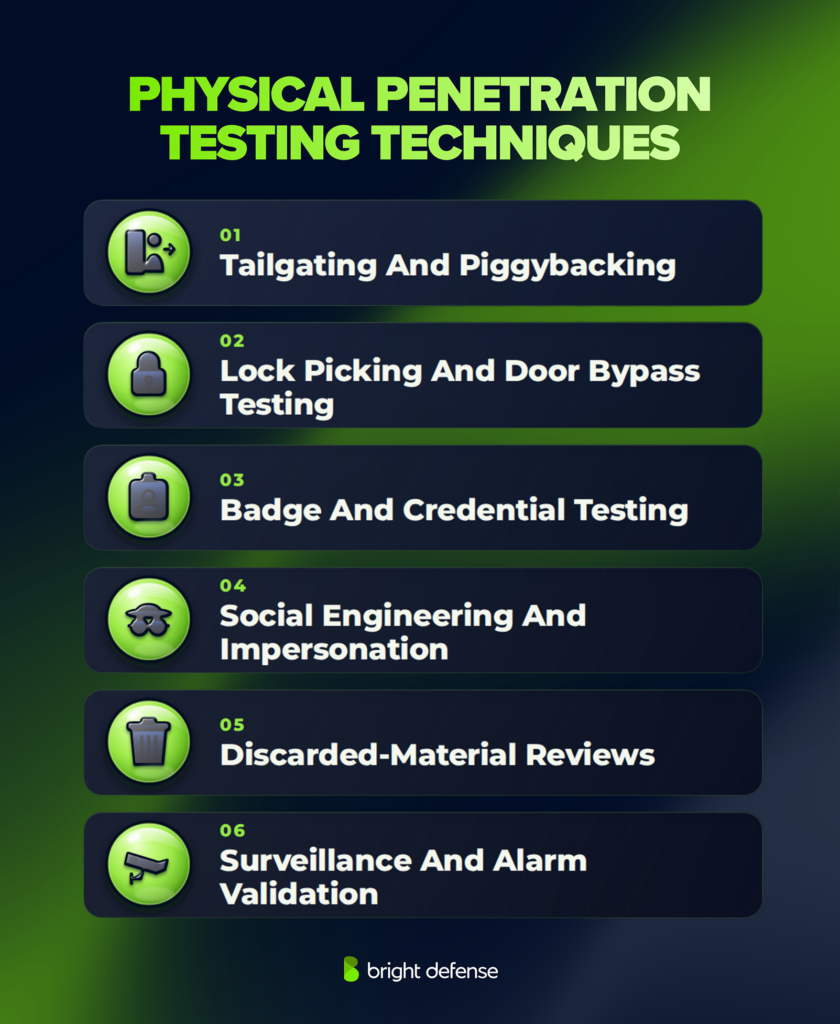
Common techniques include the following:
- Tailgating and Piggybacking: Testers assess whether someone can pass through a controlled entrance without individual authorization, including situations where an employee holds a door open. Carrying equipment can form part of this scenario.
- Lock Picking and Door Bypass Testing: Testers evaluate weaknesses in locks, latches, doors, and related hardware. The permitted approach depends on the installation and agreed limits. These techniques do not guarantee damage-free entry.
- Badge and Credential Testing: Testers assess whether susceptible access credentials can be copied or misused. Cloning feasibility depends on the credential technology and authentication method; contactless operation alone does not make every badge clonable.
- Social Engineering and Impersonation: Approved scenarios involve posing as employees, delivery personnel, or contractors to evaluate identity checks, visitor procedures, and staff responses to access requests.
- Discarded-Material Reviews: Commonly called dumpster diving, this technique examines authorized waste-disposal areas for exposed documents, badges, or other sensitive materials. Findings identify weaknesses in disposal procedures and information handling.
- Surveillance and Alarm Validation: Testers assess whether approved intrusion attempts are visible to cameras, trigger relevant alerts, and receive an appropriate response. This evaluates detection alongside the ability to prevent entry.
Destructive forced-entry testing requires explicit authorization and separate arrangements for safety, damage, and restoration. It should not be assumed to form part of a standard engagement; some providers expressly exclude forced entry and damage.
Physical Penetration Testing Tools
Physical penetration testing tools help assess facility access controls, credential security, employee procedures, and exposure after entry.
Testers select equipment according to the assessment objectives, installed technology, and approved rules of engagement.
| Tool Category | Purpose During Testing | Limitations and Scope |
|---|---|---|
| Lock Picks and Door Bypass Tools | Testers evaluate weaknesses in locks, latches, doors, and cabinets. | Suitability depends on the hardware, and damage-free operation is not guaranteed. |
| RFID and NFC Assessment Tools | Readers and analyzers examine radio-frequency identification (RFID) and near-field communication (NFC) credentials, including supported reading and emulation functions. | Capabilities depend on the credential protocol, encryption, and authentication method. These tools cannot universally clone access badges. |
| Wireless Survey Tools | Testers identify wireless networks, signal coverage, and potential exposure around the facility. | Wireless assessment requires suitable equipment and an agreed scope. A general wireless scanner does not replace a badge reader. |
| Cameras and Evidence-Recording Equipment | Testers document access attempts, control weaknesses, and relevant conditions. | Recording permissions and evidence-handling rules should define what can be captured and retained. |
| Network Test Appliances | Authorized hardware tests whether physical access permits an unapproved network connection or remote access. Internal network testing can then evaluate which systems that connection exposes, within the approved scope. | Connecting a device does not automatically provide access to protected systems. Capabilities depend on network and endpoint controls. |
| Controlled USB Test Devices | Test media and keyboard-emulating devices assess employee behavior and USB security controls. | These are distinct test scenarios. Benign demonstrations can validate exposure without deploying destructive malware. |
| Role-Play Materials | Approved props support employee, visitor, or contractor impersonation scenarios. | Props help test identity verification and staff responses; they do not guarantee successful entry. |
| Drones for Specialized Assessments | Aerial imagery can support reviews of perimeter layout and difficult-to-observe areas. | Drone use is optional and depends on site permissions and applicable aviation restrictions. |
The final report should connect each tool-assisted finding to a control weakness, supporting evidence, business impact, and corrective action.
How Can Bright Defense Help You With Physical Penetration Tests?
Bright Defense helps organizations assess facility access controls, identify physical security weaknesses, and prioritize corrective actions.
Testing covers agreed scenarios involving entrances, badge systems, visitor procedures, staff responses, and access to sensitive areas. Authorized techniques can include tailgating, door bypass testing, and impersonation.
Physical Testing Scope and Deliverables
Bright Defense’s approach focuses on four areas:
- Controlled Intrusion Testing: Approved scenarios evaluate whether physical controls and employee procedures prevent or detect unauthorized access.
- Clear Reporting: Findings document the methods used, access achieved, supporting evidence, and recommended fixes. Reports help facilities, IT, and security teams assign corrective work.
- Adaptable Scope: Engagements can address office workspaces, restricted data center areas, or multiple locations. Testing at a third-party facility requires agreement on permissions and responsibilities with the operator.
- Policy and Compliance Alignment: Testing follows agreed safety, personnel, and operational restrictions. Findings can support reviews of relevant physical-security controls associated with SOC 2, ISO/IEC 27001, and HIPAA. The assessment contributes evidence to the broader compliance program.
FAQs
1. What Is a Physical Penetration Test?
A physical penetration test is an authorized assessment that attempts to bypass facility security controls. It evaluates whether someone could reach restricted areas, equipment, or sensitive information through weaknesses in physical barriers and staff procedures.
2. What Is the Main Goal of Physical Penetration Testing?
The goal is to identify exploitable weaknesses and determine their potential impact. Testing examines how doors, locks, badges, reception procedures, guards, and surveillance work together to prevent, detect, and respond to unauthorized access.
3. Which Areas Are Commonly Tested?
Common targets include perimeter entrances, reception areas, restricted offices, server rooms, workstations, and document storage or disposal areas. The agreed scope determines which locations, controls, and access attempts testers may assess.
4. What Assessment Approaches Are Available?
Tests may be announced to participating staff or conducted with awareness limited to designated contacts. Both require authorization. A collaborative walkthrough can identify weaknesses through observation and discussion, but it does not necessarily demonstrate whether an attacker could exploit them.
5. Is Written Authorization Required Before Testing?
Yes. Obtain written authorization from parties with authority over the locations and activities involved. The rules of engagement should define approved targets, testing windows, permitted methods, exclusions, emergency contacts, evidence handling, and conditions for stopping the test.
It can, when explicitly included in the scope. Approved scenarios may test whether staff verify visitor identities, follow escort procedures, or respond appropriately to impersonation attempts. The objective is to identify weaknesses in procedures and training.
Testers agree on restrictions, escalation procedures, and emergency stop conditions before work begins. Planning should address employee safety, sensitive operations, property damage, and unexpected encounters. Activities must remain within the authorized scope throughout the engagement.
The report should explain objectives, scope, methods, limitations, findings, and supporting evidence. It should also describe potential business impact and prioritize corrective actions. Documenting successful defenses alongside identified weaknesses helps teams understand which controls worked.
Consider testing after an office move, significant renovation, access-control replacement, or major change to guard and visitor procedures.
Set recurring assessments according to facility risk, previous findings, and applicable obligations. Retesting can verify that important weaknesses have been corrected.
A useful four-part model is deter, detect, delay, and respond. Controls discourage intrusion, identify suspicious activity, slow unauthorized access, and support an appropriate response. This is a planning model; other guidance also includes functions such as mitigating an attack’s consequences.
No. Internal and external testing describe two common network-testing perspectives. External testing evaluates exposure from outside the security perimeter; internal testing evaluates risks from an established foothold. Other assessment categories include applications, APIs, wireless networks, cloud environments, and physical security.