CMMC Scoping Guide – A Strategic Approach to Certification
Updated:
October 7, 2026
CMMC scoping identifies the systems and assets that must be included in an assessment. Contractors need to trace where Federal Contract Information (FCI) or Controlled Unclassified Information (CUI) is processed, stored, or transmitted, then apply the scoping rules for the level required by their contract. Section 170.19 of the CMMC program rule defines those rules for Levels 1, 2, and 3.
The CMMC program rule is final, and contractual implementation began on November 10, 2025. The current rollout needs a qualification: Phase 2 requirements were suspended on July 13, 2026, while Phase 1 self-assessment requirements remain in effect. Contractors should check the level and assessment type stated in each applicable solicitation or contract.
This guide explains the three CMMC levels, the asset categories and boundaries in § 170.19, and the steps for documenting an assessment scope using the DoD’s scoping guidance.
What is CMMC?
The Cybersecurity Maturity Model Certification (CMMC) is a Department of Defense program for assessing how contractors protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI).
It has three levels. The level and assessment type required for a contractor depend on the applicable contract. A CMMC assessment does not always involve an outside assessor.
The levels use the following security requirements and assessment routes:
| Level | Security Requirements | Assessment Route Under the Program Rule |
|---|---|---|
| Level 1: Foundational | 15 basic safeguards from FAR 52.204-21 to protect FCI | Annual self-assessment |
| Level 2: Advanced | 110 requirements from NIST SP 800-171 Revision 2 to protect CUI | Self-assessment or assessment by a Certified Third-Party Assessment Organization (C3PAO), as specified by the contract |
| Level 3: Expert | The Level 2 foundation plus 24 selected requirements from NIST SP 800-172 | Government-led assessment by the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC) |
These are the routes established by the CMMC model. Current implementation remains in Phase 1: Phase 2 requirements are suspended, while applicable Level 1 and Level 2 self-assessment requirements remain in effect.
The DoD provides scoping guidance for each level to help organizations identify the assets included in their assessment.
Why You Need CMMC
A contractor needs a current CMMC status when an applicable DoD solicitation or contract requires it. The required level depends on the information handled and the contract terms.
During the current Phase 1 suspension, requiring activities may designate Level 1 or Level 2 self-assessments.
- Maintain contract eligibility: DFARS 252.204-7021 connects the required CMMC level to contract award and continuing performance. Contracting officers check the contractor’s current status in the Supplier Performance Risk System (SPRS). A self-assessment can establish the applicable status; an outside certificate is not required for every level.
- Demonstrate required safeguards: Level 1 assesses the basic FCI safeguards in FAR 52.204-21. Level 2 assesses the CUI security requirements in NIST SP 800-171 Revision 2. Applicable DFARS 252.204-7012 safeguarding and incident-reporting obligations remain in effect.
- Protect information across the supply chain: CMMC assessments give contractors and the DoD a defined way to evaluate safeguards for FCI and CUI, including information handled during subcontracted work.
- Prepare for the current rollout: CMMC contractual implementation began on November 10, 2025. The planned Phase 2 transition was suspended on July 13, 2026. Level 1 and Level 2 self-assessment requirements remain in effect, while requiring activities cannot designate Level 2 C3PAO or Level 3 DIBCAC assessments during the suspension.
- Give customers verifiable assessment information: A current CMMC status records the result for the applicable assessment scope. Prime contractors and customers can use that status when checking requirements for work involving FCI or CUI.
Key Components of the CMMC Scoping Guide
CMMC scoping identifies the assets that belong in an assessment and how each asset will be reviewed. Section 170.19 of the program rule sets the requirements for Levels 1, 2, and 3. The DoD scoping guides provide instructions for applying them.
Current contractual implementation remains in Phase 1, which permits Level 1 and Level 2 self-assessment requirements while Phase 2 is suspended.
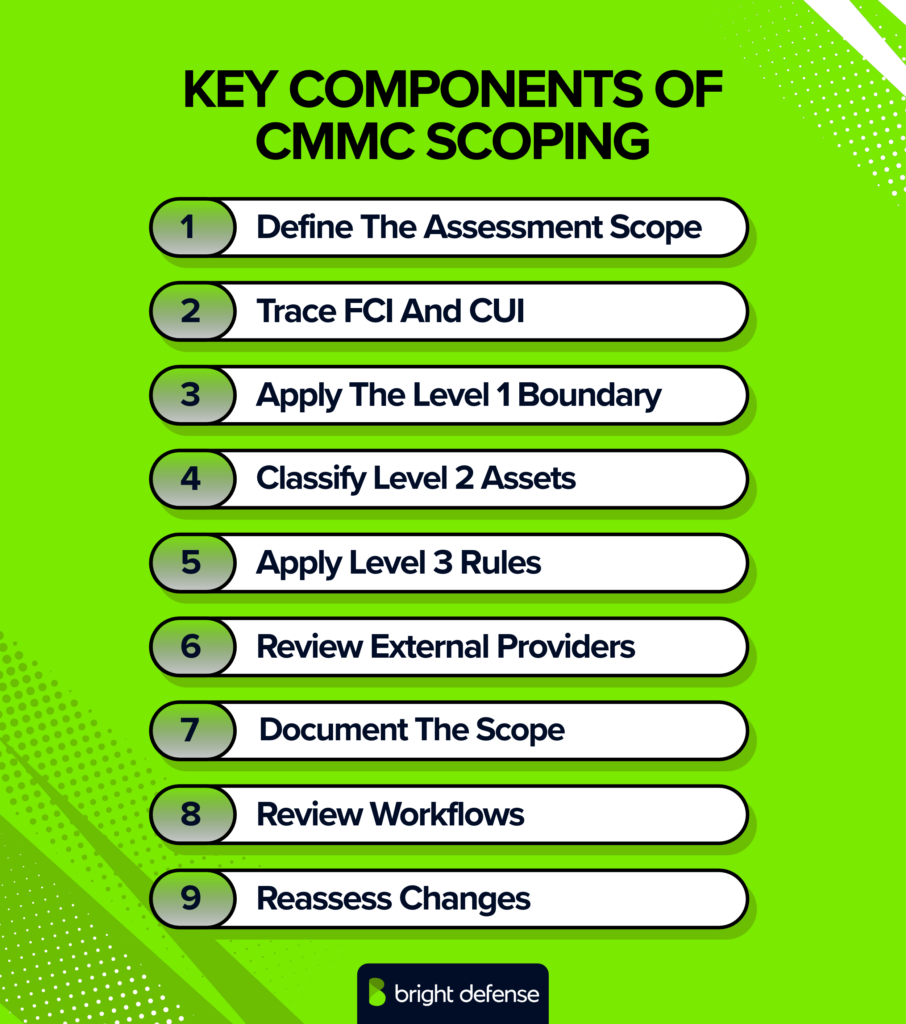
The nine components below cover the assessment boundary, asset treatment, providers, documentation, and changes to scope:
1. Define the Assessment Scope Before Testing
An Organization Seeking Assessment (OSA) must specify its CMMC Assessment Scope before the assessment begins. Start with the contract’s required level, then identify the systems involved in processing, storing, or transmitting the relevant information.
The scope is defined by those activities and the applicable asset rules, rather than by an organization chart or a preferred network boundary.
Scoping remains a common preparation gap. Our CMMC readiness statistics show that only 27% of surveyed organizations preparing internally had a well-documented assessment scope, compared with 63% working with experienced partners.
2. Trace FCI and CUI
Federal Contract Information (FCI) determines which information systems enter a Level 1 assessment. Controlled Unclassified Information (CUI) drives Level 2 and Level 3 scoping.
Trace where the information enters, moves through, and leaves the environment, including endpoints, applications, storage, and provider services. This makes asset categorization more accurate.
3. Apply the Level 1 Boundary
Level 1 includes OSA information systems that process, store, or transmit FCI. Systems that do none of these are out of scope. Under § 170.19, specialized assets that can handle FCI but cannot be fully secured are outside the Level 1 assessment scope and are not assessed against Level 1 requirements.
The rule does not require documentation for out-of-scope Level 1 assets or a Level 1 System Security Plan (SSP). Organizations should still consider the people, technology, facilities, and external providers involved in FCI workflows when defining the boundary.
4. Classify Level 2 Assets
Level 2 uses five asset categories. Four are within the assessment scope; the fifth is outside it.
| Asset Category | Treatment at Level 2 |
|---|---|
| CUI Assets | Process, store, or transmit CUI and are assessed against applicable Level 2 requirements. |
| Security Protection Assets | Provide security functions to the assessment scope and are assessed against requirements relevant to those functions. |
| Contractor Risk Managed Assets (CRMAs) | Could handle CUI but are not intended to under documented policies and practices. Assessors review their SSP treatment and may perform limited checks when warranted. Physical or logical separation from CUI assets is not required for this category. |
| Specialized Assets | Can handle CUI but cannot be fully secured. They remain in scope; assessors review their SSP treatment without assessing them against the other Level 2 requirements. |
| Out-of-Scope Assets | Cannot handle CUI, do not protect CUI assets, and are physically or logically separated from CUI assets. They are not assessed. |
5. Apply the Different Level 3 Rules
A Level 3 assessment scope must equal or be a subset of the organization’s Level 2 scope. Asset treatment changes at Level 3: a CRMA included in the Level 3 boundary is treated as a CUI Asset, and specialized assets in that boundary are assessed against applicable Level 3 requirements.
The Level 3 assessment can include limited checks of Level 2 requirements. These rules should not be described as the same five-category review used at Level 2.
6. Account for External Service Providers and Cloud Services
For Levels 2 and 3, determine whether an external service provider (ESP) processes, stores, or transmits CUI or Security Protection Data (SPD), and whether it is a cloud service provider (CSP).
A CSP handling CUI must meet the FedRAMP requirements referenced by DFARS 252.204-7012, through authorization or an accepted equivalent under DoD policy. A non-cloud ESP handling CUI has its relevant services assessed within the OSA’s scope.
Services handling SPD without CUI are assessed as Security Protection Assets. Document the provider relationship, services, and shared responsibilities in the SSP, service description, and customer responsibility matrix.
7. Document Assets, Connections, and Separation
For Levels 2 and 3, maintain an asset inventory, an SSP describing how each in-scope category is treated, and a network diagram showing the assessment scope. The SSP does not need an individual entry for every asset when the inventory provides that detail.
Show CUI pathways, provider connections, and any enclave boundaries clearly enough to support scoping decisions. An asset claimed to be out of scope must meet the rule’s separation and data-handling conditions; a CRMA has different treatment and does not require that separation.
8. Review People, Facilities, and Workflows
A device inventory alone may miss how FCI or CUI is handled. Review the work performed by employees, contractors, and provider staff, along with the offices, production areas, remote access methods, and systems they use.
Record the assets and services brought into scope by those workflows under the applicable level’s rules.
9. Reassess Significant Scope Changes
Review the assessment boundary when architecture, information flows, providers, or covered systems change. DoD rulemaking states that significant changes within the CMMC Assessment Scope require a new assessment and affirmation.
The affirming official is responsible for judging whether a change is significant enough to require reassessment; routine changes do not automatically trigger one.
Steps to Scope Your Organization for CMMC
CMMC scoping begins with the contract requirement and a trace of where Federal Contract Information (FCI) or Controlled Unclassified Information (CUI) is handled.
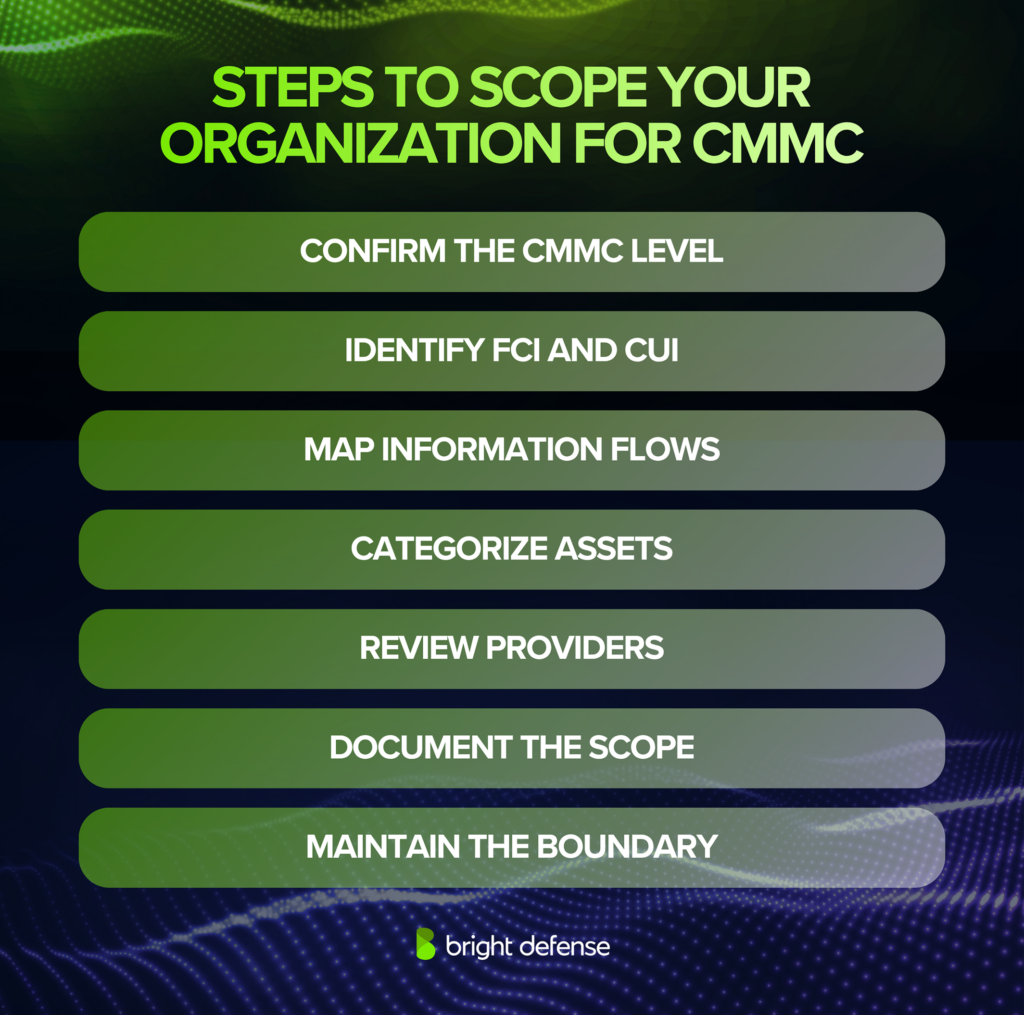
The assessment boundary must be specified before testing begins. The seven steps below provide a practical sequence for preparing for a CMMC assessment.
1. Confirm the Required CMMC Level
Review the solicitation or contract with the contracts team. Record the required level, assessment type, and systems used for the work.
During the current Phase 1 suspension, requiring activities may designate Level 1 or Level 2 self-assessments, but cannot designate Level 2 C3PAO or Level 3 DIBCAC assessments.
2. Identify FCI and CUI
Work with contract owners, data owners, and IT staff to identify relevant information received or created during contract performance.
Use contract instructions, markings, and the CUI Registry to resolve how the information should be handled. FCI determines Level 1 scoping; CUI drives Level 2 and Level 3 scoping.
3. Map the Information Flow
Trace where FCI or CUI enters, is processed, is stored, and leaves the environment. Include email, endpoints, applications, backups, remote access, and cloud services where they handle the information. Record the systems and connections involved so the boundary reflects actual workflows.
4. Categorize Assets and Set the Boundary
At Level 1, include information systems that process, store, or transmit FCI, subject to the rule’s treatment of specialized assets. At Level 2, classify assets as CUI Assets, Security Protection Assets, Contractor Risk Managed Assets, Specialized Assets, or Out-of-Scope Assets.
Apply the distinct Level 3 rules when that level is relevant. An enclave can help limit a boundary, but CMMC does not require every organization to create one. Assets claimed to be out of scope at Level 2 must meet the rule’s data-handling and separation conditions.
5. Review Providers and Subcontractors
Identify cloud providers, managed services, security services, and subcontractors involved in the information flow. For Level 2, determine whether an external service provider handles CUI or Security Protection Data and whether it is a cloud service provider; those distinctions control how its services are assessed.
A cloud service handling CUI must meet the applicable FedRAMP requirements in DFARS 252.204-7012. Do not assume every provider needs a separate CMMC certification. Review CMMC flow-down requirements separately for subcontracts that involve FCI or CUI.
6. Document and Check the Scope
For Levels 2 and 3, prepare an asset inventory, a System Security Plan (SSP) describing asset treatment, and a network diagram of the assessment scope. Document provider services and shared responsibilities in the SSP and customer responsibility matrix.
Walk through the boundary with system owners to check that the inventory, diagrams, and actual information flows agree. Level 1 does not require an SSP under its scoping rule.
7. Keep the Boundary Current
Review the scope when systems, information flows, architecture, or providers change. A significant change within the assessed scope can require a new assessment and affirmation; routine changes do not automatically require reassessment. Record the change and the reason for the decision.
Practical Tips for Effective Scoping
Effective CMMC scoping starts with actual FCI and CUI workflows and applies the asset rules for the required level. The DoD scoping guides help organizations define an assessment boundary they can explain and support with evidence.
The following practices address scope management, common mistakes, and use of the guides.
Best Practices for Identifying and Managing the Scope
- Inventory information and assets. Trace where Federal Contract Information (FCI) and Controlled Unclassified Information (CUI) enter, move through, and leave the environment. Record the systems, applications, storage, and services involved.
- Involve the people who manage the work. Ask contracts, IT, security, operations, and data owners to verify information flows and asset use. A system owner may identify a connection or workflow that is absent from a network diagram.
- Apply the correct asset category. At Level 2, distinguish CUI Assets, Security Protection Assets, Contractor Risk Managed Assets, Specialized Assets, and Out-of-Scope Assets. Segmentation can support an out-of-scope designation, but Level 2 Contractor Risk Managed Assets do not have to be physically or logically separated from CUI assets.
- Review the scope after changes. Update the inventory, System Security Plan (SSP), and network diagram when systems, providers, or information flows change. Evaluate significant changes for possible reassessment.
Common Scoping Pitfalls to Avoid
- Missing systems that provide security protection. Identity services, logging platforms, and firewalls may be in scope because of the security functions they provide, even when they do not store CUI.
- Treating every system without CUI as out of scope. Level 2 out-of-scope assets must meet the rule’s separation and data-handling conditions. An asset that could handle CUI may instead be a Contractor Risk Managed Asset.
- Overlooking providers and subcontractors. Review whether provider services handle CUI or Security Protection Data, then document the relevant services and shared responsibilities. Check subcontract flow-down obligations separately; a provider does not automatically need its own CMMC certification.
Using the CMMC Scoping Guides
- Use the guide for the required level alongside 32 CFR 170.19. Apply its asset definitions to real systems, record the reason for each classification, and direct assessment work toward assets that fall within the boundary.
- Get specialist help where classifications remain unclear. A consultant with relevant CMMC scoping experience can review data flows, provider duties, and documentation. Cyber AB Registered Practitioners and Registered Practitioner Organizations provide advisory services; that designation does not make them certification assessors.
Final Thoughts
Accurate CMMC scoping defines which assets belong in the assessment and how they must be reviewed. Use the DoD guide for the required level to trace Federal Contract Information or Controlled Unclassified Information, classify assets, and document the resulting boundary. Involve contracts, IT, security, and operations staff so the scope reflects how information is handled in practice.
Review that boundary when systems, providers, or information flows change. A current scope supports the assessment required by the contract and helps direct security work toward the assets that protect federal information.
About Bright Defense
Bright Defense helps defense contractors prepare for CMMC Level 1 and Level 2 requirements. Its services include assessment scoping, gap analysis, control implementation, remediation support, and evidence preparation.
The team can support current self-assessment requirements and preparation for a third-party assessment when one is required. Contact Bright Defense about CMMC consulting to review your required level, assessment scope, and remaining security gaps.
Faq
1. What is CMMC scoping?
CMMC scoping is the process of defining the assessment boundary before an assessment begins. The scope determines which organizational assets must be evaluated against the applicable CMMC security requirements.
2. Which assets are included in a CMMC Level 1 scope?
Level 1 includes assets that process, store, or transmit FCI. Those in-scope assets are assessed against the applicable 15 Level 1 security requirements from FAR 52.204-21.
3. Which asset categories are included in a CMMC Level 2 scope?
Level 2 includes CUI Assets, Security Protection Assets, Contractor Risk Managed Assets, and Specialized Assets. Out-of-Scope Assets are excluded when they cannot process, store, or transmit CUI and do not provide security protections for CUI assets.
4. How does CUI affect the CMMC assessment boundary?
CUI is central to Level 2 scoping because systems that process, store, or transmit CUI generally fall within the assessment boundary. Level 2 currently maps to 110 NIST SP 800-171 Rev. 2 security requirements.
5. Why should CMMC scoping happen before assessment preparation?
Accurate scoping prevents teams from testing the wrong environment or overlooking systems that handle protected information. It also determines the assets, evidence, security controls, and documentation that must be prepared for the assessment.
6. Does my employee laptop need to be in scope if it accesses CUI?
Yes. An asset that processes, stores, or transmits CUI is generally a CUI Asset and belongs within the Level 2 assessment scope, even when it is an ordinary workstation or laptop.
7. Can I create a separate CUI enclave to reduce my CMMC scope?
Yes. Logical or physical separation can limit the assessment boundary when systems outside the enclave cannot process, store, or transmit CUI and do not provide security protections for CUI assets.
8. Do cloud providers and subcontractors affect my CMMC scope?
Yes. Third-party systems can affect scope when they process, store, transmit, or protect FCI or CUI, and current DFARS requirements require contractors to flow the appropriate CMMC requirements down to applicable subcontracts and other contractual instruments.
9. What documents should I prepare for a Level 2 CMMC scope?
Prepare an asset inventory, System Security Plan (SSP), and network diagram that accurately represent the assessment boundary. Specialized Assets must be documented in the SSP and managed through the organization’s risk-based security policies and practices.
10. Has the 2026 CMMC Phase II suspension changed the need to define scope?
No. The Department suspended Phase II on July 13, 2026, but Phase I requirements remain in effect, and organizations still need to identify the systems handling FCI or CUI for applicable self-assessments. The program is currently paused in Phase I, where Level 1 self-assessments are annual and Level 2 self-assessments occur every 3 years with annual affirmations.
11. What are CMMC guidelines?
CMMC guidelines require defense contractors to protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). The framework has 3 levels: Level 1 uses 15 FAR 52.204-21 requirements, Level 2 uses 110 NIST SP 800-171 Rev. 2 requirements, and Level 3 adds 24 NIST SP 800-172 requirements.
12. Is there free CMMC training available?
Yes. Defense Acquisition University provides free online CMMC training, while Project Spectrum offers free CMMC courses, readiness assessments, training videos, and cybersecurity support for defense contractors.
13. What is a good CMMC score?
For Level 1, there is no numerical score; all 15 requirements must be marked MET. For Level 2, 110 is the maximum score, while 88 is the minimum score that can qualify for Conditional Level 2 status when applicable POA&M requirements are met.
14. What are the 17 controls for CMMC Level 1?
Current CMMC Level 1 has 15 security requirements, not 17. Older CMMC documentation referred to 17 practices because one FAR requirement was split into three mapped objectives. The current requirements cover: authorized system access, authorized functions, external connections, public information, user identification, authentication, media sanitization, physical access, visitor and physical-access controls, boundary protection, separated public-facing systems, flaw remediation, malware protection, malware updates, and system/file scanning.