

Tamzid | Cybersecurity Researcher
Tamzid is a cybersecurity researcher with more than 5 years of experience spanning SaaS, cybersecurity, compliance, and blockchain. He holds certifications in Google Foundations of Cybersecurity, Cisco AI Fundamentals with IBM SkillsBuild, Fortinet NSE 1, and Open Source Intelligence (OSINT) from the Basel Institute on Governance. He writes for Brightlio as well, turning complex security and compliance topics into clear, practical insights supported by primary-source research, verified data, and evidence-based analysis.
Highly Recommended
AICPA’s SOC 2 Proposal Cuts Criteria and Expands AI Coverage
Editorial Note: This working draft uses published analyses for the detailed criteria counts and mappings. AICPA’s proposed…
Areas of Expertise

Penetration Testing
Security Compliance & Frameworks
Endpoint Protection
Cybersecurity Education
More from Tamzid | Cybersecurity Researcher
What is Evidence Collection in Compliance?
Evidence collection in compliance is the process of gathering records that show how your organization…
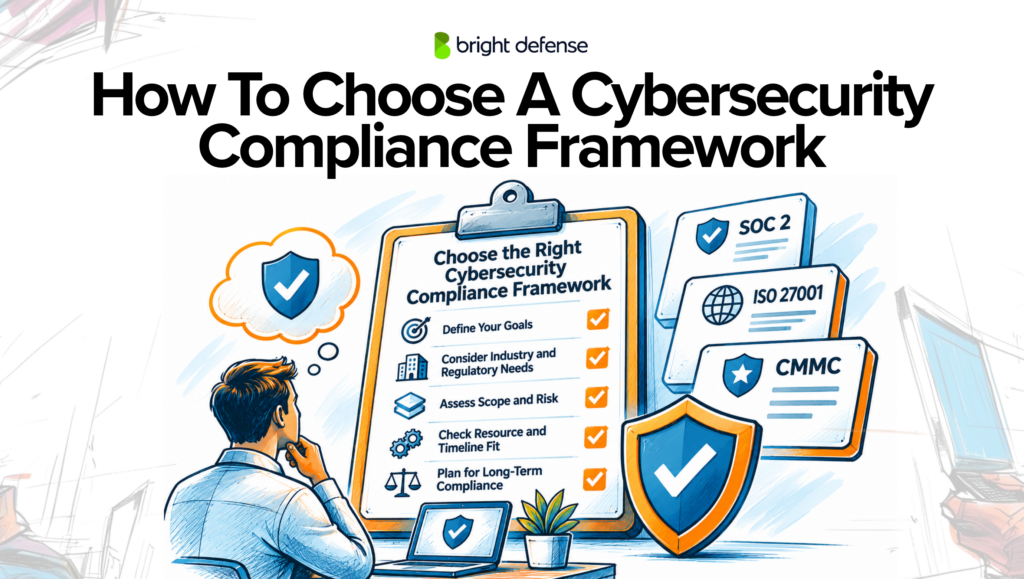
How To Choose A Cybersecurity Compliance Framework
Choosing a cybersecurity compliance framework starts with knowing what your business must prove and who…
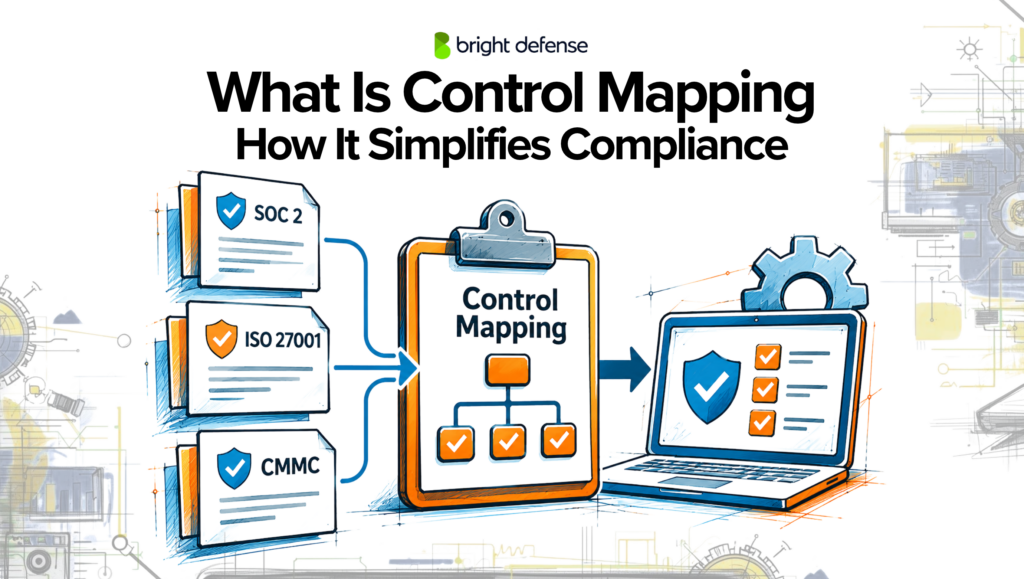
What Is Control Mapping
Control mapping connects security safeguards to the requirements they support. A clear map shows which…