CMMC Level 2 Compliance: A Step-by-Step Strategy Guide
Updated:
September 28, 2026
CMMC Level 2 requires 110 security requirements from NIST SP 800-171 Revision 2 to protect Controlled Unclassified Information (CUI). Defense contractors must implement applicable safeguards, document their operation, and complete the assessment and affirmation requirements specified for their contracts.
This guide explains how to define your assessment scope, evaluate gaps, prioritize remediation, gather evidence, and maintain compliance. Each step connects the requirements to practical actions that help your organization prepare for its Level 2 assessment.
CMMC Levels 1-3: An Overview
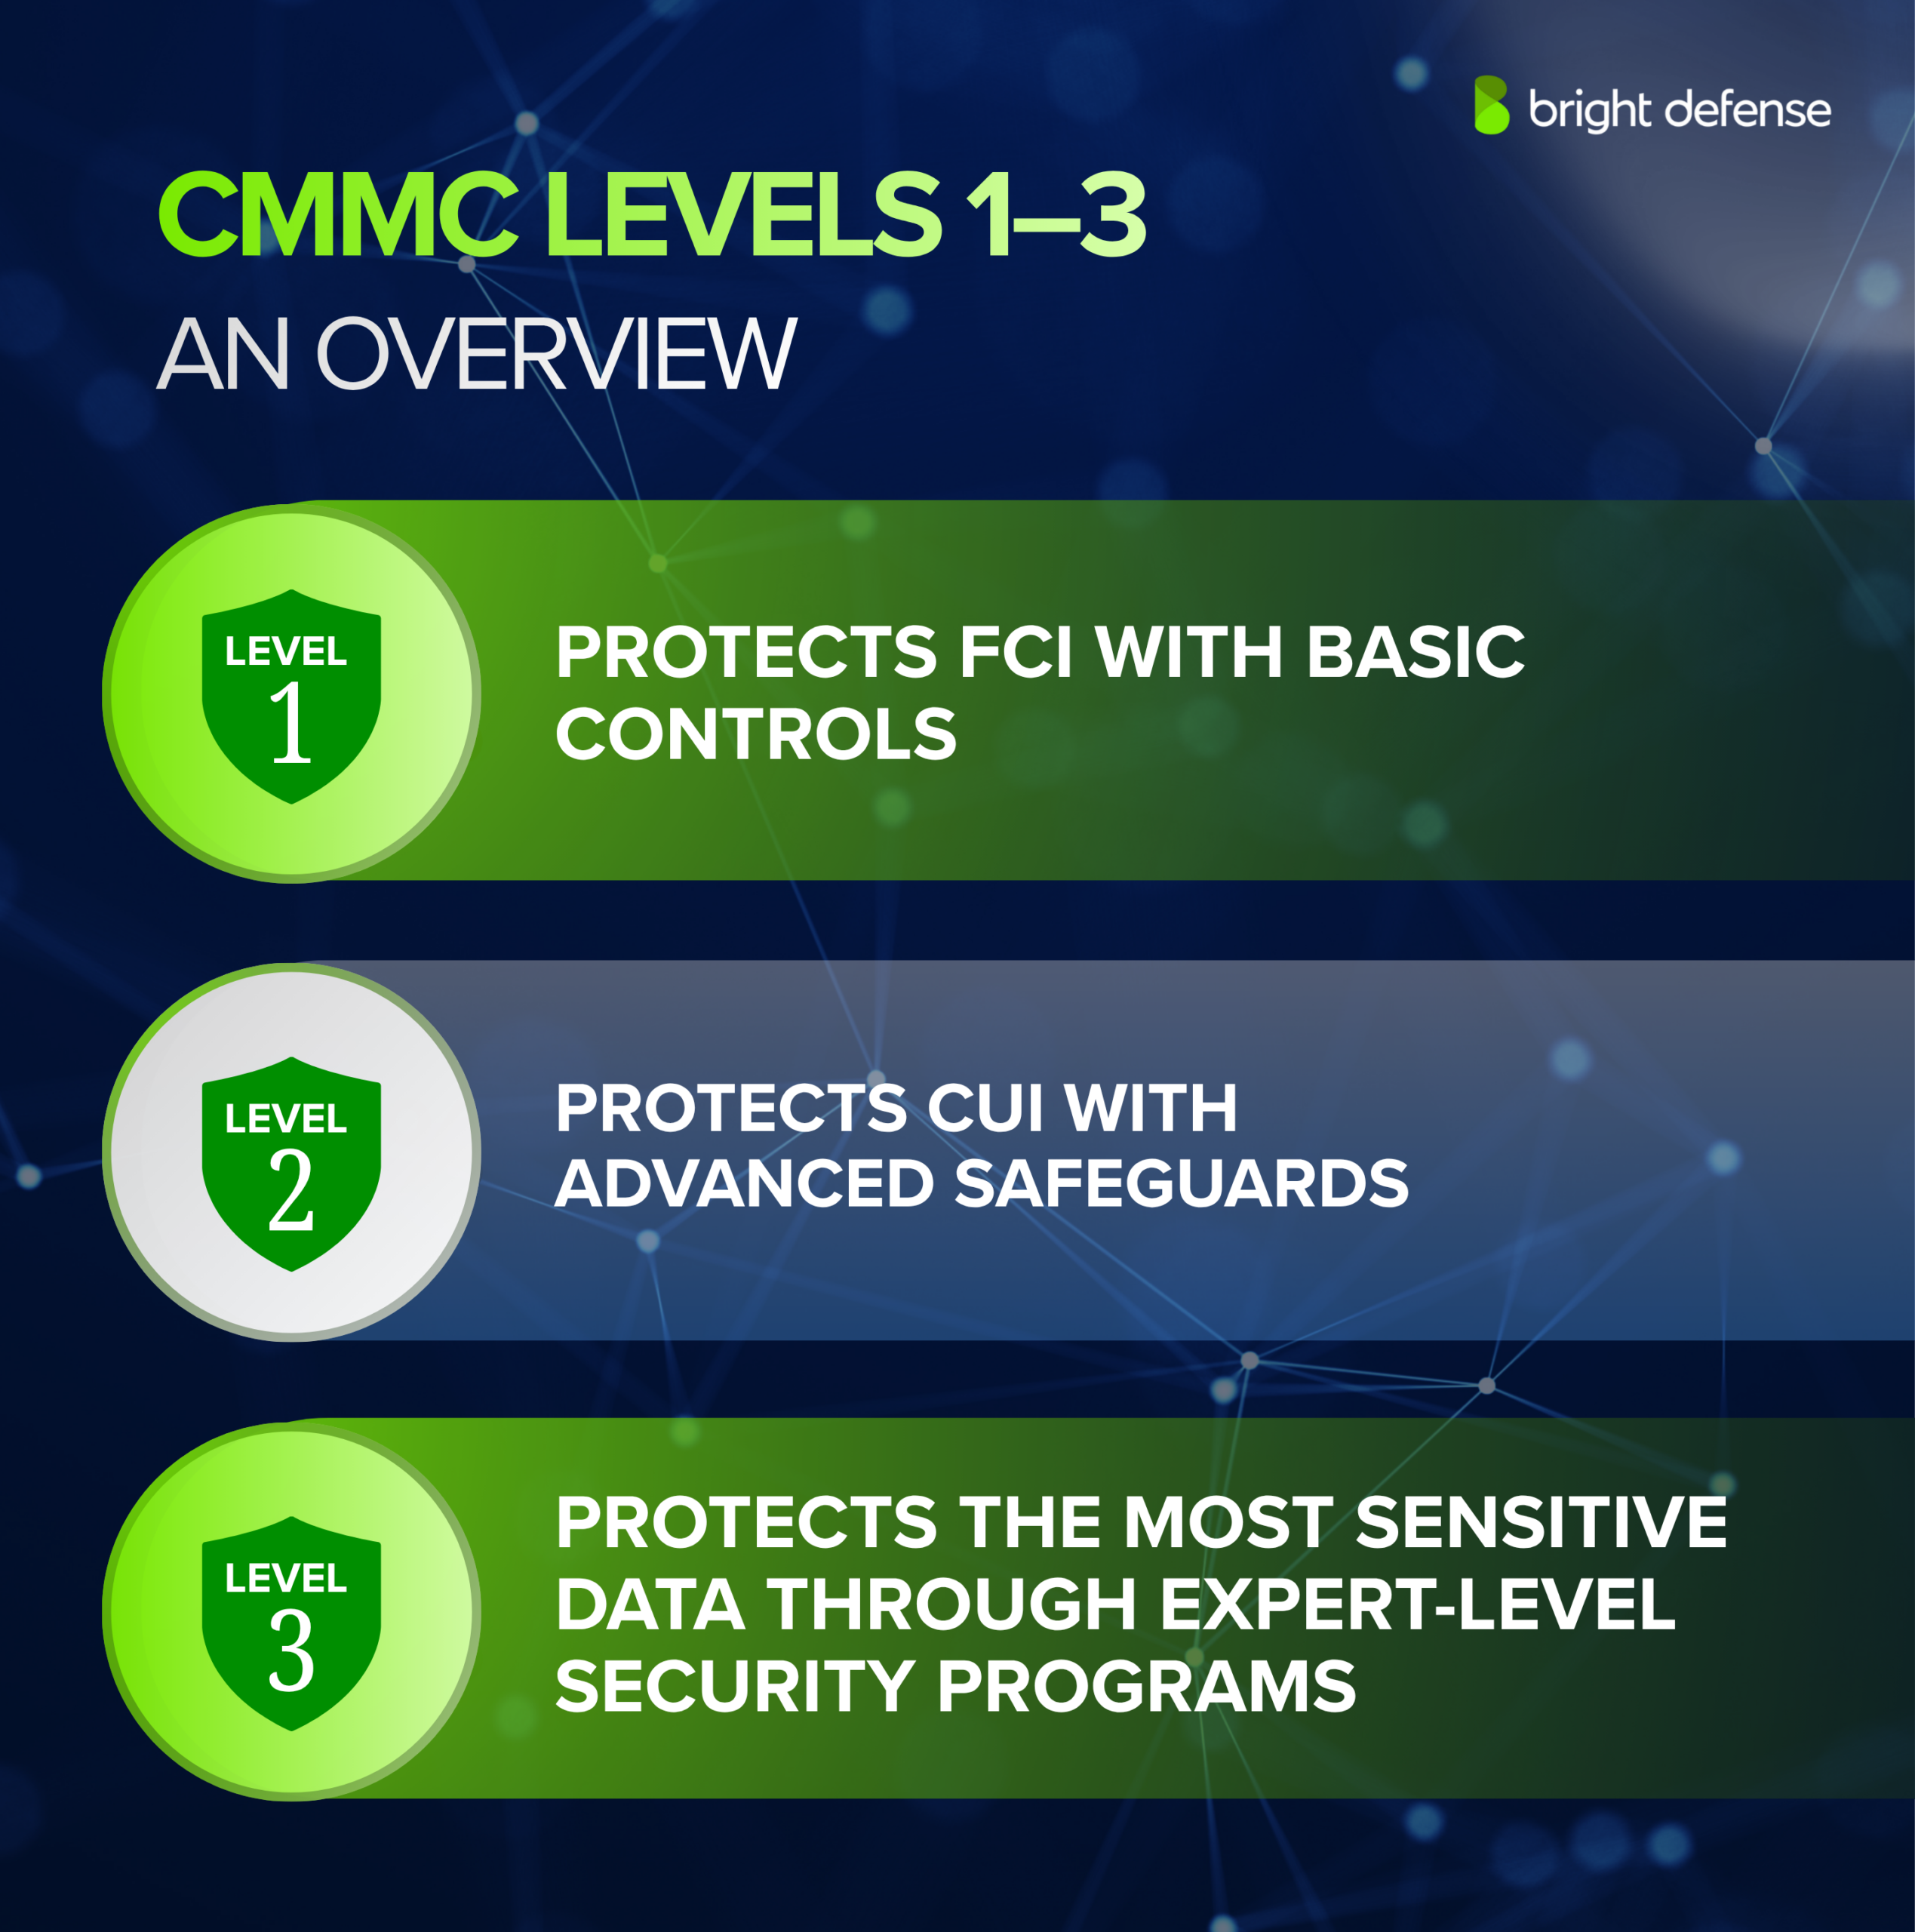
The Cybersecurity Maturity Model Certification (CMMC) program defines three levels of cybersecurity requirements for protecting Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). The required level depends on the information involved and the requirements specified for the contract.
The CMMC framework covers foundational safeguards, protection of CUI, and additional defenses against advanced persistent threats. The following three levels establish different security and assessment requirements.
What is CMMC Level 1: Foundational
CMMC Level 1 protects FCI, which includes nonpublic information provided by or generated for the government under a contract. It covers 15 basic safeguarding requirements from FAR clause 52.204-21, commonly mapped to 17 CMMC practices.
These safeguards require organizations to:
- Restrict system access to authorized users, processes, and devices.
- Verify identities before granting access.
- Control physical access and monitor visitors.
- Protect systems from malicious code and correct system flaws.
- Sanitize or destroy media containing FCI before disposal or reuse.
Level 1 requires an annual self-assessment and an annual affirmation of compliance in the Supplier Performance Risk System (SPRS). Outstanding requirements cannot be deferred through a Plan of Action and Milestones (POA&M).Defense.
What is CMMC Level 2: Advanced
CMMC Level 2 protects CUI through 110 security requirements from NIST SP 800-171 Revision 2. These requirements span 14 security families, including access control, incident response, risk assessment, and security assessment.
Implementation includes the following activities:
- Apply access restrictions and required multifactor authentication.
- Protect CUI during storage and transmission.
- Maintain system configurations and review security logs.
- Establish and test incident response capabilities.
- Maintain a System Security Plan and evidence of control operation.
The CMMC rule provides Level 2 self-assessment and Certified Third-Party Assessment Organization (C3PAO) assessment paths. Both have a three-year assessment cycle and require annual affirmations.tion is capable of protecting CUI and meeting DoD expectations for stronger cyber defense.
What is CMMC Level 3: Expert
CMMC Level 3 adds 24 selected requirements from NIST SP 800-172 to the Level 2 requirements. It addresses advanced persistent threats affecting CUI associated with designated high-priority programs.
Requirements include activities such as:
- Use threat intelligence to inform security decisions.
- Conduct threat hunting and investigate suspicious activity.
- Apply stronger authentication and system isolation measures.
- Test organizational capabilities against advanced attack techniques.
Under the CMMC rule, Level 3 requires a government assessment through the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC) every three years, with annual affirmations. Final Level 2 C3PAO status is a prerequisite for the applicable assessment scope.
Key Components of CMMC Level 2 Compliance
CMMC Level 2 compliance requires implementation of 110 security requirements across 14 domains from NIST SP 800-171 Revision 2 to protect Controlled Unclassified Information (CUI).
These domains cover technical safeguards, personnel responsibilities, and operational procedures. They address areas such as access control, security awareness training, incident response, risk assessment, and system protection.
Organizations must demonstrate that applicable requirements operate within their assessment scope. Documented procedures, system configurations, and evidence of ongoing security activities support this evaluation.
Let’s take a look at some of the CMMC domains:
CMMC Level 2 Domain Overview
CMMC Level 2 contains 14 security domains covering 110 requirements from NIST SP 800-171 Revision 2. These domains address the technical safeguards, personnel responsibilities, and operating procedures needed to protect Controlled Unclassified Information (CUI).
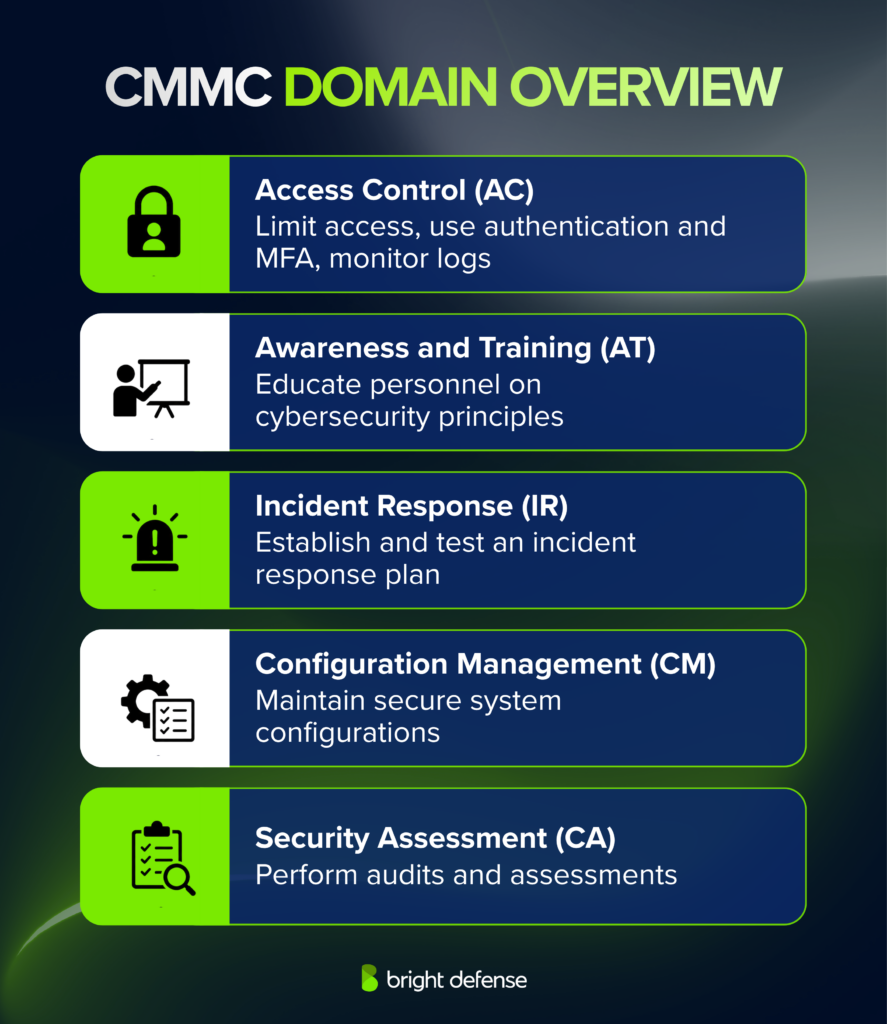
The following 14 domains organize the requirements that organizations must address within their Level 2 assessment scope.
1. Access Control (AC)
Access Control limits system access to authorized users, processes, and devices. Its requirements cover permitted activities, least privilege, separation of duties, remote access, session controls, and restrictions on information flows.
2. Awareness and Training (AT)
Awareness and Training prepares personnel to understand security risks and carry out their assigned responsibilities. Organizations must provide security awareness, role-specific training, and instruction on recognizing and reporting potential insider threats.
3. Audit and Accountability (AU)
Audit and Accountability requires system logs that support monitoring, investigations, and individual accountability. Organizations must review audit records, protect them against unauthorized changes, and address failures in audit logging.
4. Configuration Management (CM)
Configuration Management establishes system inventories, baseline configurations, and controlled changes. Organizations must assess the security impact of changes, restrict unnecessary functionality, and control software installation.
5. Identification and Authentication (IA)
Identification and Authentication verifies users, processes, and devices before granting system access. Multifactor authentication is required for local and network access to privileged accounts and for network access to nonprivileged accounts.
6. Incident Response (IR)
Incident Response establishes capabilities for preparing for, detecting, analyzing, containing, and recovering from incidents. Organizations must track and report incidents to designated officials or authorities and test their response capabilities.
7. Maintenance (MA)
Maintenance controls how systems are serviced and who performs that work. Requirements cover maintenance tools, equipment taken off-site, supervision of unauthorized maintenance personnel, and multifactor authentication for remote maintenance sessions.
8. Media Protection (MP)
Media Protection safeguards paper and digital media containing CUI. Organizations must control access, mark media appropriately, protect it during transport, and sanitize or destroy it before disposal or reuse.
9. Personnel Security (PS)
Personnel Security requires screening individuals before authorizing access to systems containing CUI. Organizations must protect those systems during personnel transfers and terminations, including changes to access permissions.
10. Physical Protection (PE)
Physical Protection restricts access to systems, equipment, and operating environments. Organizations must monitor visitors, maintain physical access logs, manage access devices, and protect CUI at alternative work locations.
11. Risk Assessment (RA)
Risk Assessment addresses risks to organizational operations, assets, and individuals arising from systems that handle CUI. Organizations must assess risk periodically, scan for vulnerabilities, and remediate vulnerabilities according to assessed risk.
12. Security Assessment (CA)
Security Assessment evaluates whether controls operate effectively. Organizations must assess controls periodically, monitor them on an ongoing basis, address deficiencies, and maintain a System Security Plan describing their environment and implementation.
13. System and Communications Protection (SC)
System and Communications Protection safeguards communications and system boundaries. Requirements address network separation, cryptographic key management, protection of CUI confidentiality, and FIPS-validated cryptography when cryptography protects CUI.
14. System and Information Integrity (SI)
System and Information Integrity addresses system flaws, malicious code, security alerts, and unauthorized activity. Organizations must correct flaws promptly, update malicious code protection, conduct required scans, and monitor systems for attacks.
Determining Whether Your Business Needs CMMC Level 2
Your business needs CMMC Level 2 when an applicable defense contract or subcontract specifies that level for systems handling Controlled Unclassified Information (CUI). Handling CUI is a key factor, but your contractual requirements establish the required CMMC status and assessment obligations.
Review the following factors to confirm your obligations:
- Contract Requirements: Check the solicitation, contract, and applicable modifications for the specified CMMC level. Relevant provisions include DFARS 252.204-7025 and clause 252.204-7021.
- Information Handled: Determine whether your systems process, store, or transmit CUI during contract performance. Working with sensitive business information alone does not establish a CUI designation.
- Subcontract Requirements: Review cybersecurity requirements passed down from your prime contractor. The required level depends on the information involved in your subcontract.
- Existing Safeguarding Obligations: DFARS 252.204-7012 can require NIST SP 800-171 safeguards for covered contractor systems. Its presence alone does not establish a CMMC Level 2 assessment requirement.
Businesses handling only Federal Contract Information (FCI) may need Level 1 when specified in their contracts. Confirm unclear data classifications or assessment requirements with the contracting officer or prime contractor before setting your assessment scope.
Factors That Determine Your Need for CMMC Level 2
CMMC Level 2 applies when your defense contract or subcontract requires that status for systems handling Controlled Unclassified Information (CUI). The following five considerations help distinguish contractual obligations from voluntary security improvements.
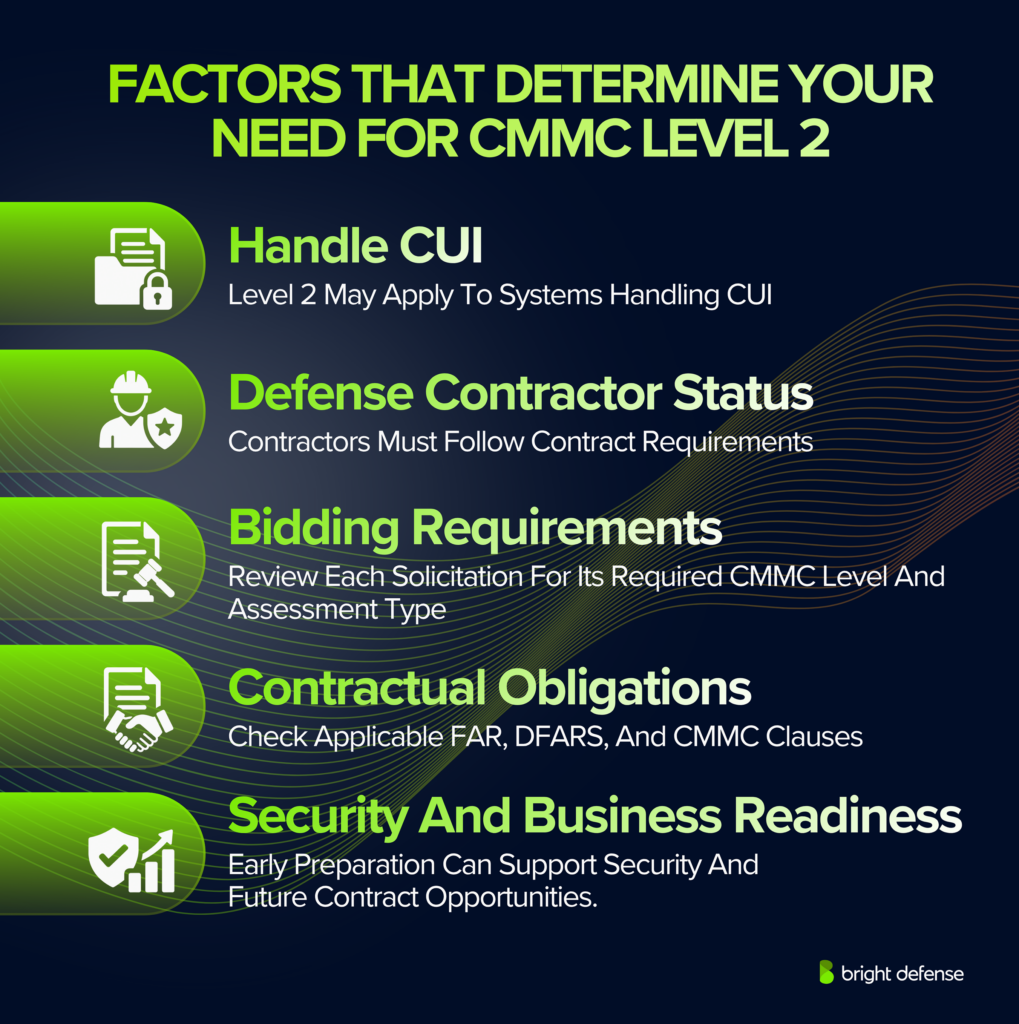
1. Handling Controlled Unclassified Information
CUI is unclassified information created or held for the federal government that requires safeguarding or dissemination controls under applicable laws, regulations, or government-wide policies.
Defense technical data, engineering drawings, manufacturing specifications, and certain personnel records can qualify as CUI. These documents are not automatically CUI simply because they contain sensitive information. Confirm their status through contract documentation, agency guidance, and applicable CUI categories.
2. Working as a Defense Contractor or Subcontractor
Prime contractors and subcontractors may need Level 2 when their work involves CUI and their agreements specify that requirement. Working within the defense supply chain alone does not establish a Level 2 obligation.
Review the cybersecurity clauses and information requirements in your contract. Subcontractors should confirm which obligations the prime contractor passes down for their portion of the work.
3. Preparing to Bid on Defense Contracts
Solicitations specify the required CMMC level and assessment type when CMMC applies. Review these requirements early enough to complete scoping, remediation, and the applicable assessment before the required deadline.
Level 2 is not a universal prerequisite for defense opportunities. Contracts involving only Federal Contract Information may require Level 1, while other contracts have different requirements or applicable exceptions.
4. Meeting Contractual Cybersecurity Requirements
Federal Acquisition Regulation (FAR) and Defense Federal Acquisition Regulation Supplement (DFARS) clauses impose different obligations. DFARS 252.204-7012 addresses safeguarding covered defense information and cyber incident reporting; its presence alone does not establish a Level 2 assessment requirement.
Check the stated CMMC requirements in the solicitation and contract, including applicable provisions, clauses, and modifications. Following NIST SP 800-171 does not automatically establish an official CMMC status.
5. Supporting Security and Business Readiness
Organizations can use Level 2 safeguards to improve access management, incident response, and protection of sensitive information. Preparing early can support future opportunities that require Level 2, although compliance does not guarantee a contract award.
Businesses considering CMMC implementation with PreVeil should evaluate technology alongside their assessment scope, operating procedures, and evidence requirements. A security product alone does not establish compliance.
Practical Steps for Achieving CMMC Level 2 Compliance
Achieving CMMC Level 2 compliance requires a defined assessment scope, implemented safeguards, supporting evidence, and completion of the applicable assessment and affirmation requirements. The following eight steps cover preparation, assessment, and ongoing compliance.
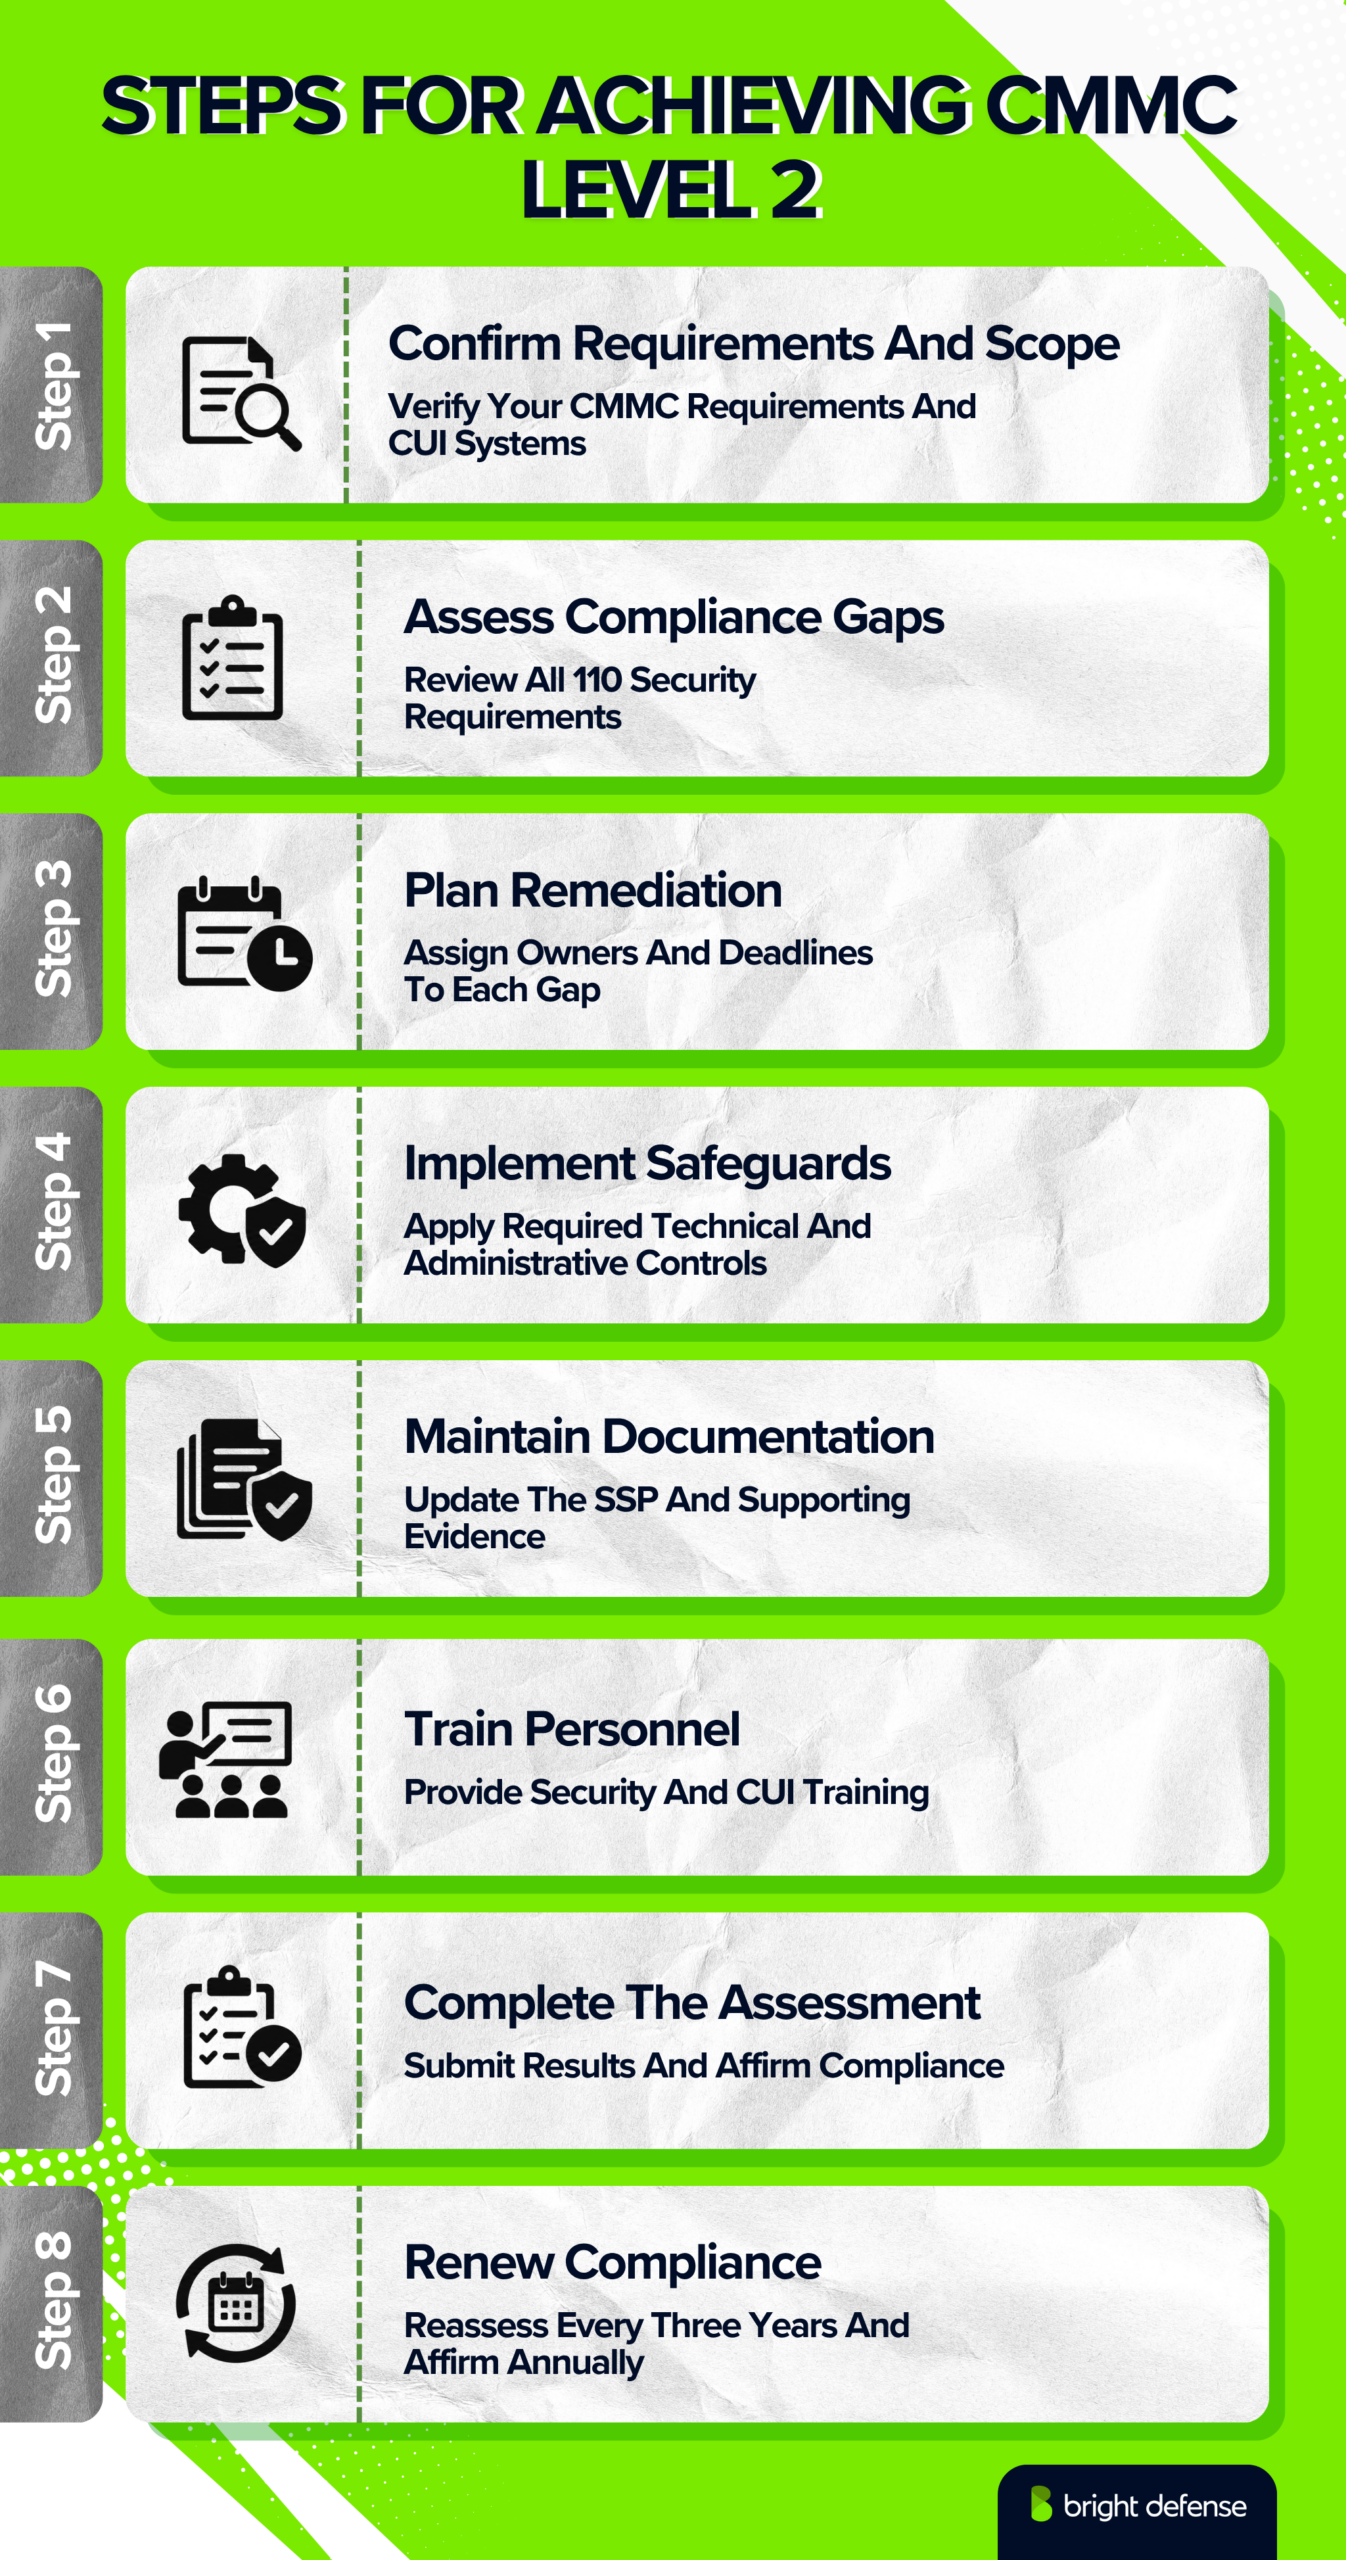
1. Confirm Contract Requirements and Define Your Scope
Review your solicitation, contract, and subcontract requirements to confirm the required CMMC status and assessment type. Account for current implementation guidance and applicable contract modifications.
Define your CMMC assessment scope around the systems that process, store, or transmit Controlled Unclassified Information (CUI), along with relevant security protection assets. Document information flows, system boundaries, and responsibilities shared with cloud providers or managed service providers.
2. Conduct a Gap Assessment
A CMMC gap assessment compares your implementation against the 110 requirements across 14 domains in NIST SP 800-171 Revision 2. Use the official Level 2 assessment guidance and a practical CMMC assessment guide to organize the review.
Examine configurations, interview responsible personnel, and test relevant safeguards. Record missing safeguards and evidence against specific assessment objectives. Internal readiness labels such as “partially implemented” can help track progress, but they do not establish that a requirement is met.
3. Develop a Remediation Plan
Convert each gap into a corrective task with an accountable owner, budget, deadline, and completion criteria. Sequence work around security exposure, assessment consequences, and dependencies between systems or procedures.
An internal remediation plan can track all preparation work. A formal Plan of Action and Milestones (POA&M) supporting conditional CMMC status has separate eligibility restrictions and requires successful closeout within 180 days of the conditional status date.
4. Implement Technical and Administrative Safeguards
Implement the safeguards applicable to your environment, including access restrictions, required multifactor authentication, secure configurations, malicious code protection, and protection of CUI during storage and transmission.
Establish operating procedures for incident response, maintenance, personnel changes, and other required activities. Assign control owners and verify that safeguards work across the assessment scope. Purchasing a tool or approving a policy does not demonstrate effective implementation.
5. Maintain the System Security Plan and Assessment Evidence
Develop and maintain a System Security Plan (SSP) describing system boundaries, the operating environment, implementation of security requirements, and connections to other systems. Update it when changes affect those descriptions.
Organize approved policies, configuration records, logs, training records, and test results against the assessment objectives they support. Resolve inconsistencies between written procedures and actual operations before the assessment.
6. Train Personnel for Their Security Responsibilities
Provide security awareness training, role-specific instruction, and training on recognizing and reporting potential insider threats. Personnel should understand how to handle CUI, report incidents, and follow procedures relevant to their work.
Keep records of training content and completion. Phishing simulations can support awareness efforts, while administrators and other personnel with security duties need instruction specific to those responsibilities.
7. Complete the Required Assessment and Affirmation
Complete the Level 2 assessment required under your applicable contract and current implementation guidance. The CMMC rule provides self-assessment and C3PAO assessment paths; a preparatory gap assessment does not replace either formal process.
Submit self-assessment results to the Supplier Performance Risk System (SPRS), or confirm that certification assessment results are recorded through the appropriate process. A senior affirming official must submit the required affirmation after the assessment, including an applicable POA&M closeout assessment.
8. Maintain Controls and Renew Your Status
Monitor control effectiveness, review access permissions, address vulnerabilities, and update documentation as systems or responsibilities change. Track corrective work through verified completion.
Level 2 requires reassessment every three years and an annual affirmation of continuing compliance. Retain assessment evidence for six years from the CMMC status date and address changes that affect your assessment scope or status.
How Bright Defense Helps:
Bright Defense supports gap reviews, remediation planning, documentation, and ongoing compliance management. Its managed security awareness training service uses KnowBe4 to support employee education and phishing simulations.
Understanding the CMMC Assessment and Certification Process
The CMMC assessment process evaluates whether an organization implements the security requirements for its required level and assessment scope. CMMC Third-Party Assessment Organizations (C3PAOs) conduct Level 2 certification assessments, while contractors conduct self-assessments under the applicable self-assessment pathway.
As of September 2026, the announced Phase 2 suspension remains in effect, while Phase 1 self-assessment requirements continue. Organizations should confirm current contractual obligations before scheduling a certification assessment.
The Role of C3PAOs in Level 2 Certification
C3PAOs evaluate implementation of the 110 requirements in NIST SP 800-171 Revision 2. Their assessment teams examine approved documentation, interview responsible personnel, and test safeguards within the agreed assessment scope.
Assessment findings establish whether requirements are satisfied and whether the organization qualifies for Final or Conditional Level 2 certification status.
Conditional status permits only eligible deficiencies and requires a successful POA&M closeout assessment within 180 days. A readiness review from a consultant does not replace this formal assessment.
C3PAO Authorization and Oversight
C3PAOs must be authorized or accredited by The Cyber AB, the CMMC Accreditation Body, before conducting Level 2 certification assessments. Requirements address assessor qualifications, organizational security, impartiality, quality assurance, and assessment procedures.
Organizations selecting a C3PAO should verify its current status in The Cyber AB’s marketplace and agree on scope, evidence handling, scheduling, and fees. The assessment provider must maintain independence and manage conflicts of interest throughout the engagement.
CMMC Rulemaking Process and Implementation Timeline
CMMC’s program and acquisition rules are finalized, and phased implementation began on November 10, 2025. As of September 26, 2026, Phase 2 remains suspended, while Phase 1 self-assessment requirements continue.
Overview of the Completed Rulemaking Process
The CMMC 2.0 final rule establishes the program under 32 CFR Part 170. It defines the levels, assessment methods, scoring, conditional status, and affirmation requirements. The rule took effect on December 16, 2024.
A separate Defense Federal Acquisition Regulation Supplement (DFARS) rule establishes how CMMC requirements enter solicitations and contracts. That rule took effect on November 10, 2025, starting phased implementation.
Timeline Highlights
| Date | Confirmed Milestone |
|---|---|
| November 2021 | The Department of Defense announces CMMC 2.0, replacing the original five-level model with three levels. |
| December 26, 2023 | The proposed CMMC program rule is published for public comment. |
| August 15, 2024 | The proposed DFARS acquisition rule is published to address contractual implementation. |
| October 15, 2024 | The final CMMC program rule is published. |
| December 16, 2024 | The CMMC program rule takes effect. |
| September 10, 2025 | The final DFARS acquisition rule is published. |
| November 10, 2025 | The acquisition rule takes effect, and Phase 1 implementation begins. |
| July 13, 2026 | The department announces the suspension of Phase 2, originally scheduled for November 10, 2026, and establishes a CMMC reform task force. |
Current Stage and Next Steps
The Phase 2 suspension pauses the planned expansion of third-party assessment requirements. Phase 1 self-assessment requirements remain in place, along with applicable information safeguarding obligations.
Contractors should review current solicitations, contract clauses, modifications, and implementation guidance to confirm their required CMMC status. Preparation should continue through scoping, gap remediation, evidence collection, and completion of applicable assessments and affirmations.
The original November 10, 2026 Phase 2 date should not be treated as an active deadline during the suspension. Future planning should follow confirmed department announcements rather than earlier rollout estimates. integrate CMMC requirements into new contracts.
Contractors should take a proactive approach by aligning their cybersecurity practices with the updated framework to ensure compliance when the CMMC requirements become mandatory.
CMMC Level 2 Compliance Summary
CMMC Level 2 requires implementation of 110 security requirements from NIST SP 800-171 Revision 2 to protect Controlled Unclassified Information (CUI). Preparation includes defining the assessment scope, correcting security gaps, maintaining a System Security Plan, training personnel, and collecting evidence that safeguards operate effectively.
Organizations must complete the assessment required under their contracts and current implementation guidance. Maintaining Level 2 status requires continued control operation, reassessment every three years, and annual affirmations of compliance. Regular reviews help address vulnerabilities and changes that affect security or assessment readiness.
Bright Defense Supports CMMC Readiness and Continuous Compliance
Bright Defense helps defense contractors prepare for CMMC Level 1 and Level 2 requirements. Its CMMC Registered Practitioners support gap assessments, remediation planning, documentation, and assessment preparation.
Bright Defense’s continuous compliance service combines expert guidance with automation to organize evidence, track corrective actions, and monitor supported controls. Ongoing reviews help keep your cybersecurity program current as systems and requirements change.
Organizations managing multiple obligations can receive support for SOC 2 readiness, HIPAA compliance, ISO 27001 certification preparation, and PCI DSS requirements.
Contact Bright Defense to discuss your required CMMC level and develop a practical compliance plan.
Frequently Asked Questions
1. Are Subcontractors Required to Be CMMC Certified?
Subcontractors must meet the CMMC level and assessment requirements applicable to their work and contractual flow-downs. A subcontractor handling only Federal Contract Information (FCI) may require Level 1. Handling Controlled Unclassified Information (CUI) can require Level 2, but the assessment type depends on applicable requirements and current implementation guidance.
2. How Many Practices Does CMMC Level 2 Require?
CMMC Level 2 includes 110 security requirements across 14 domains, corresponding to the security families in NIST SP 800-171 Revision 2. These include Access Control, Audit and Accountability, Incident Response, and Security Assessment.
3. What Documentation Is Required for CMMC Level 2?
Organizations need a current System Security Plan (SSP) and evidence supporting applicable assessment objectives. Supporting records include policies, procedures, inventories, network diagrams, configurations, logs, and training records. Plans of action address deficiencies when needed; an outstanding POA&M is not mandatory for every assessment.
4. What Is the Purpose of a POA&M?
A Plan of Action and Milestones (POA&M) records deficiencies, corrective actions, responsibilities, and deadlines. Conditional Level 2 status requires a score of at least 88 out of 110 and compliance with restrictions on eligible deficiencies. A successful closeout assessment must occur within 180 days of conditional status.
5. What Is a CMMC Assessment Scope?
The assessment scope defines the environment evaluated for compliance. Level 2 scope includes CUI assets, security protection assets, contractor risk-managed assets, and specialized assets, with different assessment treatment for each category. Scope must account for relevant service providers and supporting security functions.
6. How Are Assets Categorized in CMMC Level 2?
Level 2 uses five asset categories: CUI assets, security protection assets, contractor risk-managed assets, specialized assets, and out-of-scope assets. Security protection assets are assessed against requirements relevant to their capabilities. Contractor risk-managed and specialized assets have specific documentation and assessment rules.
7. What Is the Role of eMASS?
The CMMC instance of the Enterprise Mission Assurance Support Service (eMASS) receives certification assessment results and supporting metadata from assessors. Results transfer to the Supplier Performance Risk System (SPRS). Organizations retain their assessment evidence; eMASS receives artifact names and hashes rather than serving as the repository for every evidence file.
8. What Does a CMMC Level 2 Assessment Cost?
CMMC Level 2 assessment costs depend on scope, locations, system complexity, assessment type, and provider fees. Request a written quote that separates the formal assessment from readiness consulting, remediation, technology costs, and any closeout assessment. Self-assessments still require staff time and preparation resources.
9. What Evidence Supports CMMC Level 2 Compliance?
Evidence can include approved policies, configuration exports, access reviews, system logs, training records, incident records, and test results. Assessors use document examination, interviews, and testing to evaluate assessment objectives. Evidence must demonstrate actual implementation within the assessment scope.
10. Can Organizations Be Exempt From CMMC?
Some acquisitions, including those solely for commercially available off-the-shelf items, fall outside CMMC contract-clause requirements. Federal systems operated on the government’s behalf are outside the CMMC program’s scope. Handling no CUI does not automatically create an exemption because FCI can trigger Level 1 requirements.
11. When Will CMMC Level 2 Be Fully Enforced?
As of September 2026, Phase 2 remains suspended following the July 13, 2026 announcement, while Phase 1 self-assessment requirements continue. The previously scheduled November 10, 2026 Phase 2 start should not be presented as an active deadline. Contractors must follow current solicitation terms and contract requirements.
12. What Is CMMC Level 2 Compliance?
CMMC Level 2 compliance involves implementing the 110 NIST SP 800-171 Revision 2 security requirements for protecting CUI and satisfying applicable assessment, reporting, and affirmation obligations. Final Level 2 status requires all applicable assessment objectives to be satisfied.
13. What Role Do C3PAOs Play in CMMC Certification?
Authorized or accredited CMMC Third-Party Assessment Organizations (C3PAOs) conduct Level 2 certification assessments. They review evidence, interview personnel, test safeguards, and report findings. Their role differs from consultants performing readiness reviews and from organizations completing Level 2 self-assessments.
14. Why Is a System Security Plan Important?
The SSP describes system boundaries, the operating environment, implementation of security requirements, and connections to other systems. It provides context for assessment and must reflect the current environment. The SSP requirement cannot remain unmet on a POA&M supporting Conditional Level 2 status.
15. What Are the Key Components of CMMC Level 2 Compliance?
Key components include accurate scoping, implementation of 110 requirements across 14 domains, an updated SSP, supporting evidence, and completion of the applicable assessment. Maintaining status requires continuing implementation, required affirmations, and timely reassessment.
16. What Does Incident Response Preparedness Require?
Level 2 requires an operational incident-handling capability covering preparation, detection, analysis, containment, recovery, and user response activities. Organizations must track, document, and report incidents to designated officials or authorities and test their incident response capabilities.
17. How Does CMMC Differ From NIST SP 800-171?
NIST SP 800-171 defines security requirements for protecting CUI in nonfederal systems. CMMC establishes a program for assessing implementation and maintaining a recognized status. Level 2 uses Revision 2 and provides self-assessment and third-party certification assessment paths. NIST SP 800-171 does not itself issue certifications.
18. Who Needs to Comply With CMMC Level 2?
Defense contractors and subcontractors need Level 2 when applicable contractual requirements specify that status for their work involving CUI. The solicitation, contract, subcontract, and current implementation guidance determine the required assessment type and timing.
19. How Often Are CMMC Level 2 Assessments Required?
Level 2 self-assessments and certification assessments operate on a three-year cycle under the CMMC rule. A senior affirming official must submit an affirmation after each applicable assessment and annually thereafter. Annual affirmation does not replace the three-year reassessment.
20. What Happens After an Unsuccessful Level 2 Assessment?
An organization that does not qualify for Final or Conditional Level 2 status must correct deficiencies and complete the necessary assessment process before claiming that status. The 180-day closeout period applies only to qualifying conditional status, not to every unsuccessful assessment.