What Is a POA&M?
Updated:
October 7, 2026
A Plan of Action and Milestones (POA&M) records unresolved security weaknesses and explains how and when they will be fixed, who is responsible, and what resources are needed.
It connects each finding to corrective actions, measurable milestones, scheduled completion dates, and evidence of verified closure.
Security weaknesses can emerge from vulnerability scans, penetration tests, audits, and control assessments. A POA&M gives security teams, management, and assessors a shared record of remediation progress, delays, and remaining risk.
Having a POA&M does not automatically prove compliance or authorize a delay in meeting security requirements. The applicable program, framework, or contract determines which deficiencies are eligible, what deadlines apply, and how closure must be validated.
31% of breaches began with vulnerability exploitation in Verizon’s 2026 Data Breach Investigations Report. A POA&M helps teams track the work needed to address these weaknesses, with a named owner, a deadline, and validation that the fix works.
Key Takeaways
- A POA&M is a structured remediation record for unresolved weaknesses, corrective actions, milestones, resources, and scheduled completion dates.
- Federal Risk Management Framework (RMF), FedRAMP, and CMMC programs formally use POA&Ms; other frameworks may use them as an internal management tool.
- Every item should identify the finding, affected system or requirement, risk, owner, action, milestones, evidence, and current status.
- Remediation work needs a named owner and a realistic scheduled completion date, with approved changes documented when dates move.
- “Work completed” is not the same as “closed.” Closure should follow independent or program-required validation.
- CMMC Conditional Level 2 requires at least 88 of 110 points, permits only eligible items, and requires assessment POA&M closeout within 180 days.
When Is a POA&M Required?
A POA&M is required under some federal security and authorization programs, such as the federal RMF and FedRAMP, which use it to track security weaknesses and corrective work.
CMMC permits POA&Ms only in certain cases. Level 1 does not allow them. The Level 2 and Level 3 assessment rules permit eligible unresolved requirements under conditional status, with successful closeout required within 180 days.
Current contracting directives determine which assessment requirements apply to a procurement.
FedRAMP requirements depend on the applicable pathway and transition rules. Its 2026 consolidated rules distinguish cloud providers’ vulnerability reporting from agency-maintained POA&Ms.
Organizations need to follow the requirements and effective dates that apply to their certification pathway. SOC 2, ISO/IEC 27001, HIPAA, and PCI DSS do not generally prescribe a document called a POA&M.
Organizations can use one internally to track security issues and corrective actions, while meeting each framework’s specific remediation and evidence requirements.
The main formal references are NIST SP 800-53 Rev. 5 control CA-5 for the federal RMF and 32 CFR 170.21 for CMMC assessment POA&Ms.
What Does a POA&M Contain?
A POA&M contains a record of each security weakness and the work needed to correct it. It records who owns the work, when it should be completed, and how closure will be confirmed.
Each entry commonly includes:
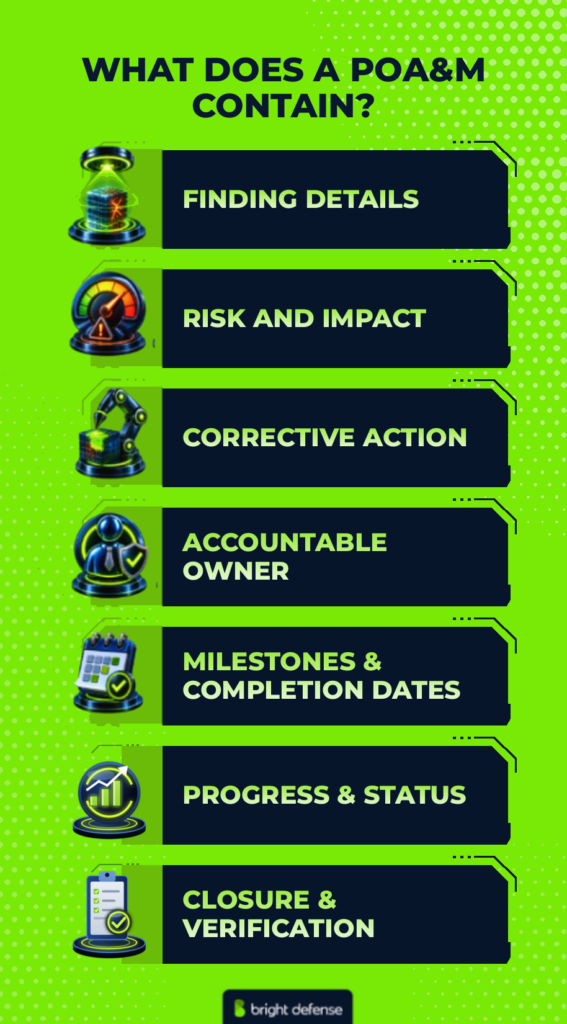
- Finding Details: A unique tracking number, description of the weakness, discovery source and date, affected system or asset, and related control or requirement.
- Risk and Impact: The severity of the weakness, its possible security or operational effects, existing safeguards, and the reason for its remediation priority.
- Corrective Action: The specific changes needed to resolve the weakness, along with required resources, approvals, and dependencies.
- Accountable Owner: One named person responsible for coordinating remediation, with supporting teams listed separately.
- Milestones and Completion Dates: Measurable steps, target dates for each milestone, and a scheduled completion date for the item.
- Progress and Status: Current status, completed work, blockers, reasons for schedule changes, required approvals, and the next review date.
- Closure and Verification: Supporting evidence, validation method and result, verifier, actual completion date, and closure approval.
Where applicable, record remaining risk, compensating controls, and authorized risk decisions separately. Keep evidence accessible through linked scan results, change tickets, configuration records, or test reports so reviewers can confirm how the weakness was resolved.
The governing program determines the mandatory fields and format. A general-purpose template can organize the work, but program-specific submissions must follow the applicable requirements.
POA&M Template & Example
A completed POA&M entry shows the original weakness, the corrective work performed, and the evidence supporting closure. It includes completed milestones, validation results, and approval from the responsible authority.
The following general-purpose template is split into planning and closure tables so it remains readable on smaller screens. The two example rows describe the same completed remediation item.
Identification and Remediation Plan
| Field | Details |
|---|---|
| Item | POA&M-001 |
| Affected System | VPN gateway GW-01 |
| Source and Date | Vulnerability scan, August 25, 2026 |
| Weakness and Risk | Critical firmware vulnerability; High risk |
| Corrective Action | Update firmware, restrict management access, and retest |
| Owner and Support | Network Engineering, IT Operations, and Security |
| Milestones | Test August 27; approve August 29; upgrade September 2; retest September 3 |
| Dependency | Approved outage window |
| Scheduled Completion | September 3, 2026 |
| Status | Closed |
Validation, Residual Risk, and Approval
| Field | Details |
|---|---|
| Item | POA&M-001 |
| Closure Evidence | Change ticket CHG-4821, firmware inventory, configuration export, and scan report |
| Validation Result | Scan confirmed the vulnerable firmware was removed. Access testing confirmed administrative network restrictions. |
| Verifier | Security Engineering Manager |
| Completion Date | September 3, 2026 |
| Compensating Controls | Administrative IP allowlist remained active during validation |
| Residual Risk | Low; routine patch monitoring continues |
| Closure Approval | Security Director, September 3, 2026 |
| Next Review | Reopen if the fix regresses or the evidence becomes invalid |
The validation result demonstrates that the corrective action resolved the original finding. Closure follows that verification and approval.
This general-purpose example illustrates an internal security finding. CMMC assessment POA&Ms and other formal submissions require their own eligibility checks, fields, and closeout procedures.
Defense-Specific Template Note
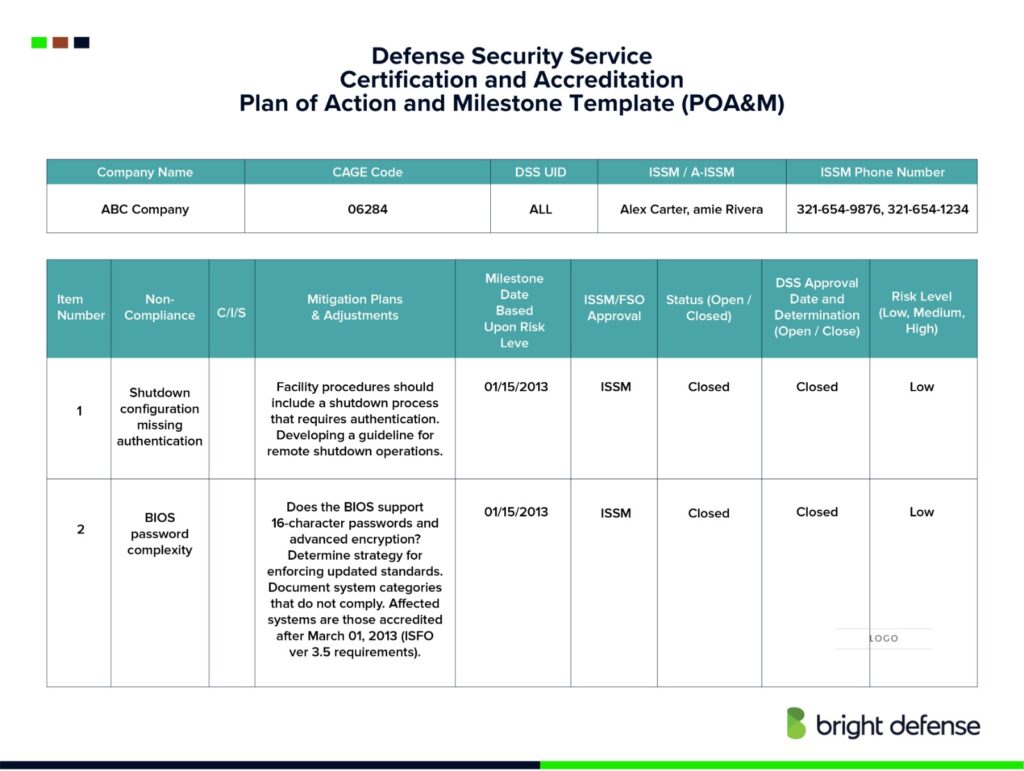
Defense-contractor records may include a Commercial and Government Entity (CAGE) code, Information System Security Manager (ISSM), alternate ISSM, Facility Security Officer (FSO), assessment score, and CMMC status. Those fields are not part of a general business template.
The older download below is a one-page Defense Security Service (DSS) example; DSS was replaced by the Defense Counterintelligence and Security Agency (DCSA), so use it only as a legacy reference and follow current DCSA, CMMC, and contract guidance for present-day work.
How to Create and Maintain a POA&M
To create a POA&M, record each security weakness, assign an owner, and set corrective actions with target completion dates. The following section below provides the complete step-by-step process:
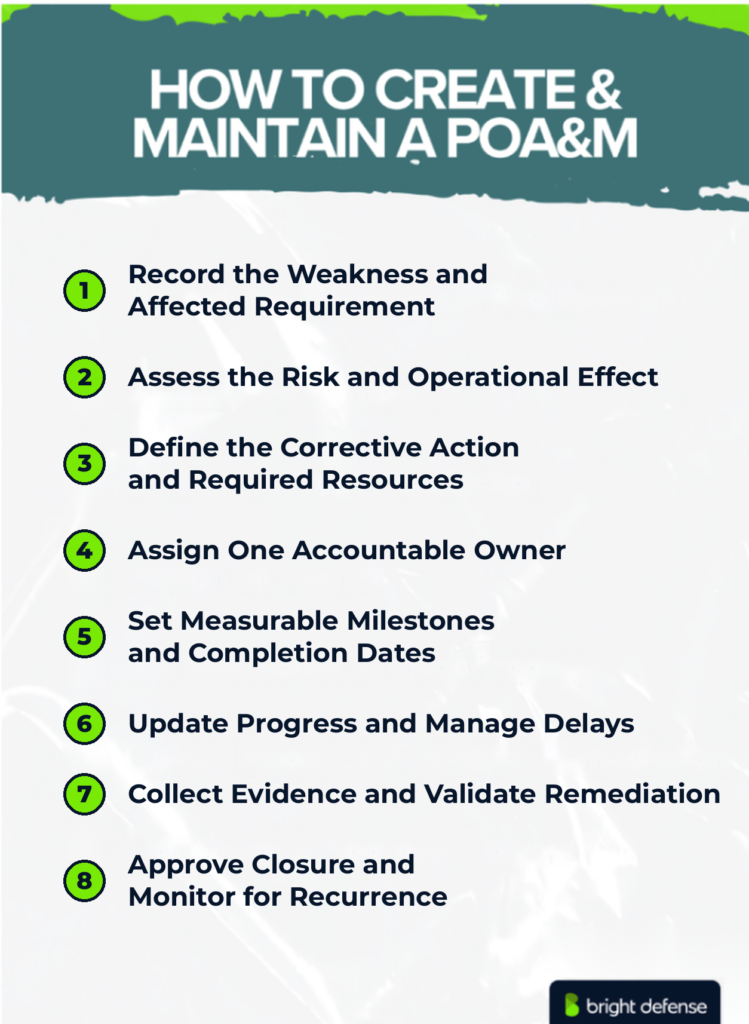
1. Record the Weakness and Affected Requirement
Document the weakness, discovery source, discovery date, affected system or asset, and relevant security control or contractual requirement. Give each entry a unique tracking number so teams can connect it to assessment results, change tickets, and closure evidence.
Describe the specific condition that needs correction. For example, “The VPN gateway’s administrative interface accepts connections from any internet address” gives the remediation owner a clear problem to resolve.
Keep unrelated weaknesses in separate entries. When one finding affects multiple systems, list the affected assets and define the scope of the corrective work.
2. Assess the Risk and Operational Effect
Consider exploitability, exposure, business impact, asset criticality, and existing safeguards. Record how the weakness could affect sensitive information, essential services, or access to critical systems.
Explain the reason for the assigned risk rating. A scanner’s technical severity and the organization’s risk rating can differ because of network exposure, system use, and compensating controls.
Check the governing program before placing an unresolved requirement on an assessment POA&M. Eligibility restrictions and mandatory deadlines take precedence over an internally selected schedule.
3. Define the Corrective Action and Required Resources
State the specific technical, procedural, configuration, access-control, or training changes needed to address the underlying cause. Describe the expected outcome clearly enough for a reviewer to test it later.
For the exposed VPN interface, the corrective action could be to restrict administrative access to the approved management subnet and verify that connections from other networks are blocked.
Record the resources and dependencies needed to complete the work, including:
- Staffing deserves particular attention.
- Software, hardware, or licensing costs.
- Vendor assistance or procurement.
- Change approvals and maintenance windows.
- Testing environments and rollback procedures.
Distinguish temporary safeguards from the final corrective action. Each temporary measure needs a clear purpose and a review point while remediation continues.
In ISC2’s survey, 42% of respondents said CMMC preparation delayed other projects or responsibilities. Our CMMC staffing statistics place that finding alongside other data on contractor budgets and readiness.
4. Assign One Accountable Owner
Name one person accountable for coordinating the item and record the teams responsible for supporting the work. Include the owner’s role so responsibility remains clear when personnel change.
The owner tracks milestones, coordinates dependencies, escalates blockers, and provides evidence for validation. Supporting teams can perform individual tasks, while the primary owner remains responsible for moving the item toward closure.
Assign a verifier and closure approver where the organization’s process requires them. Follow any program-specific requirements for assessor qualifications or independence.
5. Set Measurable Milestones and Completion Dates
Break the corrective action into steps with clear deliverables and target dates. Each milestone needs an observable result, such as an approved configuration, a completed deployment, or a successful retest.
A remediation schedule might include:
- Confirm the affected systems and technical requirements.
- Test the proposed correction.
- Obtain change approval.
- Apply the correction across the affected scope.
- Collect evidence and validate the result.
- Obtain closure approval.
Set the scheduled completion date using the applicable deadline, risk, technical complexity, and available resources. Include time for testing, evidence review, and any required closeout assessment.
6. Update Progress and Manage Delays
Update the entry whenever a milestone, owner, deadline, finding, evidence record, or risk decision changes. Record the latest action, the date of the update, outstanding blockers, and the next review date.
Use Consistent Status Labels
Use the categories required under the governing program. When no prescribed terminology applies, these four statuses provide a clear lifecycle:
| Status | Meaning |
|---|---|
| Open | The weakness has been recorded, but remediation has not started. |
| In Progress | Corrective work is underway. |
| Pending Validation | The corrective action is complete and awaiting verification. |
| Closed | Validation is complete and closure has been approved. |
Record Schedule Changes Separately
When work falls behind, retain the original deadline and record the proposed revised date, reason for the delay, operational effect, and required approval. Include temporary safeguards and the next review date where relevant.
Track a delay separately from the remediation status. An item can remain “In Progress” while awaiting a vendor fix or an approved maintenance window.
Internal approval of a revised date does not extend an external deadline. Escalate missed or threatened deadlines through the process required by the governing program or contract.
7. Collect Evidence and Validate Remediation
Preserve relevant change tickets, configuration records, scan results, test records, screenshots, and approvals. Link each evidence record to the finding and make it accessible to authorized reviewers.
Use a testing method that directly checks the original weakness across the affected scope. For an access-control finding, test that approved users retain access and unauthorized connections are blocked.
Record the validation date, method, result, and verifier. Keep the item open when testing fails or the evidence does not demonstrate that the corrective action worked.
8. Approve Closure and Monitor for Recurrence
Record the actual completion date, validation result, evidence location, and closure approval. Where exposure remains, record the residual risk, existing safeguards, responsible authority, and follow-up actions.
Track any permitted risk-acceptance decision separately from verified remediation. The entry must accurately show whether the weakness was corrected or remains present under an authorized decision.
Retain the closed item and its supporting evidence according to applicable retention requirements. Reopen it when a fix regresses, new evidence invalidates the closure basis, the affected scope expands, or a reassessment shows that the weakness persists.
How Should You Prioritize POA&M Items?
Prioritize POA&M items based on active exploitation, system exposure, business impact, and mandatory remediation deadlines. Address weaknesses that give attackers a direct path to sensitive data or critical systems first.
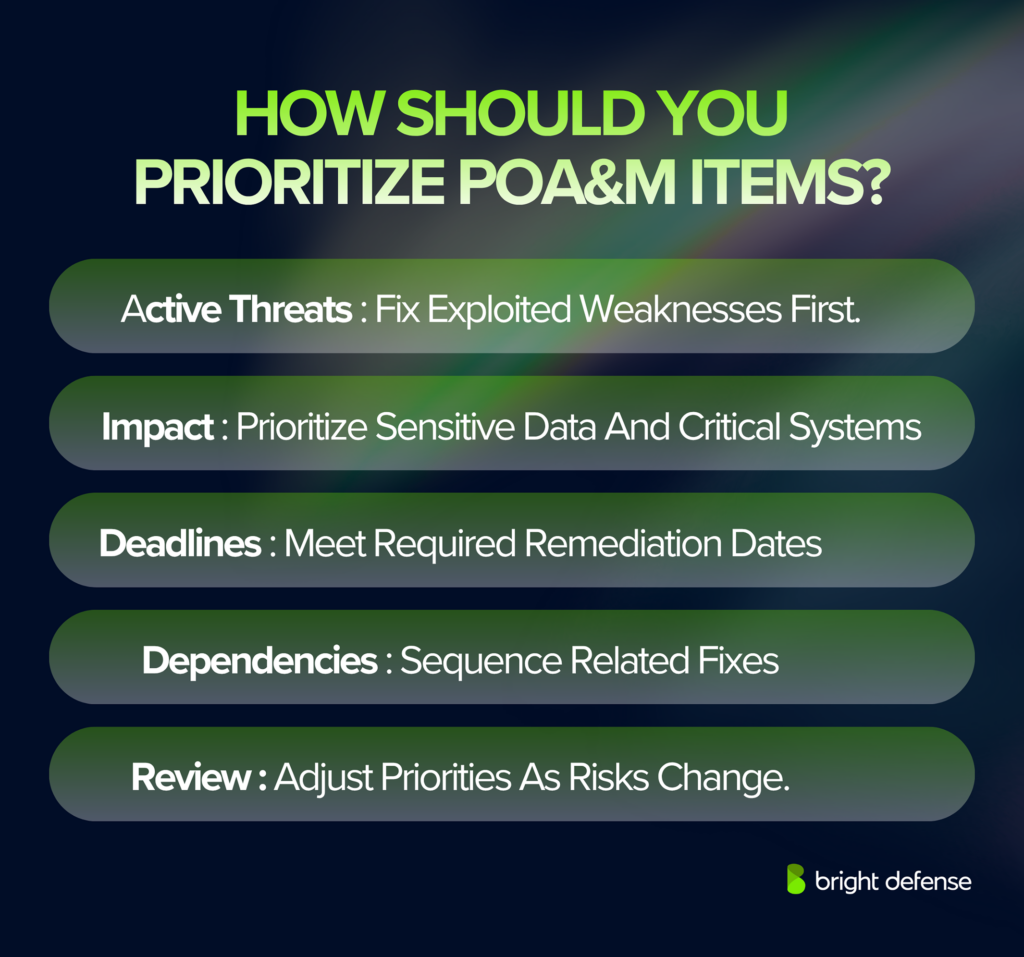
A severity rating provides a starting point. The remediation order needs to reflect how each weakness affects the organization and what obligations apply.
1. Address Active Exploitation and Exposed Systems
Give immediate attention to weaknesses being exploited in your environment. Trigger the incident-response process when exploitation is suspected or confirmed, and use the POA&M to track corrective work that remains.
For other findings, review known exploitation, internet exposure, required attacker privileges, and available safeguards. An exposed remote-access gateway with a known exploited vulnerability warrants greater urgency than a comparable weakness on an isolated test system.
2. Consider Sensitive Data and Business Impact
Assess what an attacker could access, change, or disrupt through the affected system. Prioritize weaknesses involving sensitive information, privileged accounts, essential services, and systems that support business-critical operations.
Record the potential consequences in the entry. “Unauthorized access could expose customer records” gives the owner and approver a clearer basis for prioritization than an unexplained “High” rating.
3. Work Backward From Mandatory Deadlines
Record the applicable program or contractual deadline alongside the internal remediation target. Build milestones that leave enough time for implementation, testing, evidence collection, and required validation.
Keep the earliest binding deadline visible. A long implementation effort needs an early start, especially when procurement, vendor assistance, or an external assessment is involved.
4. Review Safeguards and Dependencies
Existing safeguards can reduce exposure while remediation proceeds. Confirm that those safeguards work, record their limitations, and assign a review date.
Consider dependencies when sequencing the work. Replacing an unsupported identity platform, for example, may enable the team to resolve multiple authentication and access-control findings.
5. Reassess Priorities as Conditions Change
Review priorities when new exploitation information appears, system exposure changes, safeguards fail, or deadlines approach. Record the reason for each priority change and notify the accountable owner.
Use a practical triage order to guide these reviews:
| Priority | Typical Conditions | Response |
|---|---|---|
| Immediate Attention | Active compromise or an imminent threat to critical systems or sensitive data. | Escalate, contain exposure, and begin corrective work. |
| High | Known exploitation, significant exposure, severe business impact, or a near-term mandatory deadline. | Assign prompt milestones and frequent progress reviews. |
| Scheduled | Limited exposure and effective safeguards, with remediation achievable within applicable deadlines. | Schedule corrective work and monitor for changes. |
These categories support internal planning. Apply the governing program’s required ratings and timelines wherever they are prescribed.
How Does a POA&M Differ From an SSP, Risk Register, and Task Ticket?
A POA&M tracks unresolved security weaknesses and the work needed to correct them. A System Security Plan (SSP) describes the system and its security controls, a risk register tracks broader organizational risks, and a task ticket manages individual work activities.
These records serve different purposes and can be linked through finding numbers, control references, and ticket IDs.
| Document | Primary Purpose | Typical Contents |
|---|---|---|
| POA&M | Tracks security weaknesses through remediation and verified closure. | Findings, affected requirements, owners, corrective actions, resources, milestones, deadlines, status, and closure evidence. |
| System Security Plan (SSP) | Describes the system boundary, operating environment, and how applicable security requirements are implemented. | System components, connections, responsibilities, control implementations, and implementation status. |
| Risk Register | Records and monitors risks to organizational objectives. | Risk scenarios, likelihood, impact, risk owners, treatment decisions, existing safeguards, and residual risk. |
| Task Ticket | Assigns and tracks a specific work activity. | Task description, assignee, priority, due date, work notes, attachments, and completion status. |
For example, the SSP describes how administrative access to a VPN gateway is restricted. If a review finds that the interface is exposed to the internet, the POA&M records the deficiency, corrective action, owner, and remediation schedule.
The risk register captures the broader exposure, such as unauthorized access to internal systems. A task ticket assigns the configuration change to a network engineer and records the implementation details.
One POA&M item can link to multiple task tickets for testing, deployment, and validation. Closing an implementation ticket confirms that the assigned work is finished; POA&M closure requires the evidence and approval specified by the applicable remediation process.
How Do POA&Ms Work Under CMMC?
CMMC permits assessment POA&Ms for eligible requirements scored NOT MET when an organization qualifies for conditional status. Level 1 prohibits assessment POA&Ms. Levels 2 and 3 have specific scoring, eligibility, and closeout rules under 32 CFR 170.21.
Current CMMC Contracting Requirements
As of October 4, 2026, the Phase II suspension remains reflected on the official CMMC website. Phase I self-assessment requirements remain in place.
The implementation memorandum limits procurement requirement designations during the suspension to Level 1 (Self) and Level 2 (Self).
It directs amendments removing Level 2 C3PAO and Level 3 DIBCAC requirements from active solicitations. Existing contracts require corresponding modifications before the next option period or during the next scheduled administrative modification.
For contractors facing a Level 2 self-assessment requirement, Conditional Level 2 (Self) is the relevant assessment POA&M pathway. Certification provisions remain in the underlying CMMC regulations, subject to the current implementation restrictions.
Level 1 Restrictions
Level 1 does not permit an assessment POA&M. Contractors must resolve unmet requirements before achieving Level 1 status. An internal remediation tracker can organize that work, but it cannot establish conditional Level 1 status.
Level 2 Scoring and Eligible Requirements
Conditional Level 2 requires at least 88 out of 110 points. Requirements carrying deductions greater than one point are ineligible, except SC.L2-3.13.11: encryption is employed but is not FIPS-validated, resulting in a three-point deduction.
Six requirements are expressly excluded:
- AC.L2-3.1.20 — External Connections.
- AC.L2-3.1.22 — Control Public Information.
- CA.L2-3.12.4 — System Security Plan.
- PE.L2-3.10.3 — Escort Visitors.
- PE.L2-3.10.4 — Physical Access Logs.
- PE.L2-3.10.5 — Manage Physical Access.
Meeting the minimum score is insufficient when an unresolved requirement falls outside these eligibility rules.
The 180-Day Closeout Requirement
For Conditional Level 2 (Self), the organization must correct every requirement on its assessment POA&M, perform a closeout self-assessment, and post the compliance results in SPRS within 180 days of its Conditional CMMC Status Date.
The closeout self-assessment evaluates the previously unmet requirements. Build the remediation schedule to include evidence collection, testing, and submission of results.
Conditional status expires if successful closeout does not occur within the deadline. Expiration can trigger contractual remedies and prevent additional awards requiring the affected CMMC status until a new status is achieved.
Assessment evidence must be retained for six years from the CMMC Status Date.
Under the underlying certification rules, an authorized or accredited C3PAO performs Level 2 certification closeouts, while DCMA DIBCAC performs Level 3 closeouts. These provisions must be read alongside the suspension’s contracting restrictions.
Level 3 Prerequisites and Restrictions
The Level 3 regulatory pathway requires Final Level 2 (C3PAO) status for the systems within the Level 3 assessment scope before the Level 3 assessment begins. DCMA DIBCAC conducts the Level 3 assessment and any required closeout.
Conditional Level 3 requires an 80% minimum score and excludes seven designated requirements from its POA&M. Its separate eligibility rules appear in 32 CFR 170.21(a)(3).
Current suspension guidance prevents requiring activities from designating Level 3 assessments in procurement requirements during the suspension.
Assessment POA&Ms and Operational Plans of Action
An assessment POA&M records eligible requirements scored NOT MET during an assessment. An operational plan of action under CA.L2-3.12.2 addresses temporary vulnerabilities or deficiencies arising after a requirement has been implemented.
Examples include necessary patches, configuration changes, and updates responding to new threats. An unfinished initial implementation does not qualify as a temporary deficiency under this distinction.
The assessment POA&M’s 180-day closeout period does not automatically apply to operational plans. Operational remediation remains subject to applicable security, contractual, and incident-response obligations.
Relevant DFARS Clauses
CMMC assessment requirements operate alongside contractual safeguarding and assessment obligations:
| Clause | Relevance |
|---|---|
| DFARS 252.204-7012 | Covers safeguarding covered defense information and cyber incident reporting. These obligations remain in effect during the suspension. |
| DFARS 252.204-7019 | Establishes notice of the NIST SP 800-171 DoD assessment requirements for applicable procurements. |
| DFARS 252.204-7020 | Addresses NIST SP 800-171 DoD assessments, including government assessment access and cooperation. |
| DFARS 252.204-7021 | Establishes contractor compliance obligations for the CMMC level required by the contract. Its application must account for current deviations and contract modifications. |
The applicable solicitation, contract, and implementing directives determine the contractor’s obligations. A remediation plan needs to reflect those requirements and the assessment pathway that actually applies.
What Mistakes Make a POA&M Unreliable?
A POA&M becomes unreliable when its entries fail to reflect the actual weaknesses, remediation progress, or evidence supporting closure.
Vague findings, unclear ownership, repeatedly postponed deadlines, and unsupported completion claims make it difficult to judge whether risk is being reduced.
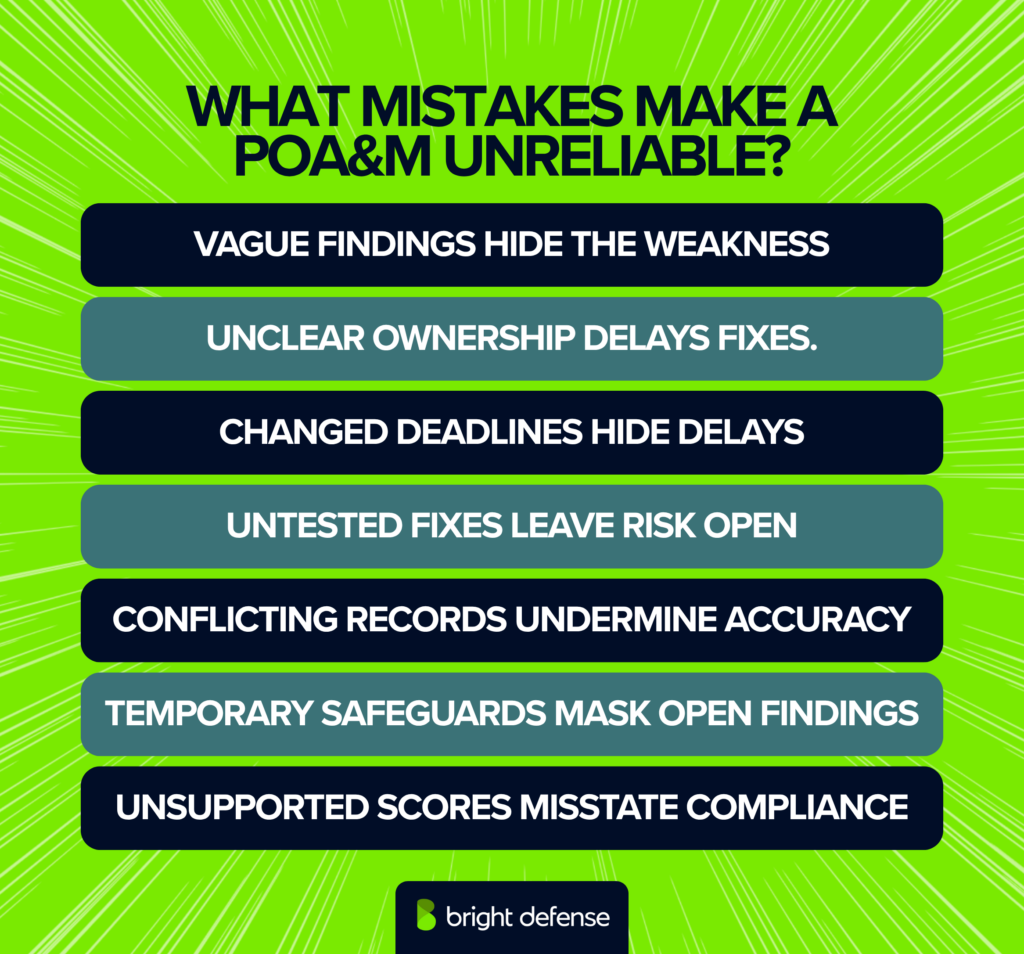
The following seven mistakes weaken a POA&M’s accuracy and make remediation harder to track:
1. Writing Findings That Are Too Vague
Entries such as “Improve access control” leave the affected system, security requirement, and expected outcome unclear. Combining unrelated weaknesses in one entry makes progress harder to measure and can hide unfinished work.
Describe the specific deficiency, affected assets, and condition required for closure. A reviewer needs enough detail to understand what failed and how the correction will be tested.
2. Assigning Responsibility to Multiple Teams
Listing “IT, Security, and Compliance” as the owner leaves accountability uncertain. Tasks can stall when each team assumes another is coordinating the work.
Assign one accountable person and list supporting teams separately. Update ownership promptly when responsibilities change.
3. Moving Deadlines Without Preserving the History
Repeatedly replacing a missed deadline with a new date hides overdue work. A schedule becomes difficult to trust when it omits blockers, dependencies, or the approvals needed to proceed.
Retain the original deadline, record each approved revision, and explain the reason for the change. Escalate delays that threaten an applicable program or contractual deadline.
4. Closing Items Without Testing the Fix
A completed change ticket or an installed product does not establish that the original weakness has been resolved across the affected scope. Testing only one device can leave the same issue open elsewhere.
Keep the item in Pending Validation until the required checks succeed. Record the test result, evidence location, verifier, and closure approval.
5. Allowing Records to Contradict Each Other
An SSP that describes a control as fully implemented can conflict with a POA&M showing that the same implementation remains unfinished. Similar inconsistencies can appear between assessment scores, task tickets, and technical evidence.
Reconcile these records before an assessment or compliance submission. Each record needs to describe the same system scope and accurately reflect the implementation status at the relevant date.
6. Treating Temporary Safeguards as Permanent Resolution
A temporary access restriction or increased monitoring can reduce exposure while corrective work continues. Closing the finding without explaining the remaining weakness conceals unresolved risk.
Record the safeguard, its limitations, and its review date. Keep any authorized risk-acceptance decision distinct from verified remediation.
7. Keeping Scores That the Implementation Cannot Support
The LOGZONE case illustrates the importance of accurate compliance records. LOGZONE submitted a self-assessment score of 110 in SPRS on October 13, 2021. A government Medium Assessment completed on February 2, 2024, produced a score of −170.
On June 18, 2026, DOJ announced a $507,144 settlement resolving allegations involving cybersecurity requirements in two Navy contracts. The resolved claims were allegations, and there was no determination of liability.
For POA&M management, the practical lesson is to reconcile unresolved findings, implementation evidence, and assessment results before submitting a compliance claim. A planned correction must remain distinguishable from a control that is already implemented and validated.
How Does Bright Defense Support POA&M Remediation?
Bright Defense helps organizations assess control gaps, develop remediation plans, organize evidence, and prepare for security assessments.
Our CMMC consulting services include gap analysis, risk assessment, policy development, remediation, and assessment preparation. For defense contractors, that support includes SSP and POA&M preparation and evidence collection.
Our continuous compliance services provide remediation tracking and support, with vCISO guidance to help your team prioritize corrective work and maintain its security program. Engagement scope determines the implementation assistance and deliverables included.
Have unresolved findings or an upcoming assessment? Talk to Bright Defense about your remediation priorities and readiness needs.
Frequently Asked Questions
1. Who Manages a POA&M?
A security, risk, compliance, or system-management lead commonly maintains the overall POA&M. Each item has one accountable remediation owner, with supporting teams listed separately. A qualified reviewer validates the corrective work before closure approval.
2. How Often Must a POA&M Be Updated?
Update a POA&M whenever a finding, milestone, owner, deadline, status, or validation result changes. Formal review frequency depends on the governing program and the risk involved. Set a recurring review schedule that brings overdue items and approaching deadlines to management’s attention.
3. Can a POA&M Deadline Be Extended?
An internal target date can be revised when the governing process permits it and the responsible authority approves the change. Retain the original date, reason for the delay, revised milestones, and approval record. For CMMC assessment POA&Ms, internal approval cannot extend the 180-day closeout period; conditional status expires if successful closeout does not occur on time.
4. Can Risk Acceptance Close a POA&M Item?
That depends on the governing program. Where an accepted-risk disposition is permitted, record the unresolved weakness, approving authority, safeguards, and review date without labeling it as remediated. CMMC assessment POA&Ms require successful closeout assessment; ordinary risk acceptance cannot substitute for meeting the unresolved requirements.
5. Does Every Vulnerability Need a Separate POA&M Entry?
Follow the applicable program’s tracking rules. Where grouping is permitted, findings can share an entry when they have the same underlying weakness, corrective action, owner, and schedule. List every affected asset and retain enough detail to verify remediation across the full scope.
SOC 2 does not prescribe a document called a POA&M. An organization can use one internally to manage control deficiencies, remediation tasks, ownership, and evidence. The organization’s controls and supporting evidence must still satisfy the applicable Trust Services Criteria.
Yes, provided the governing program permits that format. Include the required fields, restrict editing access, preserve version history, and link each entry to its supporting evidence. Assign one person to maintain the master copy so the team works from the same record.
Record the funding gap, required resources, and effect on the remediation schedule. Escalate the issue to the person authorized to approve spending and assess temporary safeguards while funding is arranged. Budget constraints do not automatically extend mandatory deadlines; resources and scheduled milestones remain core parts of the remediation plan.
Keep an internal owner accountable for tracking the vendor’s response. Record the support ticket, expected delivery date, temporary safeguards, and next follow-up date. If the vendor’s timeline threatens your deadline, escalate early and evaluate alternatives such as restricting access, disabling the affected feature, or replacing the component.
Reopen the item or create a linked finding according to your tracking procedure. Preserve the original closure evidence, explain what invalidated it, and reassess the affected scope and risk. Review any assessment results or compliance statements that relied on the earlier closure and follow the applicable correction process.